Privacy-Preserving Machine Learning: Challenges and Opportunities - Invited Talk
Explore privacy-preserving machine learning with Sewoong Oh's invited talk at PPML 2023, covering cutting-edge techniques and advancements in protecting data privacy during ML processes.
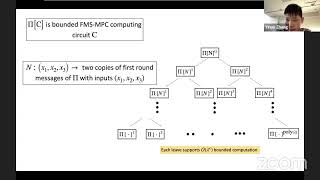
Secure Multi-Party Computation and Secret Sharing - Session 1 and 2
Explore the fundamentals of Multi-Party Computation and Secret Sharing techniques in cryptography, including key concepts, applications, and recent advancements in the field.
Fundamentals of Privacy-Preserving Federated Learning
Explore privacy-preserving techniques in federated learning, focusing on data protection and collaborative model training across distributed datasets.
Chasing Your Long Tails - Differentially Private Prediction in Health Care Settings
Explore differential privacy in healthcare ML, addressing unique challenges, extreme tradeoffs, and fairness considerations for underrepresented groups in medical datasets.
Protect Privacy in a Data-Driven World - Privacy-Preserving Machine Learning
Explore privacy-preserving machine learning techniques to harness AI's power while maintaining data confidentiality, with insights on federated learning, trusted execution environments, and homomorphic encryption.
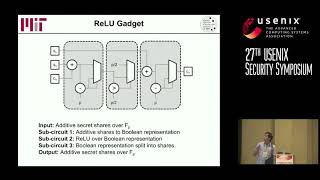
GAZELLE - A Low Latency Framework for Secure Neural Network Inference
Efficient framework for secure neural network inference combining homomorphic encryption and two-party computation, outperforming existing systems in speed while preserving privacy for cloud-based machine learning.
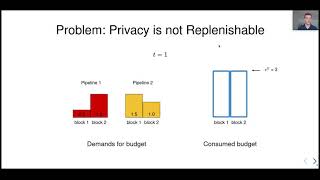
Privacy Budget Scheduling
Explores privacy budget scheduling in machine learning, introducing PrivateKube for managing differential privacy as a resource. Presents DPF algorithm for fair allocation of non-replenishable privacy budgets in ML workloads.
Apache Teaclave - An Open Source Universal Secure Computing Platform in Rust
Explore Apache Teaclave, a Rust-based secure computing platform using Intel SGX for privacy-sensitive data processing, supporting various tasks like machine learning and multi-party computation.
Towards Practical Differentially Private Convex Optimization
Explore practical approaches to differentially private convex optimization, including a novel algorithm and extensive empirical evaluation across various datasets, advancing privacy-preserving machine learning.
Gradient Obfuscation Gives a False Sense of Security in Federated Learning
Explores vulnerabilities in federated learning, demonstrating how gradient obfuscation techniques may not provide adequate privacy protection. Proposes a new attack framework and challenges existing evaluation methods.
PPML 2020 - Welcome and Invited Talk - Contributed Talks
Explore cutting-edge research in privacy-preserving machine learning, including split learning, secure inference, fairness certification, crypto-oriented neural architectures, and privacy-preserving decision trees.
PPML 2020 Session III - Invited Talks
Explore cutting-edge research in privacy-preserving machine learning with talks on cryptography in ML and trustworthy ML, focusing on robustness and privacy.
Connections Between Cryptographic Coin Flipping and Adversarially Robust Learning
Explore the intriguing links between cryptographic coin flipping and adversarial machine learning in this in-depth talk by Mohammad Mahmoody, uncovering insights for robust AI systems.
New Techniques for Efficient Secure Computation
Explore cutting-edge techniques for efficient secure computation with renowned cryptographer Yuval Ishai in this insightful PPML 2021 invited talk.
SecretFlow-SPU - A Performant and User-Friendly Framework for Privacy-Preserving Machine Learning
Explore SecretFlow-SPU, a framework for privacy-preserving machine learning that outperforms existing solutions and simplifies development for users without cryptography expertise.
Practical Privacy-Preserving Machine Learning in Python
Explore privacy-preserving machine learning techniques in Python, including federated learning and encrypted data algorithms, to build accurate models while protecting user privacy.
Information Leakage of Neural Networks
Explore information extraction attacks on machine learning models, their potential to compromise sensitive data, and strategies for mitigation. Gain insights into legal aspects and privacy-security-utility tensions.
Privacy Risks and Protections in Machine Learning Systems
Explore privacy vulnerabilities in ML systems and learn robust protection strategies to safeguard sensitive training data while maintaining system effectiveness and user trust.
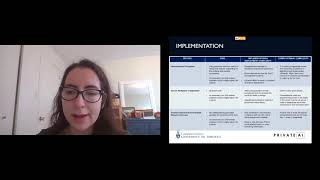
Privacy-Preserving Machine Learning: Strategies and Tools
Explore privacy-preserving machine learning tools and strategies through practical examples, considering risk, implementation complexity, and computational resources.
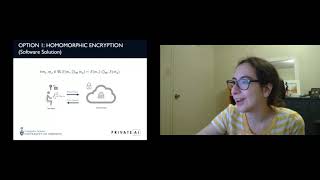
Privacy-Preserving Machine Learning
Explore strategic approaches to privacy-preserving machine learning, including federated learning, encryption, and differential privacy, with practical examples and risk considerations.
Encrypted Computing in Python Using OpenFHE
Explore Fully Homomorphic Encryption (FHE) and its applications in privacy-preserving machine learning. Learn to use OpenFHE's Python interface for encrypted computing, with practical examples and concepts.