Embrace the Red - Enhancing Detection Capabilities with Adversary Simulation
Enhance detection capabilities through adversary simulation techniques. Learn to leverage offensive skills, conduct purple teaming, and test resilience using tools like Password Frame and Empire Spray.
The Rise of the Machines - AI and ML-Based Attacks Demonstrated
AI-based attacks demonstrated: topic modeling for network mapping and email classification. Explores offensive AI/ML applications, their impact on the threat landscape, and potential defensive strategies.
Hacking Your Security Culture for the Cloud
Explore strategies for adapting security teams to cloud environments, focusing on cultural shifts, skill development, and talent acquisition to effectively support cloud adoption.
Understanding and Disrupting Offensive Innovations
Explore key offensive innovations in cybersecurity, their evolution, and strategies to disrupt attackers' advantages. Learn from experts about recent research and future trends in cyber defense.
Powershell and Windows Throw the Best Shell Parties
Explore Windows shell parties with PowerShell, learning combat techniques, configuration, and leveraging PowerShell for enhanced system interaction and security testing.
Voight-Kampff for Email Addresses
Explore email address reputation analysis for identifying spear-phishing and fraud. Learn about EmailRep, a system using OSINT techniques to assess email risk and differentiate real users from attackers.
Abusing Windows Management Instrumentation - WMI
Explore WMI's potential for stealthy, persistent attacks on Windows systems. Learn offensive techniques, backdoor creation, and defense strategies against WMI-based threats.
Offense01 Developers Care and Feeding
Explore best practices for nurturing and supporting developers in offensive security roles, enhancing team productivity and innovation in cybersecurity.
The Ethics of Prosecuting an Offensive Security Campaign
Explore ethical considerations in offensive security campaigns, including impacts on company morale, deception tactics, and maintaining professional integrity. Learn best practices for conducting ethical red team engagements.
Weapons of Text Destruction
Explore the hidden offensive capabilities of Vim for red team engagements. Learn how this popular text editor can be leveraged as a powerful tool in unconventional security operations.
Pages from a Sword-Maker's Notebook Part II
Explore covert intelligence gathering techniques, from anti-virus evasion to counter-intelligence, with practical code examples in Golang. Learn methodologies and technical solutions for long-term surveillance operations.
Weaponized RaspberryPi in Red Team Engagements
Explore weaponized RaspberryPi techniques for red team engagements, enhancing your offensive security skills and understanding of advanced penetration testing methods.
I Hope This Sticks - Analyzing ClipboardEvent Listeners for XSS
Explore ClipboardEvent listeners as potential XSS vectors in web applications. Learn techniques for identifying and exploiting vulnerabilities to enhance your offensive security skills.
Story of an RCE on Apple Through Hot Jar Swapping
Discover how Frans Rosen achieved remote code execution on Apple through hot jar swapping. Learn about the research, exploit, and analysis behind this impressive security finding.
Reversing Web Assembly
Explore techniques for reversing Web Assembly (wasm) in this offensive security talk. Learn key strategies and tools for analyzing and understanding wasm code.
Blackbox Monitoring for Timely Bug Detection
Discover effective blackbox monitoring techniques for timely bug detection in web applications. Learn task-based hybrid approaches, freshness indicators, and risk markers for improved security.
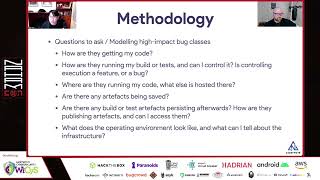
Continuous Intrusion - Hacking CI Systems
Explore techniques for exploiting vulnerabilities in Continuous Integration systems, focusing on security risks and potential attack vectors in the software development pipeline.
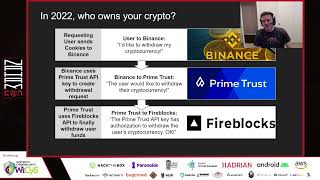
Breaking Into Cloud Wallets - Hacking Crypto Web Apps
Explore cloud wallet vulnerabilities and crypto web app hacking techniques in this talk by @samwcyo, covering blind XSS, SQL injection, and account takeovers in the cryptocurrency ecosystem.
Effectively Finding Vulnerabilities by Debugging the Source Code
Discover effective techniques for identifying vulnerabilities through source code debugging. Learn to enhance your bug hunting skills and improve your ability to find security flaws in software.
Recon Fundamentals by Example
Explore recon fundamentals through practical examples in this offensive security talk. Learn essential techniques for effective reconnaissance in bug bounty and penetration testing.
Attacking Wide Scopes
Explore techniques for attacking wide-scope targets in bug bounty programs. Learn strategies to identify vulnerabilities and maximize your impact when dealing with extensive attack surfaces.