What I Learnt from a Year of Triaging Bug Bounty Reports
Insights from a year of triaging bug bounty reports, covering key lessons learned, common pitfalls, and effective strategies for successful vulnerability reporting and management.
Go Reverse-Engineering Workshop
Develop specialized skills for reverse-engineering Go binaries, focusing on offensive security tooling. Learn methodologies and disassembler plugins to tackle this challenging language.
Building an Empire with PowerShell
Explore advanced PowerShell techniques for red teaming, including Empire framework, malware motivations, and offensive strategies. Learn about extensibility, staging, and detection methods.
Codecepticon – Building an Obfuscator to Bypass Modern EDR and AV
Explore Codecepticon, an offensive security obfuscator for C#, PowerShell, and VBA. Learn its development process, effectiveness against modern EDR and AV, and real-world applications in Red and Purple Team engagements.
Evolution of Offensive Security
Explore the evolution of offensive security techniques and strategies with industry experts, gaining insights into cutting-edge approaches for enhancing cybersecurity defenses.
Inside the Mind of a Threat Actor - Beyond Pentesting
Explore the distinctions between pentesting and red teaming, delving into tools, techniques, and career paths. Gain insights on becoming a red team operator and valuable resources for professional growth.
Techniques for Command Line Obfuscation
Explore advanced cmd.exe obfuscation techniques used by threat actors, including string manipulation and encoding methods. Learn about a new framework for payload obfuscation and its detection implications.
Local Privilege Escalation in 2016
Explore techniques for local privilege escalation on Windows and Unix systems, learning how to elevate user privileges to gain full system access in various scenarios.
E'rybody Gettin' TIPC - Demystifying Remote Linux Kernel Exploitation
Demystifying remote Linux kernel exploitation through a stack overflow vulnerability in a network module, offering insights into the exploit development process and low-level kernel internals.
How to Defeat EDRs in Usermode
Explore advanced techniques to bypass Endpoint Detection and Response (EDR) systems, including PID spoofing, DLL blocking, and syscalls. Learn from experts and get inspired to innovate in cybersecurity.
Summer of Fuzz - MacOS
Explore overlooked attack surfaces on macOS through fuzzing techniques. Learn to bypass security protections, debug effectively, and use new tools for crash triage in Apple core apps and services.
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
Explore a Safari exploit chaining six vulnerabilities to compromise the macOS kernel. Learn about offensive security research and browser-based kernel exploitation techniques.
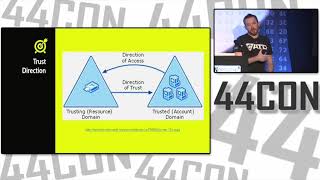
Trusts You Might Have Missed
Demystifying domain trusts: Enumeration, visualization, and exploitation techniques for red teams. Learn to leverage trust relationships for domain takeover without exploits.
CyberRange - An Open-source Offensive Security Lab In AWS
Learn to create a private AWS security training lab using SecDevOps-Cuse/CyberRange. Explore automation, vulnerability management, and offensive security in a safe cloud environment.

Red Team Yourself - Thomas Richards
Learn to assess your organization's security through red teaming techniques. Discover threat actors, asset protection, and engagement strategies for comprehensive security program improvement.
Skills for a Red Teamer
Explore essential skills for effective red team operations, including tactics, techniques, and strategies for simulating real-world cyber attacks and improving organizational security.
Beyond EIP
Explore advanced exploitation techniques beyond EIP, including OP sled, return addresses, and encoders. Learn about payloads and stagers for enhanced post-exploitation capabilities.
Third Generation Exploits on NT - Win2k Platforms pt2
Explore advanced exploitation techniques for NT/Win2k systems, focusing on third-generation vulnerabilities and cutting-edge attack methodologies.
Nemesis
Introducing Nemesis: A revolutionary system unifying post-exploitation data for automated processing, enhancing offensive workflows, and enabling data-driven research in cybersecurity.

Dirty Red Team Tricks
Explore devious tactics and advanced techniques for penetration testing and red team operations, enhancing your cybersecurity skills and strategies.
An Anti Forensics Primer
Explore anti-forensics techniques to protect digital evidence, including data hiding, artifact wiping, and trail obfuscation. Learn to safeguard sensitive information from forensic analysis.