Del Monitoreo al SOC, Digo al Socless - Open Source para el Monitoreo & IR Automático
Explora el monitoreo y automatización en seguridad defensiva con herramientas de código abierto, enfocándose en prácticas DevSecOps para mejorar la protección en entornos cloud.
Packagedna - Escaneando el ADN de tu código para detectar acciones maliciosas
Escaneo del ADN del código para detectar acciones maliciosas en el ciclo de vida de aplicaciones, incluyendo tecnologías Cloud. Enfoque en prácticas DevSecOps y análisis de seguridad defensiva y ofensiva.
Demystifying ATM Jackpot
Explore ATM security, anatomy, and attack methods. Learn about physical security, communication standards, and custom solutions. Gain insights into the fascinating world of ATM vulnerabilities and exploitation techniques.
Tales of Red Teaming - Continuous Intrusion Continuous Deception
Explore advanced red teaming techniques for attacking large corporate networks, including compromising deployment systems, backdooring software, breaking out of containers, and exploiting misconfigurations in multi-tenant systems.
K-Rail - A Tool to Manage K8s Securely at Speed
Explore offensive and defensive scenarios in Kubernetes security, and learn about k-rail, a tool for mitigating risks and managing configurations securely at scale.
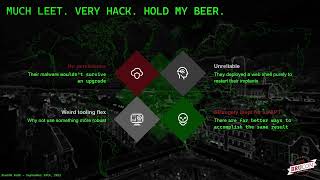
I Am Become Loadbalancer, Owner of Your Network
Explore load balancer vulnerabilities, architecture, and post-breach tactics. Learn about high-profile exploits, device deployment, and how to navigate these critical network components for both offensive and defensive purposes.
New Adventures in Active Defense, Offensive Countermeasures, and Cyber Deception
Explore innovative strategies in active defense and offensive cybersecurity with expert John Strand, uncovering cutting-edge techniques to protect and secure digital assets.
Desired State - Compromised
Explore advanced persistent threat techniques and defensive strategies in this cybersecurity talk by industry experts, focusing on real-world attack scenarios and countermeasures.
Nightmares of a Pentester
Explore real-world challenges and unexpected scenarios faced by penetration testers, offering insights into the complexities of cybersecurity assessments and ethical hacking.
Microservices and FaaS for Offensive Security
Explore offensive security using microservices and FaaS, covering Lambda, Google Cloud, IBM OpenWhisk, and more. Learn practical applications and improvements for cybersecurity projects.
Quick Retooling with .NET Payloads
Explore dynamic .NET implants for red teams, focusing on flexible retooling, OpSec, and overcoming static defenses using DLRium Managed Execution toolkit.
Credential Assessment - Mapping Privilege Escalation at Scale
Explore privilege escalation techniques in large-scale breaches and learn how to identify and combat credential exposure using a comprehensive framework for both offensive and defensive purposes.
I Am AD FS and So Can You - Attacking Active Directory Federated Services
Explore Active Directory Federated Services (AD FS) security, including claims pipeline, tokens, and vulnerabilities. Learn attack techniques, defense strategies, and best practices for securing AD FS deployments.
Offensive Active Directory with PowerShell
Learn offensive techniques for Active Directory using PowerShell, covering user hunting, enumeration, GPO abuse, trust exploitation, and more. Gain practical skills for penetration testing and security assessments.
Racketeer - Prototyping Ransomware Operations - Dimitry Snezhkov - Ekoparty 2021 - Red Zone Space
Explore el diseño e implementación de Racketeer, una herramienta ofensiva para simular y prototipar operaciones de ransomware controladas en entornos empresariales, con enfoque en seguridad y gestión de datos.
IronPython... OMFG - Marcello Salvati - Hack in Paris - 2019
Explore dynamic .NET runtime access using Python, bypassing PowerShell restrictions for stealthy offensive operations in Windows environments.
Modern Secure Boot Attacks - Alex Matrosov - Ekoparty Security Conference - 2019
Explore modern Secure Boot attacks, focusing on bypassing Intel Boot Guard in enterprise systems. Learn about hardware Root of Trust, Embedded Controllers, and UEFI Firmware vulnerabilities.

The Advanced Threats Evolution- REsearchers Arm Race - Alex Matrosov - Ekoparty Security Conference - 2019
Explore the evolution of advanced threats and defensive software, focusing on persistent methods at hardware and firmware levels. Gain insights into modern security gaps and potential solutions.
Exploiting Unknown Browsers and Objects
Discover hidden browser vulnerabilities with the Hackability Inspector, a new offensive toolkit for security researchers to explore and exploit unknown entities in embedded browsers.
Selling 0-Days to Governments and Offensive Security Companies
Explore the intriguing world of vulnerability brokerage, including the process, market dynamics, and ethical considerations of selling 0-day exploits to governments and security firms.
The Answer to Life the Universe and Everything Offensive Security
Explore offensive security through machine learning, sandbox detection, and attack graph theory. Learn about simulation, Q-learning, and adversarial attacks in this comprehensive overview.