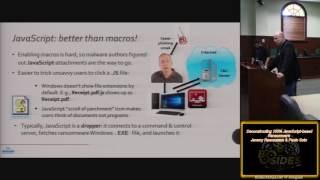
Deconstructing 100 JavaScript Based Ransomware
Explore the inner workings of JavaScript-based ransomware through a comprehensive deconstruction of 100 real-world examples, gaining insights into their mechanisms and potential countermeasures.
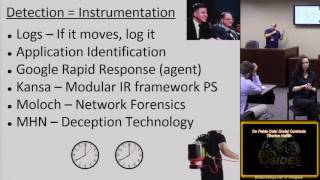
Build the Capability to Detect, Triage, and Respond
Develop skills to detect, triage, and respond to cybersecurity incidents. Learn about defining roles, handling malware, enforcing policies, and improving incident response through practice and failure.
0 to 31337 Real Quick - Lessons Learned by Reversing the Flare On Challenge
Explore reverse engineering strategies and anti-analysis techniques through lessons learned from the Flare-On Challenge, covering file types, encryption methods, and obfuscation tactics.
Playing in Memory - Examples of User Thievery and Hunting for Malware
Explore memory forensics techniques using Volatility and other tools to investigate user activity and hunt for malware in captured system memory.
Reversing a Polymorphic File Infecting Ransomware
Explore techniques for reversing polymorphic ransomware, including file inspection, debugging, and understanding metamorphic code, to enhance malware analysis skills.
Investigating Malware Using Registry Forensics
Explore malware detection and investigation techniques using Windows Registry forensics, covering key hives, detection methods, and tools for uncovering malicious activities.
Dissecting Destructive Malware and Recovering from Catastrophe
Explore destructive malware analysis and disaster recovery strategies with expert insights on encryption, investigation techniques, and effective solutions.
How Stuxnet Ruined My Life For 6 Months But I Got To Fly 1st Class A Lot
Explore the impact of Stuxnet on a cybersecurity professional's life, including unexpected travel perks and challenges faced during a six-month period.
Emotet Banking Malware With A Bite
Explore Emotet banking malware's tactics, impacts, and defense strategies in this comprehensive analysis of a potent cyber threat.
Attacker vs Defender Observations on the Human Side of Security
Explore attacker strategies, defender insights, and the human aspects of cybersecurity. Gain practical knowledge on malware, social engineering, and deception techniques to enhance your security mindset.
Potentially Unnecessary and Unwanted Programs AKA PUPs
Explore potentially unwanted programs (PUPs), their detection challenges, and mitigation strategies through real-world case studies and forensic analysis techniques.
An Open Source Malware Classifier and Dataset
Explore an open-source malware classifier and dataset, learning about innovative approaches to identify and categorize malicious software using machine learning techniques.
How We Reverse Engineered OSXPirrit, Got Legal Threats, and Survived
Dive into the thrilling journey of reverse engineering OSXPirrit malware, facing legal challenges, and emerging victorious in this cybersecurity adventure.
Practical Incident Response in Heterogenous Environment
Explore practical incident response techniques in diverse environments, focusing on mass-triage, RIFT, FRAC, malware analysis, AIOCs, YARA rules, and ClamAV for effective threat detection and forensics.
Malware Mitigation Sample Detonation Intelligence Automation - Make Your Binaries Work
Explore malware mitigation techniques, including sample detonation and intelligence automation, to enhance cybersecurity defenses and streamline incident response workflows.
Analyzing Multi Dimensional Malware Dataset
Explore techniques for analyzing multi-dimensional malware datasets, enhancing threat detection and understanding complex malware behaviors in cybersecurity.
OSXPirrit Reverse Engineering Mac OSX Malware and the Legal Department of the Company Who
Explore reverse engineering of OSXPirrit malware and navigate legal challenges in cybersecurity investigations, gaining insights into Mac-specific threats and corporate legal dynamics.
It's Malware Time - A Bar Crawl from Skunked Homebrew to Rotten Apples
Explore the evolution and techniques of malware, from Skunked Homebrew to Rotten Apples, in this comprehensive analysis of Shlayer and related threats. Learn about distribution methods, sample identification, and attack patterns.
Comparing Malicious Files
Explore techniques for comparing malicious files, including sample identification, shared engines, and various metadata analysis methods to enhance threat detection and incident response.
Its Malware Time - A Bar Crawl from Skunked Homebrew to Rotten Apples
Explore the evolution of malware through real-world examples, from initial infection to advanced techniques. Learn detection and prevention strategies for various attack vectors.
I'll Complete My Threat Model Later Mom - Infosec in Middle School - Ashley Benitez Smith
Explore innovative approaches to teaching cybersecurity concepts to middle school students, focusing on hands-on learning, real-world applications, and age-appropriate content delivery methods.