Mitigating Backdoors in Machine Learning Models - Security and Defense Strategies
Explore techniques for defending against undetectable backdoors in machine learning systems through black-box mitigation strategies, focusing on binary classification and regression models.
Scalable Extraction of Training Data from Production Language Models
Explore techniques for extracting training data from language models, focusing on breaking alignment mechanisms and understanding privacy implications in AI systems.
Securing AI Systems in Real-World Deployments
Explore critical security challenges and defensive strategies for deploying AI systems in production, including insights from running the world's largest AI Red Team and handling emerging threats.
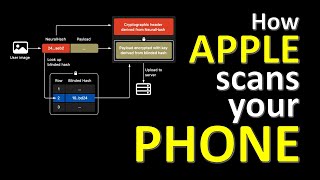
How Apple Scans Your Phone and How to Evade It - NeuralHash CSAM Detection Algorithm Explained
Detailed exploration of Apple's CSAM detection system, analyzing its technical aspects, privacy measures, and potential weaknesses. Covers NeuralHash, private set intersection, and threshold secret sharing.
Privacy and Security of Large Language Models - Risks and Mitigation
Explore security and privacy risks of large language models, including data leaks and adversarial attacks. Learn mitigation strategies and ethical considerations for AI development.
Creating an AI Security and Incident Response Team
Learn to establish and operate an AI Security and Incident Response Team (AISIRT) to address AI/ML system issues, detect problems, and differentiate between various threats.
DevSecOps for AI: Introducing MLSecOps for Software 2.0
Explore MLSecOps for AI-driven software development, addressing security challenges and best practices in the evolving landscape of Software 2.0.
ShellTorch - The Next Evolution in *4Shell Executions
Uncover ShellTorch vulnerabilities in TorchServe, enabling remote code execution and AI model manipulation. Learn about the high-severity exploit's impact on PyTorch ecosystem and essential mitigation strategies.
Invisible Infiltration of AI Supply Chains: Protective Measures from Adversarial Actors
Explore protective measures against adversarial actors infiltrating AI supply chains. Learn to secure data, models, and pipelines, implement security controls, and mitigate risks in AI systems.
Security for AI Basics - Unconventional Strategies and Humor
Explore unconventional AI security strategies through humorous scenarios, from dancing self-driving cars to gossiping chatbots, in this entertaining and informative 101 talk.
DoH Deception: Evading ML-Based Tunnel Detection with Black-Box Attack Techniques
Explore vulnerabilities in ML models for DoH tunnel detection, demonstrating successful evasion techniques and highlighting critical features to avoid in model development.
Considerations on AI Security
Explore key considerations for AI security in this TROOPERS24 conference talk, covering potential risks, vulnerabilities, and strategies for safeguarding AI systems.
OWASP LLM Top 10 - Understanding Critical Security Risks for Large Language Models
Explore OWASP LLM Top 10: Gain insights into critical security risks, learn practical steps to fortify applications, and stay ahead in cybersecurity with expert R Nagarjun.
Generating Synthetic Tabular Data that is Differentially Private
Explore approaches to applying differential privacy in generating synthetic tabular data, including measuring low-dimensional distributions and learning graphical model representations for enhanced data privacy.
Poisoned Pickles Make You Ill - Securing Machine Learning Model Serialization
Explore the security risks of using pickle for ML model serialization and learn strategies to protect against poisoned pickles in data science pipelines.
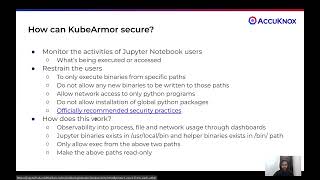
Securing Jupyter Notebooks with KubeArmor
Learn to enhance security for Jupyter Notebooks using KubeArmor, exploring advanced protection techniques for cloud-native environments and data science workflows.
MLSecOps with Automated Online and Offline ML Model Evaluations on Kubernetes
Explore automated ML model evaluations on Kubernetes, focusing on MLSecOps practices for enhanced security and efficiency in both online and offline scenarios.
Untargeted Adversarial Attack on Knowledge Graph Embeddings
Explore advanced techniques for executing untargeted adversarial attacks on knowledge graph embeddings, focusing on privacy and security implications in federated learning environments.
Adversarial Attacks in Deep Neural Networks - Understanding Vulnerabilities and Countermeasures
Explore the world of adversarial attacks in Machine Learning, understanding how malicious inputs can deceive Deep Neural Networks and the ongoing challenges in developing effective defenses.
Trustworthy AI and Cybersecurity Perspectives on Large Language Models - Lecture 32
Explore cybersecurity challenges and trustworthiness concerns in Large Language Models through expert insights on risk assessment, safety measures, and ethical AI development practices.
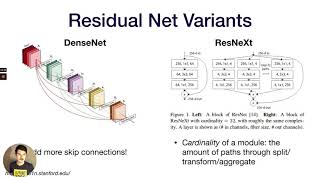
Computer Vision Applications - Full Stack Deep Learning - Spring 2021
Comprehensive overview of deep learning applications in computer vision, covering ConvNet architectures, detection methods, and advanced tasks like 3D shape inference and style transfer.