Extending Kubernetes - Introducing Custom Resources, Controllers, Operators and Schedulers
Explore advanced Kubernetes customization techniques including custom resources, controllers, operators, and schedulers to extend functionality and tailor your cluster for specific use cases.
Application Profiling Made Easy - Prevent Your Kubernetes Clusters from Drowning
Learn techniques to optimize Kubernetes cluster performance through effective application profiling, preventing resource overutilization and ensuring smooth operations.
Cloud Native - Examining Pod Security Admission
Explore Pod Security Admission in Kubernetes, covering baseline profiles, configuration, and enforcement strategies for enhanced container security.
Kubernetes Repositories and Registries Scanning with Kubescape
Explore Kubescape's capabilities for scanning Kubernetes repositories and registries, enhancing security and compliance in cloud-native environments.
The Unexplored World of OpenTelemetry and Service Mesh
Explore the pros and cons of using service mesh tools like Istio for generating traces compared to OpenTelemetry. Learn about sampling, third-party services, implementation, and visualization to make informed decisions.
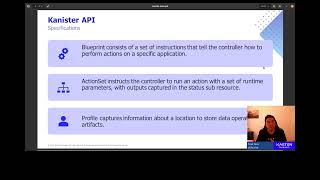
Kanister: Application-Level Data Protection on Kubernetes
Explore application-level data protection for Kubernetes with Kanister, enhancing backup and recovery processes for cloud-native environments.
Cloud Native Live - Kubernetes-Native Pipelines for Stateful Applications
Explore Kubernetes-native pipelines for stateful applications, enhancing cloud-native development and deployment strategies for robust, scalable solutions.
How Attackers Use Exposed Prometheus Servers to Exploit Kubernetes Clusters
Explore how attackers exploit exposed Prometheus servers to gather sensitive information for fingerprinting Kubernetes clusters, and learn strategies to secure your infrastructure against these threats.
KubeVirt v0.53 - New Features for Durability, Security, and Pluggability
Explore KubeVirt v0.53's enhancements in scalability, security, storage, and networking. Learn about new features for high-performance computing, unprivileged VMs, and improved automation for cloud-native virtualization.
Trampoline Pods: Node to Admin Privilege Escalation in Popular Kubernetes Platforms
Explore Trampoline Pods: powerful pods that can enable cluster takeover if compromised. Learn about detection, exploitation, and mitigation strategies for this critical Kubernetes security vulnerability.
containerd - Project Update and Deep Dive
Explore containerd's latest updates, new features, and its role in Kubernetes. Learn about configuration, nerdctl usage, and how containerd is evolving to meet user needs.
Deckhouse Kubernetes Platform: Features and Unique Aspects
Explore the unique features and advantages of the Deckhouse Kubernetes platform, understanding its special attributes for cloud-native applications and infrastructure management.
Creating a Paved Road for Security in Kubernetes Operators
Learn to enhance security in Kubernetes operators by implementing a "paved road" approach, streamlining development and reducing vulnerabilities in cloud-native applications.
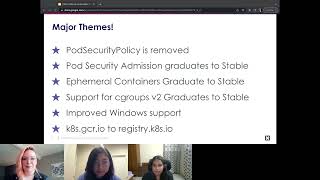
Kubernetes v1.25 Release Overview and Highlights
Explore the latest features and updates in Kubernetes v1.25, including major themes, SIG updates, and key improvements across various components of the container orchestration platform.
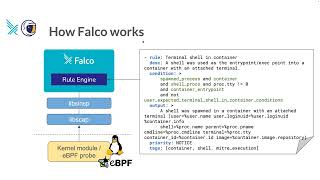
gVisor and Falco - Strengthening Kubernetes and Container Security with Visibility
Explore container sandboxing with gVisor and enhance security monitoring using Falco, improving Kubernetes protection without compromising visibility.
Backing Up Your Kubernetes Strategy - Myths and Facts
Explore myths and facts about Kubernetes backup strategies, addressing downtime costs, storage limitations, and cloud infrastructure challenges while emphasizing the importance of cloud-native data protection.
Managing Thousands of Automatic Machine Learning Experiments with Argo and Katib
Explore best practices for managing large-scale AutoML experiments using Argo and Katib in cloud-native environments, focusing on hyperparameter tuning and workflow orchestration.
Leveraging Argo Workflows and Argo Events for Cloud Agnostic Enterprise Machine Learning Deployments
Explore implementing Argo Workflows and Events for efficient MLOps, including continuous deployment, model retraining, and best practices for cloud-agnostic machine learning pipelines.
Securing GitOps Supply Chain with Sigstore and Kyverno
Learn to secure GitOps supply chain by signing and verifying container images using Sigstore and Kyverno, eliminating security risks and ensuring only trusted images are deployed in Kubernetes clusters.
Harder, Better, Faster, Stronger Pipelines - Improving Continuous Deployment with GitOps
Explore Adobe's journey from Spinnaker to GitOps with Argo, addressing challenges in automated deployment pipelines for multi-region microservices and improving speed, quality, and efficiency.
Secure by Default with GitOps - A Guide to OPA with Argo CD
Learn to integrate Argo CD and Open Policy Agent for secure GitOps practices, enhancing software delivery supply chain security through admission hooks, sync waves, and other strategies.