Securing the Supply Chain: A Practical Guide to SLSA Compliance from Build to Runtime
Dive into SLSA compliance for supply chain security using CNCF tools. Explore GitHub Actions, Cosign, Kyverno, in-toto, and Kubescape to secure software from build to runtime in Kubernetes ecosystems.
Kicking Security Chain Attacks to the Curb with Kyverno and Notary in GitOps
使用Kyverno和Notary等CNCF项目建立容器镜像信任,验证资源,并在GitOps中实施以提高软件供应链安全性。展示如何应对现代Kubernetes部署中的安全挑战。
From Cat to Lion: A Practical Guide to Building Secure, Large-Scale CI/CD Platforms with Tekton
使用Tekton构建安全、可扩展的云原生CI/CD平台,集成Kyverno、ArgoCD和Kubevela等工具。通过实践指导,掌握解决Kubernetes上CI/CD挑战的技能。
Attesting Practically: Exploring the Glue Behind Secure Runtime Environments
Explore practical applications of attestations in software supply chain security, focusing on Cosign, in-toto, and VEX to create secure, auditable runtime environments and effectively manage security threats.
Path to Production: Sustainable Compliance in Strict Environments
Discover strategies for achieving sustainable compliance in highly regulated environments, focusing on DoD practices using Big Bang, Iron Bank, and Kyverno for faster, secure-by-default Kubernetes deployments.
SLSA with Cosign and Kyverno - Securing Software Delivery in Cloud Native Environments
Explore SLSA, Cosign, and Kyverno for enhancing software delivery security in cloud-native environments. Learn practical techniques to safeguard your development pipeline.
SLSA FRSCA Recipe for Secure Supply Chain
Explore an end-to-end solution for software supply chain security using OpenSSF-FRSCA, integrating tools like Tekton, Sigstore, and Kyverno to meet SLSA Level 3 requirements.
How to Secure Your Supply Chain at Scale
Learn how Yahoo secures its software supply chain using open-source tools like Grafeas, Sigstore, and Kyverno. Discover strategies for source code scanning, vulnerability management, and protecting Kubernetes deployments at scale.
Cloud Native - Protecting Software Supply Chains Using Kyverno
Explore Kyverno's role in safeguarding software supply chains, enhancing security practices, and ensuring compliance in cloud-native environments.
Putting the Supply Chain Pieces Together: A Deep Dive into the Secure Software Factory
Explore a deep dive into supply chain security, focusing on implementing CNCF's Secure Software Factory architecture using cloud-native tools to enhance software provenance and artifact trustworthiness.
Hands-on Introduction to Sigstore - Securing the Software Supply Chain
Comprehensive introduction to sigstore, covering container image signing, keyless mode, transparency logs, and image policy enforcement with Kyverno for enhanced software supply chain security.

Securing the Supply Chain: A Practical Guide to SLSA Compliance from Build to Runtime
Practical guide to securing software supply chain using CNCF tools. Covers SLSA compliance, GitHub Actions, Cosign, Kyverno, in-toto, and Kubescape for build-to-runtime security in Kubernetes ecosystems.
Protect the Pipe - A Policy-based Approach for Securing CI/CD Pipelines
Explore a cloud-native security framework for CI/CD pipelines using in-toto, Kyverno, and sigstore. Learn to implement policy-based controls and address unique security challenges in modern application delivery.
Cloud Native Live - What's New in Kyverno
Explore the latest features and updates in Kyverno, the policy engine for Kubernetes, enhancing security and compliance in cloud-native environments.
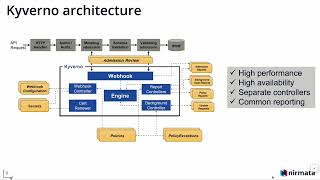
Securely Provisioning Cloud Resources Using Kyverno and Crossplane
Learn to securely provision cloud resources using Kyverno and Crossplane, enhancing your infrastructure management skills and improving cloud security practices.
What's New in Kyverno - Cloud Native Policy Management
Explore the latest updates and features in Kyverno, enhancing Kubernetes policy management and automation for improved cloud-native application security and compliance.
Cloud Governance with Infrastructure as Code Using Kyverno and Crossplane
Explore cloud governance using Crossplane and Kyverno for self-service Kubernetes environments. Learn to automate resource provisioning with compliance checks, ensuring security and cost management standards.
Introducing the BACK Stack - Building an Internal Developer Platform with CNCF Projects
Explore the BACK stack: a composable Internal Developer Platform using Backstage, Argo CD, Crossplane, and Kyverno to empower developers with self-service capabilities and streamlined software delivery.
LFX Mentorship Showcase - Segment 3
Mentees share experiences and projects from LFX Mentorship program, covering OpenBLAS, AMQ Protocol, supply chain security, Kyverno policies, Linux kernel contributions, and personal growth in open source.
Kyverno in Production: Cloud Native Policy Management
Explore Kyverno's capabilities for Kubernetes policy management, including customization, high availability, and monitoring, with practical demos and insights.
GitOps: A Realistic DevSecOps Scenario with Kubernetes and Flux - Lightning Talk
Explore GitOps implementation on Kubernetes using Flux, featuring realistic DevSecOps scenarios, team collaboration, security measures, and monitoring in a dev-to-prod process.