Securing Your Cloud Native Stack with Policy-as-Code and OPA
Explore policy-as-code and OPA for securing cloud-native stacks. Learn implementation strategies and best practices for robust security in modern infrastructure.
Fine-grained Authorization in Containerized Environments Using Open Policy Agent
Explore fine-grained authorization using Open Policy Agent (OPA) for containerized environments, focusing on policy enforcement in Kubernetes without modifying core components.
Comparison of Current Service Mesh Architectures
Explore service mesh architectures, comparing popular options like Envoy, Istio, and Linkerd. Learn key benefits, capabilities, and performance factors to choose the best solution for your distributed applications.
Rust for the Kubernetes Ecosystem - Exploring Advantages and Use Cases
Explore Rust's potential in Kubernetes ecosystem: advantages over Golang, ideal use cases, and real-world examples. Gain insights on building efficient K8s tools and WebAssembly workloads.
Choose Your Own Adventure - The Treacherous Trek to Development
Interactive journey through container development, exploring CNCF projects and key decisions in the path from source code to running application. Audience-driven choices shape the adventure to reach a development environment.
Walk, Jog and Run with Cloud Native and CNCF TAG-Runtime
Explore CNCF's TAG-Runtime projects for cloud-native workloads, focusing on Edge and Batch use cases. Learn about workload management, edge native principles, and future trends in containers, VMs, and WebAssembly.
Operate Multi-Tenancy Service Mesh with ArgoCD in Production
Learn to implement and manage soft and hard multi-tenancy in Istio service mesh using ArgoCD, addressing challenges in configuration, resource consumption, and security for scaled environments.
Multi-Cluster Observability with Service Mesh - Challenges and Solutions
Explore multi-cluster observability challenges with service mesh, focusing on Istio's benefits and limitations. Learn practical solutions using Prometheus Operator and Thanos for effective monitoring.
Multi-Arch Infrastructure from the Ground Up
Explore multi-architecture infrastructure challenges and solutions, covering CI/CD, packaging, Kubernetes, testing, and performance optimization for efficient workload deployment across diverse hardware.
Welcome and Opening Remarks - KubeCon + CloudNativeCon
Opening remarks from CNCF leaders Priyanka Sharma and Chris Aniszczyk, discussing the latest developments and future directions in cloud native computing.
Confidential Containers Made Easy
Learn to provision and run Confidential Containers (CoCo) for cloud-native confidential computing. Explore integration of open-source projects, hardware technologies, and CRI runtimes using a Kubernetes operator for simplified deployment.
From SBOMs to IBOMs - Know What's Happening in Your Clusters
Explore the importance of Infrastructure Bill of Materials (IBOM) in cloud-native environments, its role in security, and how to leverage it for cost optimization and reducing attack surfaces.
Application Configuration Management at the Edge - Taming Thousands of Deployment Targets
Explore challenges and solutions for managing microservice configurations across numerous edge locations, using Carvel tools for efficient Kubernetes deployment and application building.
Cloud Native Live - Linkerd 2.14: Enterprise Multi-Cluster and Gateway API Conformance
Explore enterprise multi-cluster capabilities, Gateway API conformance, and advanced features in the latest Linkerd service mesh update.
Circuit Breakers and Dynamic Request Routing with Linkerd 2.13
Explore dynamic request routing and circuit breakers in Linkerd 2.13, enhancing Kubernetes traffic management and system resilience through practical demonstrations and insights.
Cloud Native Live - What's New in Kyverno
Explore the latest features and updates in Kyverno, the policy engine for Kubernetes, enhancing security and compliance in cloud-native environments.
Graduated Projects Panel - From Sandbox to Graduation in Open Source
Panel discussion on the lifecycle of open source projects, featuring insights from community members of Argo, Flux, Jenkins, and Tekton on their journey to graduation and beyond.
FinOps Observability: Monitoring Kubernetes Cost with OpenCost
Explore FinOps principles and learn to monitor Kubernetes costs using OpenCost. Gain insights into cloud financial management and optimize resource allocation in cloud-native environments.
Run WASM - Shim This Way: Enhancing Container Development with WebAssembly
Explore server-side WebAssembly's potential to enhance developer experience, running alongside containers using familiar technologies like Kubernetes, containerd, and Docker Compose.
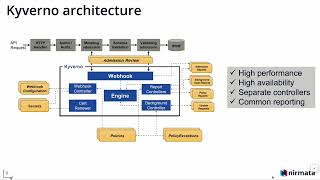
Securely Provisioning Cloud Resources Using Kyverno and Crossplane
Learn to securely provision cloud resources using Kyverno and Crossplane, enhancing your infrastructure management skills and improving cloud security practices.
The Negatives of Per-Host Service Mesh - Sidecar Model as an Ideal Solution for Robust Security
Explore the security implications of per-host service mesh vs. sidecar model in Kubernetes, focusing on proxy footprint, blast radius, and security boundaries for robust and scalable services.