[ko-KR] Safe Kubernetes Environment with AppArmor
AppArmor를 활용하여 Kubernetes 기반 컨테이너 인프라 환경을 안전하게 구축하는 방법 학습. 다양한 예시를 통해 효과적인 애플리케이션 제어 방법 탐구.
Istio Ambient Mesh: Sidecar vs Sidecar-less Explicado de Forma Simple
Explora la diferencia entre modelos Sidecar y Sidecar-less en Service Meshes, enfocándose en Istio Ambient Mesh y sus beneficios para la implementación transparente en Kubernetes.
Docker y Kubernetes - Seguridad 101
Explora los fundamentos de seguridad en contenedores y Kubernetes. Aprende consideraciones críticas para proteger aplicaciones y datos en entornos dinámicos. Amplía tus conocimientos en ciberseguridad.
SSL Hell: Automated Certificate Management for Microservices
Explore automated certificate management for microservices using cert-manager and ACME protocol. Learn to streamline SSL/TLS deployment in Kubernetes environments.
Policy Compliance with Sigstore - From Signing Software to Validating the Whole Software Supply Chain
Explore sigstore for software signing and verification, and learn how to implement policy compliance in cloud-native software build and deployment processes using automation and tools.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Telecom User Group and Cloud Native Network Functions Testbed - Introduction and Deep Dive
Explore the evolution of telecom network functions to cloud-native, discussing challenges, architecture, and performance testing in Kubernetes environments.
Containerizing Your Security Operations Center
Explore containerizing security operations for improved deployment, maintenance, and collaboration. Learn to build a cloud-based SOC using containers, enhancing visibility and streamlining security workflows.
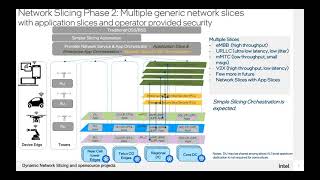
5G Dynamic Network Slicing via Open Source Projects
Explore 5G dynamic network slicing, its business opportunities, and deployment models. Learn about orchestration, automation, and open-source projects contributing to this innovative technology.
Attesting Practically: Exploring the Glue Behind Secure Runtime Environments
Explore practical applications of attestations in software supply chain security, focusing on Cosign, in-toto, and VEX to create secure, auditable runtime environments and effectively manage security threats.
Securing CI/CD Pipelines Through Security Gates
Explore CI/CD pipeline security gates, frameworks, and best practices. Learn to embed security seamlessly in DevOps workflows and eliminate issues before production. Includes live demo.
Lightweight Zero-Trust Network Implementation and Transition with Keycloak and NGINX
Explore lightweight zero-trust network implementation using Keycloak and NGINX, covering JWT validation, OAuth MTLS, and security boundary transitions for enhanced API and service protection.
Apache Kafka and Kubernetes in the Telco Industry for Cloud-Native 5G, MEC and OSS Use Cases
Explore cloud-native solutions for 5G, MEC, and OSS in telecommunications using Apache Kafka and Kubernetes, focusing on data motion and infrastructure modernization.
How Grafana Labs Builds and Sustains Communities
Explore Grafana Labs' strategies for building thriving open-source communities, drawing from decades of experience in fostering collaboration and sustainable growth in large-scale projects.
Automated Cloud-Native Incident Response with Kubernetes and Service Mesh
Explore automated incident response in cloud-native environments using Kubernetes and service mesh. Learn best practices, tools, and techniques for effective security management and threat mitigation.
Filling the Gaps in Kubernetes Flavored SLSA with Threat Modeling
Explore threat modeling for Kubernetes CI/CD security using SLSA standards. Learn to identify and mitigate vulnerabilities in supply chain processes, with practical insights from Tekton's implementation.
DevSecOps Best Practices in Cloud Native Computing - CMCC Case Study
探索中国移动通信公司的DevSecOps最佳实践,了解如何将安全无缝集成到云原生开发和运维流程中,提高效率和安全性。
What Can Go Wrong When You Trust Nobody? Threat Modeling Zero Trust
Explore Zero Trust principles and threat modeling for cloud-native systems. Learn to implement secure architectures using Istio, Kubernetes, SPIRE, and OPA for robust, distributed workload protection.
Path to Production: Sustainable Compliance in Strict Environments
Discover strategies for achieving sustainable compliance in highly regulated environments, focusing on DoD practices using Big Bang, Iron Bank, and Kyverno for faster, secure-by-default Kubernetes deployments.
Software Bill of Materials (SBOM) in Kubernetes - Best Practices and Approaches
Explore SBOM implementation in Kubernetes, comparing approaches and best practices. Learn how Paketo Buildpacks embeds SBOMs in application images using Syft, enhancing software supply chain security.
Putting Hackers Breaching Your Cluster in Automatic Quarantine
Explore automatic isolation techniques for breached apps in Kubernetes clusters, enhancing overall security and minimizing potential damage from hacker intrusions.