Behind the Curtain - Safe Harbor and Department of Defense
Explore legal protections, risks, and trends in vulnerability disclosure with DoD experts. Learn about safe harbor policies, submission processes, and the evolving landscape of bug bounty programs.
From CTF to CVE by Joe Gray
Explore the journey from Capture The Flag challenges to real-world vulnerability discovery, emphasizing skill application, persistence, and responsible disclosure in cybersecurity research.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
Bad API, HAPI Hackers!
Explore API hacking methodology, from information gathering to privilege escalation. Learn techniques for testing vulnerabilities, automating processes, and uncovering critical security flaws in web applications.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Finding Bugs with Binary Ninja by Jordan Wiens
Explore bug-finding plugins for Binary Ninja and learn techniques to extend them for discovering various bug classes in this informative demonstration.
Social Engineering 101 by Matteo Cagnazzo
Discover techniques for gathering company information through OSINT and social engineering. Learn how non-technical methods can complement technical security assessments in bug hunting.
Serverless Top 10 Vulnerabilities by Tal Melamed
Explore serverless security vulnerabilities, their impact, and prevention techniques. Learn how traditional threats evolve in serverless environments and discover best practices for securing cloud-native applications.
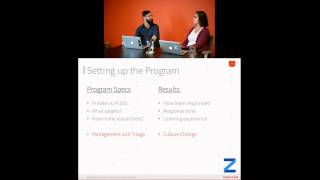
Revitalizing Product Security Through Bug Bounty Programs - Zephyr Health Case Study
Discover how implementing a private bug bounty program transformed Zephyr Health's development culture, motivating teams to prioritize security and leverage crowdsourced expertise.
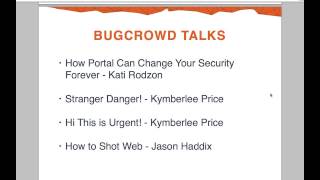
What You Missed During Black Hat and DEFCON - Security Conference Highlights
Explore key highlights from Black Hat and DEFCON, including car hacking, Android security, policy changes, and malware analysis, as presented by Bugcrowd's VP of Operations.
Critical Vulnerabilities and Bug Bounty Programs
Explore critical vulnerabilities uncovered through bug bounty programs, their impact, and strategies for effective vulnerability management and disclosure in cybersecurity.
Hacking with Burp Suite for Bug Bounties - Tutorial 1
Learn essential Burp Suite techniques for bug bounty hunting, including setup and basic functionality, to enhance your web application security testing skills.
Barracuda Bug Bounty Program Evolution - From Inception to Bugcrowd Platform
Explore Barracuda's bug bounty program evolution, from its 2010 inception to current Bugcrowd platform, covering impact, metrics, and rewards for security researchers.
5 Tips for a Successful Bug Bounty Program
Discover key strategies for implementing an effective bug bounty program, including common pitfalls to avoid and expert insights for maximizing benefits and security outcomes.
How the Crowd Outperforms Traditional Security Testing
Explore how crowdsourced security testing outperforms traditional methods, with insights on implementation, benefits, and real-world examples from successful bug bounty programs.
The Art and Value of Bug Bounties
Explore cybersecurity trends, bug bounty myths, and the future of ethical hacking with experts Keren Elazari and Casey Ellis in this informative webinar on the value of crowdsourced security.
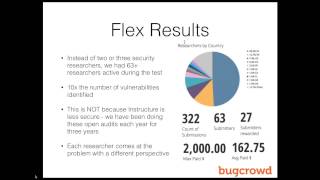
Key Takeaways from Instructure's Bug Bounty Program
Discover insights from Instructure's Bug Bounty program, including their innovative approach to security audits, crowdsourced penetration testing, and key lessons learned for enhancing cybersecurity practices.
How DevOps Becomes DevOpsSec - Chris Raethke, Bugcrowd Webinar
Explore how DevOps evolves into DevOpsSec, integrating security into development processes. Learn strategies for effective implementation and team collaboration.
Finding Bugs with Burp Plugins and Bug Bounty 101
Learn to create automated testing plugins for Burp and explore bug bounty programs. Gain insights on finding vulnerabilities, tips for success, and valuable resources for cybersecurity enthusiasts.
What Is Bug Bounty?
Explore bug bounty basics, including potential earnings, required skills, and benefits for companies. Learn how to get started and what to expect in this comprehensive introduction.
XML External Entity Injection
Learn to identify, exploit, and mitigate XML External Entity (XXE) vulnerabilities. Gain practical skills to enhance application security and protect against data disclosure and system impacts.