Unique Mindset - Hacking Techniques and Favorite Findings
Explore zseano's unique hacking mindset through real-world examples, favorite findings, and insights on identifying critical vulnerabilities in web applications.
Hardware Hacking for the Masses
Explore hardware hacking fundamentals, fields, and affordable entry points. Learn about electronics, UART, JTAG, and car hacking with practical tips and resources for beginners.
GitHub Recon and Sensitive Data Exposure
Learn techniques to locate and identify sensitive data exposed in GitHub repositories, enhancing your cybersecurity skills for ethical hacking and vulnerability assessment.
Bugcrowd University - Advanced Burp Suite
Explore advanced Burp Suite configurations, functionality, and extensions to enhance your web application security testing capabilities and efficiency.
Recon & Discovery
Explore techniques for discovering company assets, including subdomain enumeration, fingerprinting, dorking, and content discovery, to enhance your bug bounty skills.
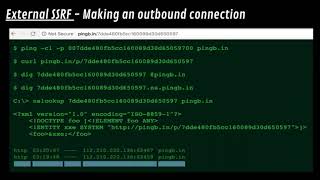
Server Side Request Forgery
Learn to identify, exploit, and mitigate Server-Side Request Forgery vulnerabilities. Covers external and internal SSRF, bypassing blacklists, and includes practical demonstrations and real-world examples.
Car Hacking: A College Student's Perspective - LevelUp 0x04
Explore car hacking techniques, tools, and targets from a student's perspective. Learn about initial access, hardware hacking, and canvas basics for automotive security.
Hacking in Groups: Best Practices for Team Collaboration - LevelUp 0x04
Discover strategies for effective team hacking: finding skilled colleagues, identifying potential teammates, best practices for collaboration, and tools to maximize teamwork efficiency.
LevelUp 0x04 - Blueprint for Becoming a Penetration Tester
Blueprint for aspiring pen testers: expert insights, career tips, and actionable steps to enter the field of ethical hacking and penetration testing.
Fun with Frida on Mobile - Leveraging Dynamic Analysis Tools
Explore Frida for mobile app analysis: trace functions, examine memory, bypass security. Practical examples for iOS and Android, including SSL pinning bypass and custom tool creation.
Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
Group Hacking: A Mini Live-Hacking Event - Discovering Internet-Wide Vulnerabilities
Discover how a small team uncovered a widespread vulnerability across multiple bug bounty programs. Learn strategies for effective group hacking, testing, and reporting in cybersecurity.
OWASP Amass - Discovering Internet Exposure and Network Mapping - LevelUp 0x04
Discover internet-facing assets and enhance network visibility using OWASP Amass. Learn subdomain enumeration techniques and tools for improved cybersecurity and asset management.
LevelUp 0x04 - The Infinite Game of Hacking and Future of Crowdsourced Security
Explore the 'infinite game' of hacking and the future of crowdsourced security with Bugcrowd's CEO Ashish Gupta in this insightful welcome address for LevelUp 0x04.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
LevelUp 0x04 - Introduction to Ethical Hacking and Bug Bounty - Day 1
Explore cutting-edge cybersecurity insights and strategies at this free conference, featuring expert talks and discussions on the latest industry trends and challenges.
Reducing the Cost of Free Speech - The Law and You
Explore legal strategies to protect free speech and reduce associated costs with insights from EFF's Nate Cardozo. Learn about rights, risks, and practical approaches for digital activists and security researchers.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
IoT Security - Attacker's Perspective on Common Vulnerabilities
Explore IoT vulnerabilities from an attacker's perspective, covering famous exploits, OWASP IoT Top10, and practical attack methodologies. Gain insights for both security professionals and IoT developers.
From IVI to CAR in a Box - Building and Testing Automotive Systems
Explore building a simulated car system, from in-vehicle infotainment to a complete "Car in a Box" setup, with insights on ECU integration and safety precautions.
What You Reap, Is What You Sow by Chris Roberts
Explore cybersecurity challenges, industry failures, and potential solutions in an evolving technological landscape. Gain insights on improving security practices and addressing emerging threats.