Profiling the Attacker - Using Offender Profiling in SOC Environments by James Stevenson
Explore techniques for profiling cyber attackers, including asset classification, attack analysis, and motive discernment, to enhance security operations and threat intelligence.
OWASP iGoat - Learning iOS App Penetration Testing & Defense
Explore iOS app hacking and penetration testing techniques using OWASP iGoat, a powerful tool for understanding and improving mobile app security.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
Why Humans Suck at Calculating Risk and How It Affects Security - Masha Sedova
Explore human biases in risk assessment and their impact on cybersecurity decision-making. Learn effective strategies for addressing vulnerabilities and improving organizational security posture.
Bugcrowd University - Broken Access Control Testing
Learn white hat hacking techniques for identifying and exploiting broken access control vulnerabilities, including IDOR, path traversal, and logic flaws, to enhance your bug bounty hunting skills.
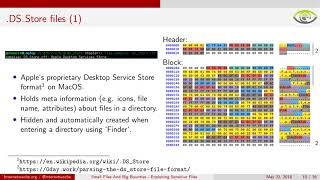
Small Files and Big Bounties - Exploiting Sensitive Files
Explore techniques for exploiting sensitive files to uncover vulnerabilities and earn bounties. Learn from Internetwache team's expertise in identifying and leveraging small but critical files.
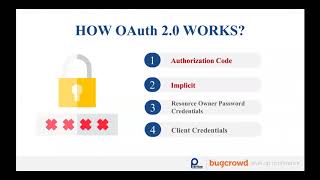
Hacking OAuth 2.0 for Fun and Profit
Discover high-impact vulnerabilities in OAuth 2.0 integrations. Learn attack techniques, methodologies, and case studies for token stealing, code stealing, CSRF, and token impersonation.
Practical Recon Techniques for Bug Hunters & Pen Testers
Discover effective reconnaissance strategies for identifying vulnerabilities and enhancing security assessments in this informative session led by expert Bharath.
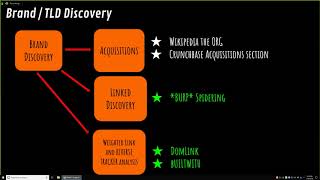
Bug Bounty Hunter Methodology V3
Comprehensive guide to modern bug bounty hunting techniques, covering recon, automation, and vulnerability discovery for web and mobile applications.
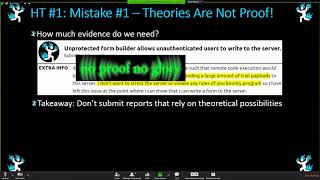
Trickle Down PwnOnomics
Learn how to succeed in bug bounty hunting, from zero experience to consistent earnings, with practical tips and strategies for effective vulnerability discovery and reporting.
Hardware Hacking 101
Introduction to hardware hacking for web and mobile security professionals, covering essential tools, techniques, and protocols like UART, SPI, and JTAG. Hands-on examples and practical insights for beginners.
Back to Basics - Application Security Practices in Smart Contract Auditing
Explore application security practices in smart contract auditing, focusing on Solidity, common vulnerabilities, security tools, and the growing market for blockchain security engineers.
Identifying & Avoiding Android App Protections - Tim Strazzere, LevelUp 2017
Techniques for quickly identifying and bypassing Android app protections to improve bug bounty hunting efficiency and ROI.
MarkDoom- How I Hacked Every Major IDE in 2 Weeks - Matt Austin, LevelUp 2017
Explore web hacking techniques used to exploit major IDEs and desktop applications, revealing high-severity vulnerabilities in popular development tools.
Hacking Internet of Things for Bug Bounties - Aditya Gupta, LevelUp 2017
Discover techniques for finding vulnerabilities in IoT devices, covering firmware, hardware, and radio components. Learn to perform attack surface mapping on commercial smart devices.

Car Hacking 101 - Alan Mond, LevelUp
Explore car hacking essentials: hardware, software, and penetration testing techniques for automotive systems. Learn about attack surfaces, OBD2 ports, and network basics.
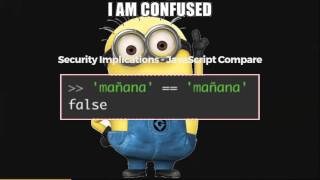
How Does Unicode Affect Our Security?
In-depth exploration of how encoding schemes can lead to IT implementation flaws and security vulnerabilities, with a focus on Unicode's impact on system security.
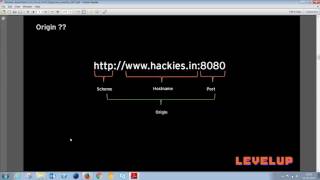
Browser Exploitation for Fun and Profit - Dhiraj Mishra, Bugcrowd's LevelUp 2017
Explore browser vulnerabilities, their root causes, and exploitation techniques. Learn about interesting security flaws discovered during research and gain insights into browser exploitation.
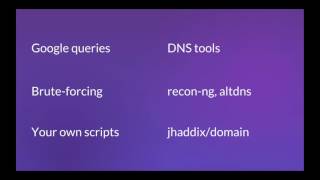
Targeting for Bug Bounty Research - Matthew Conway, Bugcrowd's LevelUp
Discover advanced techniques for identifying and assessing potential targets in bug bounty programs, going beyond conventional methods to maximize research efficiency and effectiveness.
Advanced Android Bug Bounty Skills - Ben Actis, Bugcrowd's LevelUp 2017
Explore advanced Android bug bounty techniques, focusing on IPC vulnerabilities, mobile-specific issues, and leveraging web hacking skills for mobile security testing.
Do You Like Fuzzing? - Abhijeth, Bugcrowd's LevelUp
Explore REST API fuzzing with Fuzzapi, an automated tool for detecting vulnerabilities in web/mobile applications and improving API security.