Learn Offensive JavaScript Today
Discover offensive JavaScript techniques including keylogging, data exfiltration, password theft, and CSRF bypass in this concise tutorial on exploiting web vulnerabilities.
Tales of Obfuscation in Bounded Arithmetic, Metacomplexity, and Differential Privacy
Explores obfuscation's role in theoretical computer science, covering Circuit Range Avoidance, metacomplexity of Kolmogorov complexity, and computational differential privacy, with focus on recent results and open questions.
Tutorial on Obfuscation
Explore minimal complexity assumptions for cryptography, focusing on obfuscation techniques and their applications in secure system design.
Hacking for Fun and Profit - Motivations and Rewards
Explore the motivations behind hacking and its potential for both enjoyment and financial gain with HackerOne CEO Mårten Mickos at Disobey 2017.
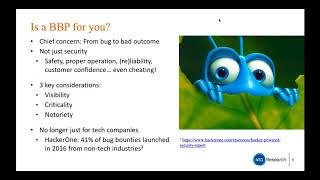
Bug Bounties and the Path to Secure Software Development
Explore bug bounties and vulnerability disclosure policies for secure software development, including implementation strategies, benefits, and best practices.
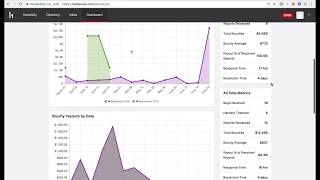
HackerOne Product Walkthrough - Security Team and Researcher Perspectives
Explore HackerOne's platform from both security team and researcher perspectives, covering report management, rewards, and key features for effective vulnerability disclosure.
Bug Bounty Product Demo - HackerOne Platform Overview
Explore HackerOne's platform for managing security vulnerabilities, leveraging ethical hackers, and enhancing penetration testing with co-founder Michiel Prins.
How to Win Over Security Teams and Gain Influence as a Hacker
Insights from experienced hackers on effective strategies, tools, and etiquette for successful bug bounty hunting and building positive relationships with security teams.

An Invitation to Hack - Benefits and Risks of Vulnerability Disclosure Programs
Explore vulnerability disclosure programs' benefits and risks, legal considerations, and real-world examples. Learn practical insights for implementing these programs to enhance cybersecurity in organizations.
Hacker-Powered Security in Agile Software Development - Webinar
Explore hacker-powered security in agile software development, covering open source risks, bug bounty benefits, and integrating security into continuous delivery workflows.
Engineering, Hacking, and Security Panel - Insights from Industry Experts
Panel discussion on engineering, hacking, and security careers featuring insights from industry professionals. Covers career paths, learning resources, challenges, and advice for aspiring hackers and engineers.
Bug Bounty Field Manual - Cliff Notes for Planning and Operating Successful Programs
Comprehensive guide on planning, launching, and operating successful bug bounty programs, covering team formation, scope setting, bounty structures, and program management strategies.
Advanced Hacking Workshop - Techniques and Personal Insights
Top hackers share advanced techniques, personal stories, and insights on bug bounty hunting. Learn from experts Frans Rosén and Peter Yaworski about URL validation, third-party scripts, and building a hacking career.
Tips on Building a World-Class Bug Bounty Program - Zenefits Red Team Insights
Learn from Zenefits' Red Team expert on building a top-tier bug bounty program. Gain insights on best practices, collaboration strategies, and maintaining program effectiveness for robust data protection.
Pentest Reporting and Best Practices
Learn step-by-step techniques for crafting high-quality penetration test reports, including effective articulation of technical details and tips for writing for both technical and executive audiences.
Pentesting Resources
Explore top pentesting resources, practice platforms, and valuable certifications to enhance your skills and advance your cybersecurity career.
Hacker101 - Android Quickstart
Learn essential Android app hacking concepts, tools, and techniques in this quick guide. Explore APK structure, emulators, decompilation, and security testing methods for successful mobile app penetration testing.
Maximizing Burp
Enhance vulnerability detection skills using Burp Suite's advanced features like Intruder and Scanner for more effective penetration testing.
The Hacker Army: Protecting Your Data Through Bug Bounty Programs
Explore how ethical hackers form a global freelance security team, supporting internal teams through bug bounty programs and keeping us safer online in the face of cybersecurity challenges.
Tapping Hackers for Continuous Security
Explore how external hackers can enhance security, assess the suitability of bug bounty programs, and learn to build effective vulnerability disclosure programs for improved software development.
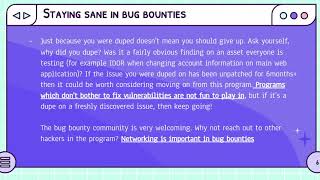
Staying Sane in Bug Bounties - Navigating Challenges and Persistence
Strategies for maintaining mental well-being while participating in bug bounty programs, addressing common challenges and providing guidance on persistence and decision-making.