Embracing the Multi-Party Dilemma: Incident Response Across Company Boundaries
Explore incident response challenges across company boundaries, focusing on managing vendor relationships and learning from multi-party incidents in software systems.
Identity-based Source Integrity with Gitsign
Explore Gitsign, a Sigstore project for keyless, identity-based Git commit signing. Learn its benefits over traditional methods and how it enhances security in CI/CD and GitOps workflows.
Preparing for Effective OT Incident Response - Key Actions and Recommendations
Explore OT incident response preparedness with expert recommendations on facilities, personnel, procedures, and communication tools. Gain actionable insights to enhance your organization's readiness.
Incident Response for ICS: Differences Between OT and IT Environments
Explore key differences between OT and IT incident response, focusing on global incident command and the critical importance of ICS-specific response plans for OT cybersecurity preparedness.
Stories from the Life of an Incident Responder
Explore real-world IT security incidents, attack methods, and prevention strategies. Learn essential steps for incident response and how to prepare your organization for potential cyber threats.
Critical Evaluation and Historical Context of the Vulkan Leaks - Lecture 10
Analyze the Vulkan Leaks' impact on cybersecurity, exploring historical context and critical implications for threat intelligence and network defense strategies.
Inside the Biggest Hacks and Facts of the Past Year - 2022-2023
Explore the most significant cybersecurity events, active threat actors, and surprising facts from 2022-2023 in this comprehensive overview of the rapidly evolving digital security landscape.

Security Onion Essentials 2.4 - Threat Hunting
Explore threat hunting techniques in Security Onion 2.4, covering workflow essentials and practical strategies for proactive cybersecurity defense and network monitoring.
SANAN: Development of Lightweight Live Acquisition Tool for Amphibious Incident Response - Paper 7
Explore SANAN, a lightweight live acquisition tool for digital forensics, designed to efficiently capture volatile data during incident response in our increasingly digital world.

Browser Forensics - Are We Missing Something?
Explore browser forensics techniques to uncover user activities through artifacts like favicons and login data, enhancing investigation and incident response capabilities.
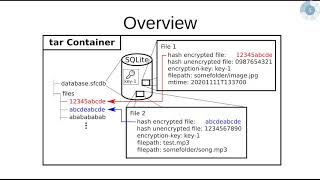
Lightning Talks 2020 - Open Source Digital Forensics Conference
Engaging series of rapid-fire presentations on cutting-edge topics in open source digital forensics and incident response.
Are You Safe from OWASP #11? - Creating a Successful API Security Program
Explore API security beyond Top 10 lists, focusing on building a comprehensive program at scale. Learn key strategies for successful API protection and management.
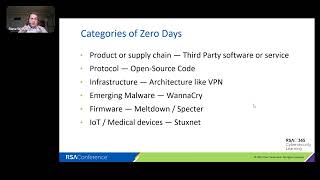
Don't Let Zero Days Steal Your Weekends
Learn strategies to effectively handle zero-day threats, including mitigation techniques and real-world use cases, to prevent these emergencies from disrupting your team's work-life balance.
RSAC 365 Virtual Seminar - Supply Chain Security
Explore open-source supply chain threats, defense frameworks, and incident response strategies. Learn to track attackers, protect your organization, and shift thinking on supply chain security from experts in the field.
Cyber Threat Intelligence Demystified - Leveraging Intelligence for Effective Cybersecurity
Explore cyber threat intelligence essentials, best practices, and automation tools to enhance your organization's cybersecurity strategy and proactively combat advanced threats.

Flare-On FireEye 2018 CTF - Malware Analysis of Flare Minesweeper
Expert malware researcher Amr Thabet discusses the Flare-On FireEye 2018 CTF challenge, providing insights into malware analysis techniques and sharing experiences from high-profile cybersecurity investigations.
Red Team Adversary Emulation With Caldera
Explore automated Red Team adversary emulation using MITRE Caldera, a framework built on ATT&CK for simulating attacks and testing organizational security defenses.
Drivers for Software Supply Chain Security Programs
Explore software supply chain security concerns, drivers, and strategies based on a survey of 300 tech executives. Gain insights into current issues and learn programmatic approaches to address risks.
Defense-in-Depth Engineering Techniques for Secure Software Design
Explore techniques for building resilient software, identifying overlooked vulnerabilities, and designing for incident preparedness. Learn to architect secure systems and improve incident response capabilities.
Unified SOC - Centralized Security Data with OT Visibility for Intelligence-Driven Investigations
Experts discuss unifying Security Operations Centers by integrating OT cybersecurity, threat intelligence, and advanced technologies for comprehensive visibility and efficient investigations in industrial environments.
Performing Rapid Triage Analysis using ANY.RUN
Explore rapid triage analysis using ANY.RUN for efficient malware assessment. Learn to gather crucial indicators of compromise and prioritize potential threats effectively.