Is the Internet on Fire? Strategies for Mitigating Open Source Software Vulnerabilities
Explore strategies for mitigating open source software vulnerabilities, including supply chain attacks, SBOMs, and next-generation security controls for robust defense and compromise resilience.
Securing Our Cyberspace Together
Explore cybersecurity strategies with Singapore's Commissioner of Cybersecurity. Gain insights on national cyber defense, policy development, and international collaboration for a secure digital future.
The Fault in Our Metrics - Rethinking How We Measure Detection and Response
Rethinking cybersecurity metrics: Learn to develop meaningful measurements for detection and response capabilities, avoiding pitfalls of traditional metrics and motivating teams effectively.
Traceability in Cybersecurity - Lessons Learned from the Medical Sector
Explore traceability in cybersecurity through insights from the medical sector, enhancing security practices and incident response strategies.

Complete CyberSecurity Roadmap 2024 - Beginner's Guide to Ethical Hacking
Comprehensive guide to becoming an ethical hacker, covering essential steps, skills, and resources for beginners entering the cybersecurity field in 2024.
The Forensic Frontier - Exploring Digital Forensics and Cybersecurity
Explore digital forensics' critical role in cybersecurity through an army veteran's journey. Gain insights into challenges, innovations, and the importance of indigenous solutions in this evolving field.
War Stories - Fighting Ransomware Operators
Insights into combating ransomware from a cybersecurity expert, sharing real-world experiences and strategies for incident response and threat mitigation.
A New Architecture for Data Security to Free Incident Responders from False Positives
Explore a new data security architecture that minimizes false positives, enhancing incident response efficiency and improving detection of real security threats.
Llama: The Fast-File Processor with No Drama
Explore fast-file processing techniques for efficient digital forensics and incident response, enhancing investigative capabilities without complications.
How Persistent is an APT? Battling Three Threat Actors in a Single Environment
Explore real-world strategies for combating multiple persistent threat actors simultaneously, uncovering their evasion tactics and adapting incident response techniques in complex cybersecurity scenarios.
Forensic Analysis of Compromised VPN Appliances by Advanced Actors
Arm yourself with techniques to analyze VPN-related intrusions, understand threat actor tactics, and identify IOCs. Gain actionable insights for improved incident response and VPN defense.
Extracting Forensic Artifacts from Seemingly Idle iOS Devices - Dormant Devices, Chatty Logs
Uncover hidden forensic artifacts from idle iOS devices using system logs, revealing crucial data for investigations beyond traditional imaging methods.
The SaaS-y Side of Incident Response - Key Log Sources for Okta, GitHub, and Salesforce
Explore key log sources for Okta, GitHub, and Salesforce in cloud-based incident response. Learn to interpret SaaS logs, avoid common pitfalls, and improve detection strategies for effective security management.
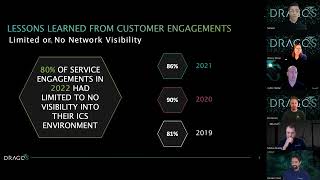
2022 ICS/OT Cybersecurity Year in Review - Lessons Learned from the Frontlines
Incident responders discuss industrial cybersecurity trends, mitigation strategies, and regulatory impacts, offering insights to protect ICS/OT environments based on real-world experiences.
Open Software Supply Chain Attack Reference (OSC&R) - OWASP Foundation
Explore the OSC&R framework for software supply chain security, analyzing real-world attacks and improving DevSecOps programs to enhance overall security posture.
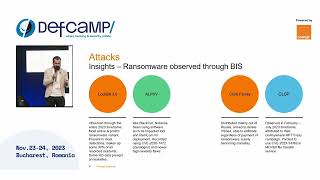
Rough Seas and Ships in Storms - A 2023 Retrospective from an MSSP Perspective
Cybersecurity expert reviews 2023 challenges for Managed Security Service Providers, offering insights on navigating threats and protecting organizations in an evolving digital landscape.
Using RPA for Fast, Reliable and Repeatable Incident Response
Explore how Robotic Process Automation enhances incident response in cybersecurity, offering speed, reliability, and repeatability for improved threat management and operational efficiency.
The State of Cybersecurity - 2023 Year in Review
Insights on 2023's cybersecurity landscape, including attacker techniques, defense strategies, and impact on executive decisions, from Mandiant's incident response experiences.
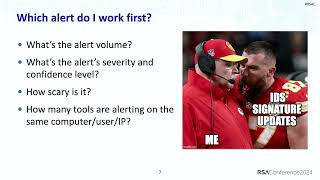
Everything Everywhere All at Once - A Guide to Alert Triage and Analysis
Learn effective alert triage and analysis techniques for incident response, including basic triage methods and an information collection checklist to make informed decisions during overwhelming situations.
Backdoors and Breaches - Live Tabletop Exercise Demo
Interactive tabletop exercise demonstrating incident response strategies and cybersecurity best practices through simulated breach scenarios and team-based problem-solving.
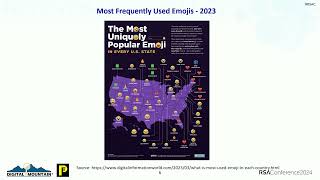
The Evolving Role of Emojis in Investigations and Data Security
Explore the impact of emojis in digital investigations, including tools for decoding meanings, enhancing security, and detecting potential criminal activity. Learn about ChatGPT's role in emoji analysis.