SHADOWPAD - Chinese Espionage Malware-as-a-Service
Comprehensive analysis of SHADOWPAD malware: its origin, usage patterns, and business model. Explores its impact on Chinese cyber espionage and the evolving threat landscape.
Turning an Incident Report into a Design Issue with TLA+
Explore how modeling-driven techniques and TLA+ can enhance postmortem analysis, uncover root causes, and improve system design in distributed database architectures.
Logs Told Us It Was DNS, It Looked like DNS, It Had to Be DNS, It Wasn't DNS
Unraveling a complex Kubernetes incident: from DNS suspicions to kernel-level insights, culminating in a surprising three-line code fix. Learn debugging techniques and unexpected system behaviors.
An Organizational Response to Incidents - Designing for Smooth Coordination
Strategies for effective incident response coordination, focusing on follower roles and organizational preconditions. Insights to improve communication and collaboration during software outages.
Incident Commanders to Incident Analysts - How We Got Here
Explore the transition from incident management to incident analysis, highlighting the distinct skills required and the value of post-incident learning for driving meaningful organizational change.
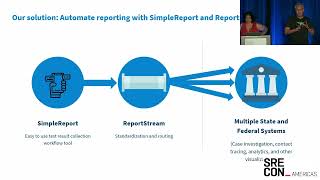
SRE's Critical Role in the COVID-19 Pandemic Response in Government
Explore how SREs in government navigated regulatory constraints to rapidly deploy critical software services during the COVID-19 pandemic, showcasing their adaptability and incident response skills.
Far from the Shallows - The Value of Deeper Incident Analysis
Explore the value of in-depth incident analysis in SRE, moving beyond surface-level metrics to uncover hidden insights and improve system reliability through qualitative investigation.
Human Observability of Incident Response
Practical advice on improving incident response outcomes by understanding the human element. Explores coordination, learning, and socio-technical systems in incident management.
Empathy and Vulnerability in SecOps
Explore how empathy and vulnerability enhance SecOps, improving team collaboration, incident response, and security awareness programs for more effective and resilient operations.
How Automating Incident Response Secures Your Security Posture
Explore how automating incident response enhances security posture, builds team capacity, and cultivates new skills in this insightful discussion with Karl Klaessig of ServiceNow.
Incident Response at Scale - Building a Next Generation SOC
Explore strategies for automating incident response processes in large-scale environments to improve efficiency, visibility, and organizational protection.
It's 10pm, Do You Know Where Your Access Keys Are?
Strengthen AWS infrastructure against attacks: Learn to secure environments, monitor for threats, and recover from incidents using AWS tools like Config, CloudWatch, and IAM.
LangSec for the Masses
Explore AWS security best practices, including hardening, monitoring, and recovery techniques. Learn to protect your infrastructure against common attacks and respond to security breaches effectively.
Old Dog, New Tricks - Forensics With PowerShell
Explore PowerForensics: a PowerShell-based toolset for live digital forensics and incident response, enabling efficient investigation of advanced cyber threats without system imaging.
The CISO's Dilemma
Explore the challenges faced by Chief Information Security Officers and strategies for effective cybersecurity leadership in today's complex threat landscape.
They are the Champions - How To Build and Maintain an Effective Cybersecurity Champion Programme within your Organisation
Maximizing security awareness through a champions program: scaling up, improving communication, enhancing security cost-effectively, and boosting incident reporting. Aligning with company culture for effective implementation.
OSTrICa - Open Source Threat Intelligence Collector
Explore OSTrICa, an open-source framework for automated threat intelligence collection and visualization. Learn about its plugin-oriented architecture and applications in cybersecurity and incident response.
Lessons Learned from the CISA COVID Task Force & Healthcare Attacks
Insights from CISA's COVID Task Force and healthcare cybersecurity efforts, exploring challenges, strategies, and lessons learned in protecting critical infrastructure during the pandemic.
Low Context DevOps - Improving SRE Team Culture through Defaults, Documentation, and Discipline
Strategies for creating a low-context SRE culture: leveraging defaults, simplifying processes, and fostering documentation habits to enhance teamwork, onboarding, and incident response in DevOps environments.
SOC Panel Keynote
Explore insights from security operations center experts in this panel discussion, covering best practices, challenges, and emerging trends in cybersecurity management.
Incident Response Evolved - A Preventative Approach to Incident Management
Explore preventative incident management strategies, evolving threat landscapes, and real-world case studies to enhance your organization's cybersecurity preparedness and response capabilities.