Operation Escalation - How Commodity Programs Are Evolving Into Advanced Threats
Explore how common programs transform into sophisticated threats, examining indicators, processes, and impacts across various sectors and geographic regions.
Preach It Don't Breach It - Cyber Security and Data Protection as Partner in Crime
Explore the synergy between cybersecurity and data protection in incident response. Learn to build robust security programs that safeguard personal data and comply with privacy laws.
Building a Healthy On-Call Culture
Strategies for building a healthy on-call culture, focusing on transparency, shared responsibility, preparedness, system resilience, actionable alerts, and continuous learning to improve incident response and team well-being.
OMGOVHBBQ
Análisis detallado del incendio en el centro de datos de Estrasburgo en marzo de 2021, sus causas y consecuencias para la infraestructura en la nube.
The Log4J Rollercoaster - From an Incident Response Perspective
Insights from the frontlines of Log4J incident response: preparing for unknown vulnerabilities, leveraging threat intelligence, and aiding the community during a major cybersecurity crisis.
Patterns, Not Categories - Learning Across Incidents
Explore a pattern-centered approach to outage analysis, moving beyond traditional categorization methods to identify fundamental failure patterns in complex systems for improved reliability decision-making.

Security Onion Essentials - Alert Triage and Case Creation
Learn essential alert triage and case creation techniques for Security Onion, enhancing your ability to efficiently manage and respond to security incidents in this comprehensive workflow guide.

State of the Onion - Security Onion Conference 2021
Comprehensive overview of Security Onion's latest developments, features, and future roadmap, presented by Doug Burks at the annual conference.

SOARing with Security Onion
Explore how Security Onion integrates with automation tools for enhanced incident response, enabling faster threat detection and improved security operations efficiency.

Security Onion Automation and Response Lab with n8n and Velociraptor
Explore automated incident response with Security Onion, n8n, and Velociraptor. Learn to set up a zero-cost detection and response orchestration system for enhanced cybersecurity workflows.

Security Onion Essentials - Alert Triage and Case Creation
Learn essential alert triage and case creation workflows in Security Onion, covering key aspects of security incident response and management for network defenders.

Blue, Red, Purple, White - Which Team Are You On?
Explore cybersecurity team roles, network layouts, and threat detection scenarios using Security Onion. Learn about FOSS tools, packet analysis, and data source integration for effective security operations.

Security Onion 2017 - Pivoting Effectively to Catch More Bad Guys
Learn effective pivoting techniques to enhance threat detection and investigation skills, improving your ability to identify and catch malicious actors in cybersecurity.

The Investigators Labyrinth - A Data-Driven Perspective
Explore data-driven perspectives on digital forensics and incident response, focusing on cognitive challenges, investigation processes, and analytical strategies for security professionals.
An Incident Post-Mortem
Explore the process of conducting effective incident post-mortems in software engineering, focusing on collaborative problem-solving and continuous improvement without blame or finger-pointing.
The Proactive Approach - Data Driven Observability & Incident Response
Explore data-driven observability and incident response in DevOps, focusing on proactive approaches, streamlined processes, and effective emergency management techniques.
DFIR - Don't Forget Your Roots
Explore essential DFIR skills, from understanding applications and APIs to analyzing C2 beacons, with insights from an experienced practitioner's career journey.
The Challenges of Remediation During a Cyber Incident
Explore strategic, technical, and industry-wide challenges in cybersecurity incident remediation, featuring a real-world case study and expert insights.
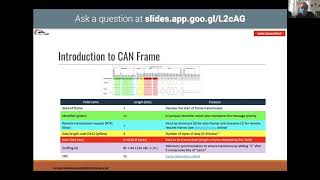
Car Hacking Virtual Lab
Explore vehicle architecture, CANbus protocol, CAN frames, and car hacking tools in this hands-on virtual lab. Learn from experts in automotive security and gain practical skills in vehicle system penetration testing.
Out of Denial - A 12-Step Program for Recovering Admins
Discover a 12-step program for IT admins to enhance security practices, from leveraging existing tools to implementing advanced strategies and staying current with industry trends.
Social Media in Incident Response Program
Explore integrating social media into incident response programs for enhanced situational awareness, flexible communication, and real-time information gathering during crises.