Real Security Incidents - Unusual Situations
Explore real-world security incidents and unusual situations with Adam Dean, gaining insights into practical cybersecurity challenges and their solutions.
Tales From The Trenches - Practical Information Security Lessons
Practical information security insights from real-world scenarios, covering mouse movements, traveler vulnerabilities, and Wi-Fi risks, with actionable lessons for enhancing cybersecurity practices.
How I Learned to Stop Worrying and Build a Modern Detection & Response Program
Discover a framework for building effective, modern detection and response programs. Learn key capabilities and strategies to enhance your cybersecurity approach.
Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.
Unveiling the Open Source Visualization Engine for Busy Hackers
Open source engine for creating advanced data visualizations, enabling visual learners to interpret complex data sets efficiently. Useful for security practitioners, incident responders, and malware researchers.
Legal Aspects of Cyberspace Operations
Explore legal frameworks for cyberspace operations, including network security, defense, exploitation, and attack. Gain insights into recent incidents and their legal classifications.
Targeted Intrusion Remediation - Lessons From The Front Lines
Explore strategies for combating persistent cyber threats, focusing on inhibiting attacker activities, enhancing detection capabilities, and improving rapid response techniques for effective intrusion remediation.

The State of Incident Response
Explore economic and psychological factors shaping incident response in cybersecurity, examining trends, challenges, and potential solutions for protecting networks against sophisticated attacks.
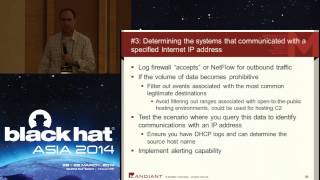
Beyond ‘Check The Box’ - Powering Intrusion Investigations
Explore advanced intrusion investigation techniques, focusing on DHCP logging, Kerberos tickets, and DNS resolutions to enhance cybersecurity capabilities and identify compromise indicators.
Z - MAKE TROY NOT WAR - Case Study of the Wiper APT in Korea, and Beyond
Análisis detallado del ataque "Wiper" en Corea del Sur en 2013, explorando el vector de infección inicial, examinando muestras de malware y estableciendo conexiones con otros casos de APT desde 2009.
Is That a Government in Your Network or Are You Just Happy to See Me?
Explore techniques for identifying and defending against long-term network intrusions by foreign intelligence agencies, with insights on open-source tools for detecting impersonation attacks.
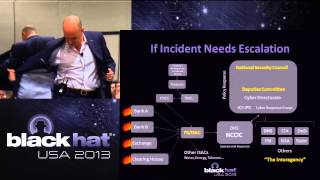
Above My Pay Grade - Cyber Response at the National Level
Explore national-level cyber incident response, from individual banks to presidential decisions, examining the flow of information and decision-making in major cybersecurity crises.
Computer Forensics - A Critical Process in Your Incident Response Plan
Explore computer forensics as a crucial component of incident response planning, enhancing cybersecurity preparedness and investigative capabilities.
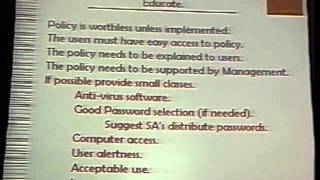
Incident Response in a Microsoft World
Explore incident response strategies for Microsoft environments, focusing on effective techniques to detect, analyze, and mitigate security breaches in Windows systems.
Putting 2 and 2 Together
Explore advanced cybersecurity techniques and threat analysis strategies in this Black Hat conference talk, focusing on connecting disparate pieces of information to uncover hidden vulnerabilities and potential attacks.
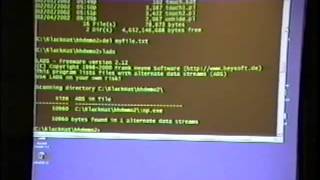
NT - 2K Incident Response & Mining for Hidden Data - PostMortem of Windows Box
Explore advanced techniques for Windows incident response and data mining, uncovering hidden information in NT/2K systems for effective forensic analysis.
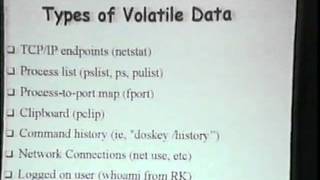
NT - 2K Incident Response & Mining Hidden Data - PostMortem of Windows Box pt2
Explore advanced techniques for Windows incident response and data mining, focusing on hidden information extraction and post-mortem analysis of compromised systems.
Using Security Onion to See Adversary Activity through All Phases of the Kill Chain
Explore how Security Onion detects and analyzes adversary activities across all stages of the cyber kill chain, enhancing threat detection and response capabilities.

Augmenting the Onion - Facilitating Enhanced Detection and Response with Open Source Tools
Explore open-source tools for enhancing threat detection and response capabilities in Security Onion, improving network security monitoring and incident handling processes.
Troubleshooting Tiered Tragedy - A Peek Into Failure
Explore real-world system failure scenarios, learn effective troubleshooting techniques, and discover strategies to prevent and mitigate catastrophic incidents in complex software environments.
Incident Analysis Before Chaos Engineering
Explore incident analysis in chaos engineering with real-world stories, learn its benefits, and discover how to implement it effectively for improved system resilience and reliability.