Security Orchestration and Incident Response
Explore cyber-resilience strategies in an uncertain world, integrating human expertise with machine learning for effective security orchestration and incident response.
Codifying the Brain - Automation, Alerts and a Human Resource Answer
Explore automation strategies to address the cybersecurity talent shortage, featuring case studies and best practices for efficient incident response and threat mitigation.
SCADA Attack Detection
Explore ICS/SCADA attack detection techniques, relevant logs, and ML-based anomaly detection methods. Includes practical demonstrations and insights for enhancing industrial cybersecurity.
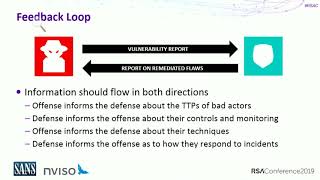
Live Adversary Simulation - Red and Blue Team Tactics
Explore live adversary simulation techniques, enhancing communication between red and blue teams for effective cybersecurity. Learn to perform threat simulations, map APT phases, and implement purple teaming strategies.
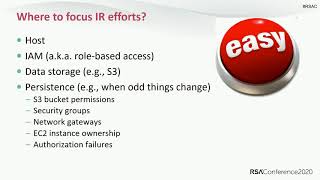
Clearing the Clouds - Incident Response in AWS - Isn’t as Bad as You Thought
Demystifying AWS incident response through detailed use cases, focusing on architecture, shared responsibility, and practical strategies for handling AWS-specific security incidents.
Peel Back the Layers of Your Enterprise and Make Your Adversaries Cry
Explore enterprise security with Security Onion, an open-source platform offering comprehensive visibility. Learn about intrusion detection, network monitoring, and incident response techniques to detect and interrupt adversaries quickly.
How Threat Intelligence Sharing and Automation Wins the War against Attackers
Explore how real-time threat intelligence sharing, automation, and orchestration can enhance cybersecurity efforts and effectively combat attackers in today's digital landscape.
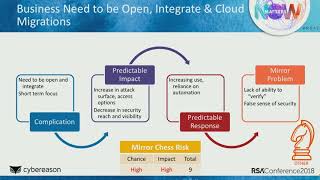
Mirror Chess - Why Mature, Predictable Security Is a Disaster
Explore how predictable security measures can be exploited by adversaries and learn strategies to enhance cybersecurity through innovative, unpredictable approaches.
Stories from the Front Line - Forensic Investigation and Incident Response
Explore real-world cyber incidents, attack methodologies, and forensic investigation techniques used in high-profile cases like Polish bank attacks and Bangladesh Bank heist.
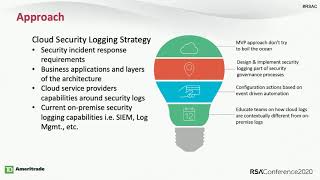
The Fog of Cloud Security Logging
Explore TD Ameritrade's multi-cloud security logging approach, focusing on critical events, use cases, and implementation strategies for AWS and Azure to enhance incident response and threat management.
The Surge of BEC Attacks and How to Mitigate Damages
Explore BEC attacks, their impact, and effective mitigation strategies through real-world case studies. Learn response procedures and recommendations to protect your organization from these prevalent cyber threats.
Detection & Response - Building Effective SOC Operations
Insider's guide to planning and building effective SOC operations, covering technical, process, and personnel considerations for enhanced cybersecurity capabilities.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.
Call of Duty Crypto Ransomware
Explore crypto ransomware's history, infection methods, behavior, and defense strategies. Learn prevention, detection, and incident response techniques for this evolving threat.
Robots Ninjas Pirates and Building an Effective Vulnerability Management Program
Explore effective vulnerability management through a unique lens of robots, ninjas, and pirates. Learn prevention, detection, and reaction strategies to enhance cybersecurity.
What Do Infosec Practitioners Actually Do
Explore the daily realities of information security professionals, debunking myths and highlighting key skills like writing, problem-solving, and effective communication in various cybersecurity roles.
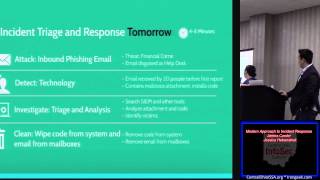
Modern Approach to Incident Response
Explore modern incident response strategies, including automation, threat intelligence, and AI, to enhance cybersecurity practices and reduce response times for various threats.
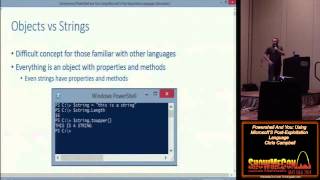
Powershell and You - Using Microsoft's Post Exploitation Language
Explore PowerShell's potential for cybersecurity, from basic cmdlets to advanced scripting techniques. Gain insights into its use in hacking, post-exploitation, and incident response.
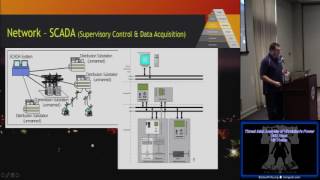
Threat Intel Analysis of Ukrainians Power Grid Hack
Analyze the Ukrainian power grid hack, exploring tools, techniques, and implications. Learn about ICS vulnerabilities, attack stages, and strategies to enhance critical infrastructure security.
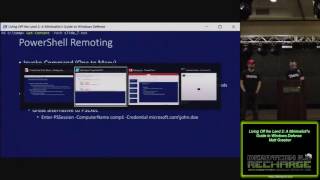
Living Off the Land 2 - A Minimalist's Guide to Windows Defense
Explore minimalist Windows defense techniques, including PowerShell remoting, WMI data collection, ETW for incident response, and Device Guard monitoring and bypass strategies.
Practical Applications of the Dickerson Pyramid
Exploring real-world implementations of the Dickerson Pyramid for Site Reliability Engineering, with examples from Google, Hillary for America, and First Look Media.