Prevention as a Business Strategy
Explore how prevention-focused cybersecurity strategies using AI and machine learning can protect businesses from evolving threats, reducing risks and costs associated with traditional detect-and-respond approaches.
Breaches Are Everywhere - What’s A Good Security Leader To Do?
Explore strategies for security leaders to combat increasing breaches, from IoT vulnerabilities to phishing attacks. Learn essential skills and best practices for effective cybersecurity management.
Topics of Interest - An Attacker's View on APAC's 2021 Three Major Breaches
Explore an attacker's perspective on APAC's major 2021 breaches, analyzing causes and prevention strategies for enhanced cybersecurity awareness.
Stories from DART - Taking the Ware out of Ransomware
Microsoft's DART team shares insights on minimizing ransomware exposure through real-world case studies, offering practical strategies for investigation, mitigation, and remediation across organizations.
Ready for - Nearly Anything - Preparing Your Organisation for a Cyber Incident
Practical guide to preparing organizations for cyber incidents, covering key processes, skilled personnel, logging, containment technology, and coordination tools for effective response.
Bypassing Malware Analysis Sandboxes Is Easy - Let’s Discuss How They Are Doing It and Why It Works
Explore techniques used by malware to evade analysis sandboxes, comparing various sandbox solutions and their effectiveness in detecting and analyzing different types of malware.
A Year in the Wild - Fighting Malware at the Corporate Level
Explore Yelp's automated malware defense system, featuring in-house tools like AIR and OSXCollector, complemented by open-source solutions for swift threat detection and response in corporate networks.
Fantastic Red-Team Attacks and How to Find Them
Explore prevalent gaps in organizational defenses through Atomic Red Team testing. Learn to identify and analyze complex attack patterns using Event Query Language and data analysis techniques.
Incident Response
Explore incident response and threat intelligence with Palo Alto Networks' SVP Wendi Whitmore, discussing cybersecurity consulting, ransomware trends, and prevention strategies.
My Bro The ELK - Obtaining Context From Security Events
Automate security event analysis using ELK, Bro IDS, and threat intelligence feeds. Learn to integrate frameworks for faster incident response and enhanced threat detection.
Security Research on Mercedes-Benz - From Hardware to Car Control
Explore Mercedes-Benz car security research, from hardware analysis to gaining control. Learn about attack surfaces, reverse engineering, and cloud control in modern connected vehicles.
Ransomware - Creation, Detection, and Response
Explore ransomware creation, detection, and response strategies. Learn evasion techniques, novel detection methods, and tailored incident response approaches from real-world engagements.
Critical Infrastructure Network Attacks - Code Red, Alert Network Operators
Analyze new tactics used by cybercriminals targeting critical infrastructure with multistage ransomware attacks, focusing on electric transmission substation vulnerabilities and incident timelines.
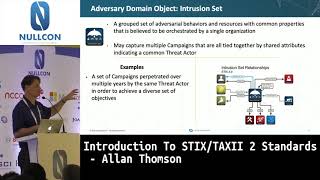
Introduction to STIX - TAXII 2 Standards
Comprehensive overview of STIX/TAXII 2 standards for Cyber Threat Intelligence, covering key concepts, data models, and interoperability challenges in threat intelligence sharing.
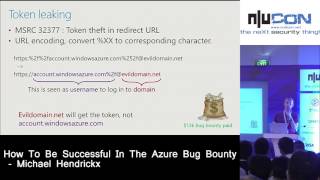
How to Be Successful in Azure Bug Bounty
Learn Azure bug bounty strategies from a Microsoft expert, covering attack surfaces, past payouts, and how to start hunting for vulnerabilities in cloud infrastructure.
Rapid Incident Response with PowerShell
Learn essential PowerShell techniques for rapid incident response, focusing on preparation, identification, and containment strategies to effectively handle cyber attacks like NotPetya.
Embrace the Red - Enhancing Detection Capabilities with Adversary Simulation
Enhance detection capabilities through adversary simulation techniques. Learn to leverage offensive skills, conduct purple teaming, and test resilience using tools like Password Frame and Empire Spray.
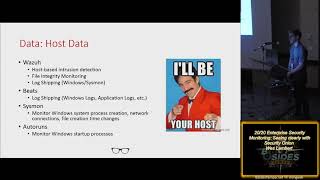
Enterprise Security Monitoring - Seeing Clearly with Security Onion - Wes Lambert
Learn to implement enterprise-level security monitoring using Security Onion, covering tools, data types, interfaces, and deployment strategies for effective threat detection and analysis.
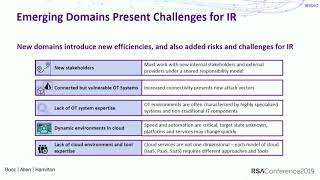
Incident Response Beyond Enterprise IT
Explore strategies for effective incident response in emerging domains like cloud, OT, and mobile. Learn about new service models, team structures, and proactive solutions for evolving cybersecurity challenges.
How I Learned Docker Security the Hard Way - So You Don’t Have To
Practical insights on securing Docker containers, from architecture to incident response. Learn threat modeling, attacker techniques, and best practices for DevOps security.
Ransom - A Real-World Case Study in Data Theft, Forensics and the Law
Explore a real-world data theft case, covering forensics, legal aspects, and emerging cyber threats. Gain insights into adversary tactics and effective response strategies.