Birthday Hunting
Explore the Birthday Paradox in cybersecurity, learning its applications in incident response, investigations, and threat detection. Gain insights into mathematical concepts and practical implementations.
Enterprise Overflow - How Breached Credentials Impact Us All
Explore the impact of breached credentials on enterprises, learn about data leaks, and discover solutions for incident response and active directory management.
Grapl - A Graph Platform for Detection and Response
Explore a graph-based platform for enhanced cybersecurity detection and response, covering node relationships, log analysis, and advanced investigation techniques.
CloudSec Rules Everything Around Me - C.R.E.A.M.
Explore cloud security essentials, from shared responsibility to logging, compliance, and incident response. Learn best practices for AWS, Azure, and Office 365 environments.
What Do Hackers See When They Look at the Clouds
Explore cloud security vulnerabilities, historical incidents, and protective measures. Learn to identify abandoned subdomains and bypass firewalls in this eye-opening talk on hacker perspectives.
Digital Safety for Politically Vulnerable Organizations
Learn strategies for protecting politically vulnerable organizations from digital threats, covering physical and psychological security, incident response, and data retention policies.
To Log, or Not to Log! That Is the Question - DefCamp - 2022
Explore logging challenges in cybersecurity, including sensitive data handling, storage, analysis, and access control. Learn best practices for secure logging in various scenarios.

Gehackt. Und nu?
Professionelle Reaktion auf Hackerangriffe: Phasen, Strategien und Best Practices für effektives Incident Response in Unternehmen.
Building a Cyber Security Operations Center - DefCamp 2015
Explore the challenges, objectives, and key success factors in establishing a Cyber Security Operations Center. Learn about data aggregation, change management, and incident response strategies.
Vulnerability Disclosure, Governments and You
Explore vulnerability disclosure's evolution, its impact on policy-making, and the role of governments. Learn about bug bounties, legal considerations, and international efforts in cybersecurity.
Information Flows and Leaks in Social Media
Explore social media's impact on information flow, opinion formation, and real-world events. Analyze case studies of online campaigns and their consequences across different regions and contexts.
Game Over, Does the CISO Get an Extra Life
Explore CISO challenges, attack surfaces, and security strategies in this talk on navigating the complex landscape of cybersecurity leadership and risk management.
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.
Signatures Are Dead - Long Live Resilient Signatures
Insights on creating resilient, high-fidelity threat detections that withstand evasion attempts, with practical examples from real-world attacks and methodologies for effective detection development.
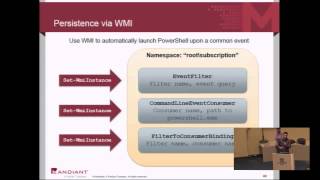
Investigating PowerShell Attacks
Explore PowerShell attack techniques, forensic artifacts, and investigation methods for detecting and mitigating threats in Windows environments.
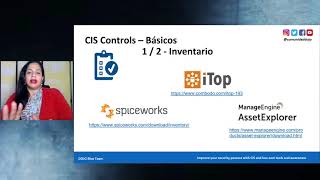
Improve Your Security Posture with CIS Controls and Awareness - Sheila Perez - Ekoparty Security Conference
Guía práctica para mejorar la seguridad utilizando controles CIS y herramientas económicas. Aprende a cerrar brechas de seguridad sin grandes presupuestos.
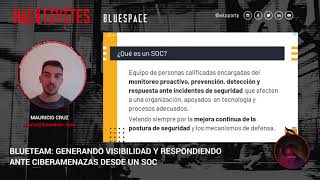
Blue Team - Generando Visibilidad y Respondiendo Ante Ciberamenazas Desde un SOC
Metodología para detectar y responder ante ciberamenazas en organizaciones, abordando visibilidad, priorización y automatización desde un SOC. Incluye servicios, componentes y herramientas para una gestión eficaz.
Defending, Detecting, and Responding to Hardware and Firmware Attacks - Teddy Reed - USENIX Enigma Conference - 2016
Explore firmware security, attack surfaces, and defense strategies. Learn to detect vulnerabilities, monitor integrity, and implement deep systems defense for enterprise protection against hardware and firmware attacks.
Security Testing - Is Automation Failing Us?
Explore the challenges of security testing automation and its impact on identity, privacy, and overall system protection in modern software development.
Breach Assessments - Are You Owned? You Can Find Out!
Discover techniques to detect ongoing network breaches, analyze anomalous behavior, and eradicate threats from Red Team experts turned Blue Team specialists.
Cloud Forensics - Putting The Bits Back Together
Explore cloud forensics challenges and solutions in AWS, focusing on server breaches, disk imaging, and incident response techniques for various EC2 instance types and EBS volumes.