Automating Incident Response - The Serverless Way
Experiencia en automatización de respuesta a incidentes utilizando tecnología serverless. Aprende estrategias para mejorar la eficiencia y efectividad en ciberseguridad.
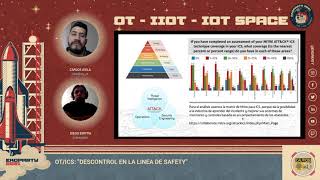
Descontrol en las Líneas de SAFETY - OT - IIOT - IOT Space
Análisis de seguridad en entornos industriales e IoT, enfocado en líneas de seguridad. Expertos comparten experiencias sobre implementación, pruebas y respuesta a incidentes en sistemas OT/ICS.
Securing India - The CERT-In Way
Panel discussion on CERT-IN's notification for reporting security breaches, emphasizing timely incident reporting, organizational awareness, and citizen precautions to enhance India's cybersecurity posture.
A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
Beyond Monitoring
Effektive Überwachung von Systemen: Strategien für Alarmierung, Incident-Management und kontinuierliche Verbesserung in der IT-Infrastruktur.
Logging in the Cloud - From Zero to Incident Response Hero
Learn essential cloud logging practices for AWS, Azure, and GCP to enhance incident response capabilities and streamline security operations in multi-cloud environments.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.
Shall We Play a Game?
Develop effective security exercises using MITRE ATT&CK framework. Learn to create, run, and score drills that turn threat intelligence into practiced action for improved incident response.
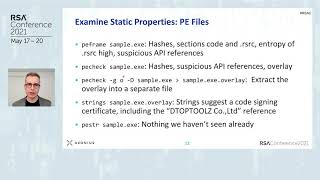
Analyzing Windows Malware on Linux - Getting Started Tips and Examples
Practical session on using free Linux tools for Windows malware analysis, featuring the REMnux toolkit. Learn essential techniques for incident response and SOC analysis.
SolarWinds - What Really Happened?
Insightful analysis of the SolarWinds cyberattack, revealing unique perspectives on the incident's details, methods, and perpetrators, with valuable lessons for enhancing industry-wide cybersecurity measures.
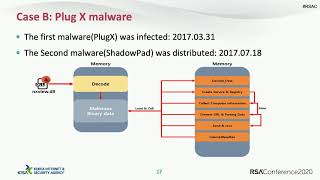
Chronicle of the Supply Chain Attack and Two Attack Strategies
Explore supply chain attack strategies, including software development environment and update server penetration, through analysis of incidents targeting Korean and global companies.
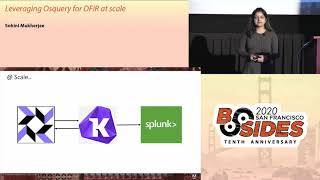
Leveraging Osquery for DFIR at Scale
Explore efficient incident response using Osquery for digital forensics, accelerating breach investigations and uncovering attacker breadcrumbs in large-scale environments.

Threat Hunting Using 16th-Century Math and Sesame Street
Discover innovative threat hunting techniques using mathematical principles and data analysis to uncover unusual machine behaviors in large-scale environments, transcending specific attack patterns.
Understanding the Discipline to Optimize Cyber Defense Collaboration
Explore the Cyber Threat Intelligence Analyst role, its competencies, and how it intersects with other cybersecurity disciplines to enhance collaboration and organizational security posture.
Visibility Beyond Perimeters - Detecting C2 at Time of Execution
Innovative network-based threat detection technique providing real-time alerting without endpoint software. Leverages internet infrastructure to detect malicious activity across organizational boundaries, augmenting existing EDR solutions.
Incident Response in the Cloud - Foggy with a Ray of Sunshine
Explore challenges and solutions for incident response in cloud environments, focusing on logging options, visibility issues, and automated response techniques for improved security operations.

Atomic Threat Coverage - Being Threat Centric
Atomic Threat Coverage framework: Automatically generate actionable analytics to combat threats based on MITRE ATT&CK model, unifying detection, response, mitigation, and simulation for efficient security operations.
Disrupting the Kill Chain
Comprehensive defense strategy for Windows environments, leveraging native Microsoft tools to disrupt cyber-attack kill chains. Covers detection, response, and automated remediation across various attack stages.
Hello to the Dark Side
Explore the intricacies of cybersecurity's dark side with expert L. Grecs, delving into advanced threats, ethical considerations, and cutting-edge defense strategies.
Hacking KPN - Lessons From The Trenches
Explore real-world cybersecurity challenges and solutions through KPN's hacking experience, offering valuable insights for security professionals and enthusiasts.
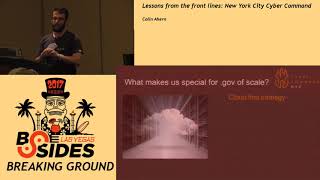
Lessons From the Front Lines - New York City Cyber Command
Insights from NYC Cyber Command's frontline experiences, covering operational design, governance, threat modeling, and future cybersecurity strategies for urban environments.