Discovering Debug Interfaces with the JTAGulator Part 1
Explore debug interfaces and hardware hacking techniques using the JTAGulator, a versatile tool for discovering and exploiting hidden system access points.
Fully Arbitrary 802.3 Packet Injection - Maximizing the Ethernet Attack Surface
Explore novel Ethernet attack techniques using affordable hardware and custom firmware. Learn about frame manipulations, SFD parsing anomalies, and Ethernet Packet-In-Packet injection for enhanced network security testing.
Teridian SoC Exploitation - Harvard Architecture Smart Grid Systems
Exploitation techniques for Teridian 8051-based SoCs in smart grid systems, covering architecture, security barriers, and methods to gain code execution and firmware access.
Power Analysis Attacks for Cheapskates
Discover affordable power analysis attack techniques for cryptographic systems using open-source hardware and software. Learn to set up a budget-friendly lab and perform live demonstrations against AES implementations.
Secure Hardware Design
Explore secure hardware design principles and techniques with experts Kingpin and Brian Oblivion, focusing on protecting electronic systems from vulnerabilities and attacks.
Lost Control - Breaking Hardware-Assisted Kernel Control-Flow Integrity with Page-Oriented Programming
Explore techniques to bypass hardware-assisted kernel control-flow integrity using page-oriented programming, revealing vulnerabilities in modern operating system security mechanisms.
Unlocking Any Door in 21st Century - Immersion in Bio-Security
Explore biometric authentication vulnerabilities, AI/ML risks, and creative hacking techniques. Learn about data privacy threats and strategies to bypass liveness checks in modern security systems.
Downfall - Exploiting Speculative Data Gathering
Unveiling Downfall attacks: new transient execution vulnerabilities exploiting gather instructions on x86 CPUs, compromising security across various computing environments and defeating existing defenses.

Jtagulator - Assisted Discovery of On-Chip Debug Interfaces
Explore on-chip debug interfaces and JTAG architecture with JTAGulator, a hardware tool for identifying and accessing embedded systems' debug ports.
Hardware Tamper Resistance - Why and How
Explore hardware tamper resistance techniques, from physical systems to electronic solutions, and learn about new approaches like machine-verifiable seals and secure multiparty computation.
Crash the IoT Train Yourself - Intentionally Vulnerable WRT IV WRT
Explore IoT device vulnerabilities, including firmware backdoors, default credentials, and web interface flaws. Learn about common security risks and see live demonstrations of exploits.
Identifying and Exploiting Hardware Vulnerabilities - Demo of the HRES Process
Demonstration of the HRES process for identifying and exploiting hardware vulnerabilities, showcasing practical techniques and methodologies.
IoT Defenses - Software, Hardware, Wireless, and Cloud
Explore comprehensive IoT security strategies across software, hardware, wireless, and cloud domains, enhancing your ability to protect interconnected devices and systems.
Run Time Accessible DRAM PUFs in Commodity Devices
Explore DRAM-based Physical Unclonable Functions (PUFs) in everyday devices, their implementation, and potential applications for enhanced security and device authentication.
The First Thorough Side Channel Hardware Trojan
Explore the groundbreaking research on side channel hardware trojans, examining their potential impacts and detection methods in cryptographic systems.
Key Extraction Using Thermal Laser Stimulation - A Case Study on Xilinx Ultrascale FPGAs
Explore thermal laser stimulation for key extraction on Xilinx Ultrascale FPGAs, examining vulnerabilities and potential security implications in hardware cryptography.
Stealthy Opaque Predicates in Hardware - Obfuscating Constant Expressions at Negligible Overhead
Explores hardware-based obfuscation techniques for constant expressions, presenting a novel approach with minimal overhead. Discusses applications in watermarking and security.
On the Difficulty of FSM Based Hardware Obfuscation
Explores challenges in finite state machine-based hardware obfuscation, analyzing vulnerabilities and proposing potential countermeasures for enhanced security in digital circuit design.
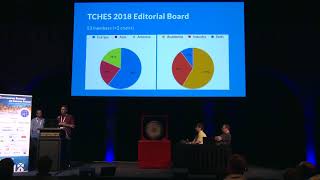
CHES 2018 Rump Session
Cryptographic hardware and embedded systems experts present cutting-edge research and innovations in a rapid-fire format, covering diverse topics in security and cryptography.
The Curse of Class Imbalance and Conflicting Metrics with Machine Learning for Side-channel Evaluation
Explore machine learning challenges in side-channel analysis, focusing on class imbalance and conflicting metrics. Learn strategies to address these issues in cryptographic hardware evaluation.
Deep Learning to Evaluate Secure RSA Implementations
Explore deep learning techniques for evaluating secure RSA implementations, focusing on cryptographic hardware and embedded systems security.