Fuzzers, Analyzers, and Other Gophers Insecticides - Session 1
Explore techniques for discovering vulnerabilities in Go code, including static analysis, fuzzing, and fault injection. Learn about common bugs, concurrency issues, and tools for automated vulnerability detection in Go applications.
Full Speed Fuzzing - Reducing Fuzzing Overhead Through Coverage-Guided Tracing
Innovative approach to reduce fuzzing overhead through coverage-guided tracing, significantly improving efficiency in software bug and vulnerability detection.
Razzer - Finding Kernel Race Bugs through Fuzzing
Discover efficient kernel race bug detection through fuzzing with Razzer. Learn static analysis and deterministic thread interleaving techniques to identify vulnerabilities in Linux kernels.
Fuzzing & Directory Brute-Force With ffuf
Learn to perform fuzzing, enumeration, and directory brute-forcing using ffuf, a fast web fuzzer. Discover techniques for directory discovery, virtual host detection, and parameter fuzzing to enhance your web security testing skills.
Fuzz Testing in Black Box Systems - Merlion Approach
Explore advanced black box fuzzing techniques inspired by Singapore's iconic Merlion, enhancing software security testing skills and uncovering hidden vulnerabilities.
Fuzz Driven Development for JSON Patch Operations - RustConf 2021
Explore fuzzing in Rust for efficient development, using cargo fuzz to build a JSON Patch operation squasher. Learn about misconceptions and leverage community tools for improved testing and code coverage.
Fuzzing the CNCF Landscape - Challenges and Results
Explore fuzzing techniques applied to CNCF projects, including Kubernetes and Etcd. Learn about challenges, results, and continuous integration with OSS-Fuzz for enhanced security.
Securing Fluent Bit by Way of Fuzzing
Explore automated security testing for Fluent Bit using fuzzing techniques. Learn about implementation, bug detection, and the impact on overall security posture.
How the Argo Project Transitioned From Security Aware to Security First
Discover how the Argo project enhanced its security strategy, implementing best practices, formalizing processes, and leveraging community resources to transition from security-aware to security-first.
Fuzzing - Finding Bugs and Vulnerabilities Automatically
Explore automated bug and vulnerability detection through fuzzing. Learn techniques, case studies, and key open-source projects for effective software testing and security enhancement.
Fuzzing Linux with Xen - Advanced Techniques and Findings
Explore advanced Linux fuzzing techniques using Xen, including VM forking, VMI, and full-VM taint analysis. Learn about USB3 xHCI architecture and discover real-world bug findings.
SyzScope: Revealing High-Risk Security Impacts of Fuzzer-Exposed Bugs
Explore SyzScope, a tool revealing high-risk security impacts of fuzzer-exposed bugs. Learn about its workflow, fuzzing techniques, and symbolic execution for effective vulnerability assessment.
Fuzzing Linux Drivers with Syzkaller
Explore Syzkaller for effective Linux driver fuzzing, covering architecture, setup, configuration, and practical use cases to enhance software testing and security.
ACRN Security: Fuzzing and Hardening Edge Hypervisors
Explore fuzzing techniques and security hardening for ACRN, an open-source hypervisor designed for edge computing and IoT devices, with insights on tools and methodologies.
Broken Brokers in Boxes - Fuzzing Breaks Everything, Even Erlang
Explore fuzzing techniques to uncover vulnerabilities in software systems, with a focus on Erlang applications and message brokers.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
Introduction to OWASP's Zed Attack Proxy - Web Application Penetration Testing
Explore OWASP's free, open-source penetration testing tool for web applications. Learn its features, installation, and usage through hands-on demonstrations and testing of insecure web apps.
Fuzzing the Linux Kernel - Mentorship Session
Explore advanced techniques for identifying vulnerabilities in the Linux kernel through fuzzing, enhancing system security and stability.
How to Make Syzbot Reports Easier to Debug
Explore strategies to enhance syzbot bug reports for more efficient kernel debugging. Share experiences and suggest improvements to streamline the process and better serve the Linux community.
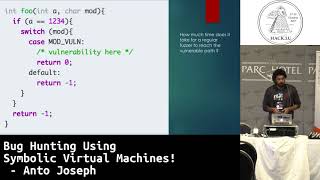
Bug Hunting Using Symbolic Virtual Machines - Hack.lu 2017
Explore symbolic execution for vulnerability discovery and reverse engineering. Learn KLEE symbolic virtual machine basics to solve complex challenges in software security.
Fuzz Everything, Everywhere, All at Once - Advanced QEMU-Based Fuzzing
Explore advanced QEMU-based fuzzing techniques for binary-only targets, including command and SQL injection detection, and scalable Android library testing without physical devices.