Control-Alt-Hack - White Hat Hacking for Fun & Profit
Explore ethical hacking through a card game that simulates security audits and consulting. Learn about diverse hacking skills, mission challenges, and cybersecurity concepts in an engaging, entertaining format.
State of Web Exploit Toolkits
Deep dive into popular web exploit toolkits, analyzing construction, shellcodes, obfuscations, and exploits. Explore trends, data harvesting methods, and emerging players in cybercriminal landscape.
SQL Injection to MIPS Overflows - Rooting SOHO Routers
Explore SQL injection techniques to exploit buffer overflows and gain root access to Netgear routers, including file extraction and live demonstration of vulnerabilities in SOHO devices.
Easy Local Windows Kernel Exploitation
Discover reliable techniques for exploiting common local Windows kernel vulnerabilities across multiple versions, including previously challenging exploits.
Owning Bad Guys and Mafia with Javascript Botnets
Explore mitm attacks on anonymous services and learn to create JavaScript botnets for analyzing connections, uncovering activities of malicious actors behind these services.
SQL Injection Detection - Joint Force Database Auditing & Anomaly Intrusion Detection
Explore advanced SQL injection detection techniques, combining database auditing and anomaly intrusion detection for enhanced cybersecurity measures.
Beyond EIP
Explore advanced exploitation techniques beyond EIP, including OP sled, return addresses, and encoders. Learn about payloads and stagers for enhanced post-exploitation capabilities.
Owning the C-suite - Corporate Warfare as a Social Engineering Problem
Explore social engineering tactics in corporate espionage, focusing on vulnerabilities in executive-level security and strategies for protecting high-value targets in organizations.
Computer Security - Textbook View
Explore computer security challenges, from software design to system management, with insights on trust issues, complexity, and evolving threats in the digital landscape.
The Issues Surrounding the Hiring of Hackers
Explore ethical considerations and practical challenges of employing individuals with hacking backgrounds in cybersecurity roles.
Next Generation Clickjacking
Explore advanced clickjacking techniques, including data injection and extraction, cross-browser vulnerabilities, and a new tool for creating multi-step attacks on web applications.
Huawei - From China with Love
Exploring vulnerabilities in 3G/4G USB modems, focusing on Huawei devices. Discusses potential for widespread infection and botnet creation through software exploits.
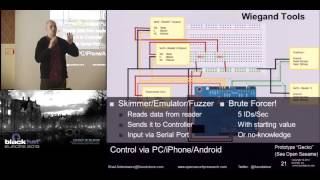
Using D-Space to Open Doors
Explore vulnerabilities in proximity card access systems, from RFID tags to backend databases. Learn attack techniques through demonstrations on popular deployments.
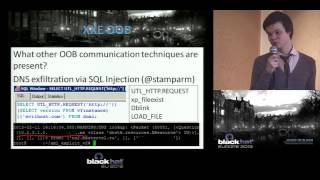
XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.
Practical Exploitation Using A Malicious Service Set Identifier - SSID
Explore SSID exploitation techniques for wireless device attacks, including XSS, CSRF, and command injection. Learn about limitations, risk factors, and see live demonstrations of these methods.
Let's Play - Applanting
Discover a new attack methodology called APPLANTING, which allows attackers to install apps on Android devices without user knowledge, combining CSRF and clickjacking techniques.
The Deputies Are Still Confused
Exploring misunderstandings and vulnerabilities in same-origin policy, with practical examples of attacks bypassing common content-isolation mechanisms for CSRF, clickjacking, and NTLM protection.
Honeypot That Can Bite - Reverse Penetration
Explore aggressive honeypot techniques for de-anonymizing attackers, assessing skill levels, and gaining control. Learn real-world applications and effectiveness through case studies and practical examples.
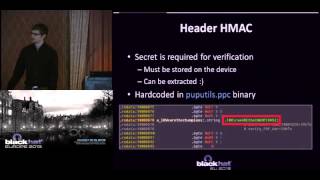
Hacking Video Conferencing Systems
Explore vulnerabilities in high-end videoconferencing systems, focusing on Polycom HDX devices. Learn about firmware analysis, device rooting, and remote exploitation techniques for H.323 protocol.
Using Online Activity as Digital Fingerprints to Create a Better Spear Phisher
Explore data mining and NLP techniques to profile online activity, creating digital fingerprints for enhanced social engineering. Learn to analyze user interactions, vocabulary, and communication patterns.
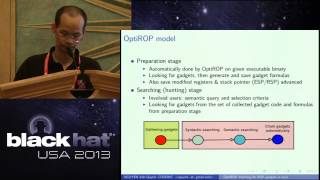
OptiROP - Hunting for ROP Gadgets in Style
Discover efficient ROP gadget hunting with OptiROP, a tool using semantic queries for quick, precise results across executable formats on x86/x64 architectures. Simplify shellcode development.