Parrot Drones Hijacking
Explore drone architecture, communication protocols, and reverse engineering techniques. Learn to assess security, develop new methodologies, and implement best practices for securing drone environments.
Purple Dome - Kein Schwein greift mich an
Simulationsumgebung für Hacking-Angriffe: Testen von Sicherheitssystemen, Beobachtung von Reaktionen und Verbesserung der Systemhärtung mit Purple Dome.
Where Do You Draw The Line?
Explore ethical boundaries in cybersecurity with Patricia R. Gain insights on navigating complex moral dilemmas and making principled decisions in the field.
Exploiting Linux Capabilities
Explore Linux capabilities exploitation techniques, enhancing your understanding of system security vulnerabilities and potential attack vectors in Unix-like environments.
Introduction to Bug Hunting
Learn essential techniques and strategies for identifying and reporting software vulnerabilities, enhancing your skills in ethical hacking and cybersecurity.
Cameras, CACs & Clocks - A Story of Millions of Interrogated and Hacked xIoT Devices
Demonstración en vivo de ciberataques a dispositivos IoT, con hallazgos de investigación de seguridad y técnicas de mitigación de amenazas para proteger contra actores maliciosos.
Growing Your Skillset with Capture the Flag
Strategies for maximizing learning in Capture the Flag competitions, including tips for beginners and insights from an organizer's perspective on tackling new topics effectively.
HALT AND CATCH FIRE - Social Engineering CTFs for Fun to a Job as a Professional Red Team Social Engineer
Explore the transition from social engineering competitions to professional red team engagements, examining the differences in tactics, strategies, and real-world applications.
I Hope This Sticks - Analyzing ClipboardEvent Listeners for XSS
Explore ClipboardEvent listeners as potential XSS vectors in web applications. Learn techniques for identifying and exploiting vulnerabilities to enhance your offensive security skills.
Story of an RCE on Apple Through Hot Jar Swapping
Discover how Frans Rosen achieved remote code execution on Apple through hot jar swapping. Learn about the research, exploit, and analysis behind this impressive security finding.
A Heaven for Hackers - Breaking Web Security Virtual Appliance
Explore web security vulnerabilities and hacking techniques through hands-on demonstrations, focusing on methodology, enumeration, and exploitation of common weaknesses in web applications.
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.
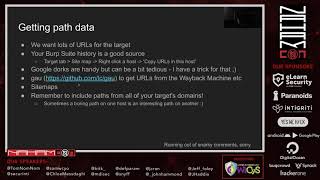
Who, What, Where, When, Wordlist
Explore techniques for creating and utilizing effective wordlists in cybersecurity, including target-specific lists, data processing, and practical applications for bug hunting.
The Pwning Machine - An Easy to Setup Pwning Station
Explore the Pwning Machine, an easy-to-setup hacking environment. Learn about its features, including a basic server, markdown editor, and pipeline runner for efficient cybersecurity tasks.
How to Use Amass Efficiently
Comprehensive guide on maximizing Amass tool for efficient information gathering and reconnaissance in cybersecurity, presented by expert Jeff Foley at NahamCon2020.
You've Got Pwned - Exploiting E-Mail Systems
Explore email system vulnerabilities and exploitation techniques in this informative talk by @securinti, covering key security risks and potential attack vectors.
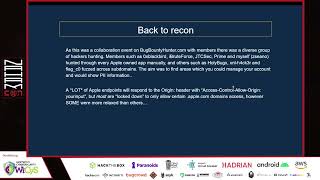
Finding XSS on Apple.com and Building a Proof of Concept to Leak Your PII
Discover how to find XSS vulnerabilities on high-profile websites and create effective proof-of-concept exploits to demonstrate potential data leakage risks.
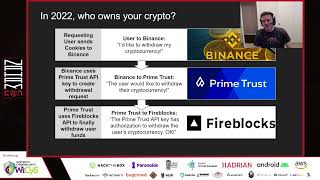
Breaking Into Cloud Wallets - Hacking Crypto Web Apps
Explore cloud wallet vulnerabilities and crypto web app hacking techniques in this talk by @samwcyo, covering blind XSS, SQL injection, and account takeovers in the cryptocurrency ecosystem.
Effectively Finding Vulnerabilities by Debugging the Source Code
Discover effective techniques for identifying vulnerabilities through source code debugging. Learn to enhance your bug hunting skills and improve your ability to find security flaws in software.

Finding 0days in Enterprise Web Applications
Explore techniques for finding 0-day vulnerabilities in enterprise web applications, focusing on HCL Digital Experience, Solarwinds Web Help Desk, and Sitecore's Experience Platform.
Career and Community Building with Bug Bounties
Panel discussion on leveraging bug bounties for career growth, knowledge expansion, and community building in infosec. Experts share insights on how bug bounties have impacted their professional journeys.