Catch Me, Yes We Can - Pwning Social Engineers Using Natural Language Processing Techniques in Real-Time
Explore techniques to detect and prevent social engineering attacks across various communication channels using content-based analysis and natural language processing.
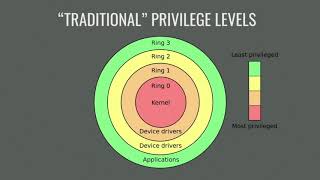
Why so Spurious? Achieving Local Privilege Escalation on Operating Systems
Explore a critical x86 architecture vulnerability exploitable for local privilege escalation across Windows, macOS, and Linux. Learn about this widespread security issue and its implications.
Pre-built JOP Chains with the JOP ROCKET - Bypassing DEP without ROP
Explore Jump-oriented Programming (JOP) as an alternative to ROP for code-reuse attacks. Learn about the JOP ROCKET tool for creating pre-built JOP chains to bypass DEP without ROP.
Vibe Check - Why Students May Shy Away From Cyber in a Surveillance State
Explores impact of surveillance and strict laws on cyber talent in Asia Pacific, discussing challenges for ethical hacking and threat research in a censorship-heavy environment.
Alarm.DISARM - Remotely Exploiting & Disarming Popular Physical Security System from Public Internet
Explore remote code execution vulnerabilities in physical security systems, learning to exploit and disarm alarms through reverse engineering and network protocol analysis.
New Attack Surface in Safari - Using Just One Web Audio Vulnerability to Rule Safari
Explores a novel attack surface in Safari, focusing on vulnerabilities in system libraries like audio. Demonstrates how a single Web Audio vulnerability can be exploited to compromise Safari's security.
Fingerprint-Jacking - Practical Fingerprint Authorization Hijacking in Android Apps
Practical exploration of fingerprint authorization vulnerabilities in Android apps, demonstrating attack techniques and suggesting mitigation strategies for developers.
Light Commands - Hacking Voice Assistants with Lasers
Explore how lasers can manipulate voice-activated IoT devices, revealing potential security vulnerabilities in smart home technology and microphone systems.
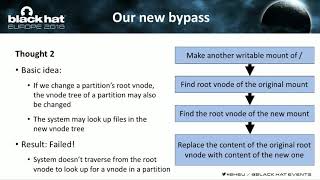
The Last Line of Defense - Understanding and Attacking Apple File System on iOS
Explore APFS architecture, previous attacks, and a new method to bypass mitigations, potentially compromising iOS file system security.
Automating Exploit Generation for Arbitrary Types of Kernel Vulnerabilities
Explore automated exploit generation techniques for kernel vulnerabilities, reducing development time from thousands of hours to minutes and enhancing cybersecurity practices.
Playback - A TLS 1.3 Story
Explore TLS 1.3's 0-RTT feature, its risks, and real-world replay attacks. Learn about potential solutions and mitigation controls for secure deployment of TLS 1.3-supported software.
The Hidden RCE Surfaces That Control the Droids
Uncover hidden vulnerabilities in Android OS libraries that process incoming files, potentially leading to remote code execution attacks on various system applications.
AutoSpear - Towards Automatically Bypassing and Inspecting Web Application Firewalls
Explore techniques for automatically bypassing and inspecting web application firewalls, examining vulnerabilities in WAF-as-a-service solutions and cloud security services.
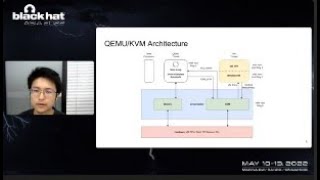
Hunting and Exploiting Recursive MMIO Flaws in QEMU KVM
Explore security vulnerabilities in QEMU/KVM hypervisors caused by recursive MMIO handling, uncovering a new attack surface with potential for critical exploits in cloud computing environments.
Windows Heap-backed Pool - The Good, the Bad, and the Encoded
Explore Windows kernel pool's evolution, new design complexities, and potential vulnerabilities. Learn about structure changes, exploitation techniques, and analysis tools for kernel pool security.
Typhoon Mangkhut - One-click Remote Universal Root Formed with Two Vulnerabilities
Exploit chain for remote Android root using Chrome and Binder vulnerabilities. Demonstrates bypassing security mitigations to achieve one-click root access on modern Pixel devices.
Remote Exploitation of an Unaltered Passenger Vehicle
Comprehensive exploration of remote vehicle hacking, demonstrating real-world attacks on unaltered cars and pivoting through hardware to send CAN bus messages affecting critical systems.
Rocking the Pocket Book - Hacking Chemical Plant for Competition and Extortion
Explore techniques for exploiting chemical plant systems to cause economic damage while avoiding detection. Learn about attack stages, cost considerations, and creating misleading forensic evidence.
Adventures in Femtoland - 350 Yuan for Invaluable Fun
Explore vulnerabilities in 3G/4G networks using femtocells. Learn to intercept data and exploit weaknesses in UMTS infrastructure, from unboxing to proof-of-concept demonstrations.
CrackLord - Maximizing Password Cracking Boxes
Explore distributed password cracking with CrackLord, a scalable system for load balancing GPU and CPU resources across multiple hardware systems, enhancing efficiency and accessibility.
Subverting Satellite Receivers for Botnet and Profit
Exploiting vulnerabilities in satellite receivers to build botnets, highlighting risks in DVB-CA encryption, custom plugins, and CCCAM protocol. Demonstrates potential for large-scale network compromise and unauthorized access.