IPvSeeYou - Exploiting Leaked Identifiers in IPv6 for Street-Level Geolocation
Explore a data fusion attack on IPv6 home routers for precise street-level geolocation, uncovering millions of devices worldwide and discussing privacy implications.
Enter Sandbox
Explore automated seccomp filter generation for Linux applications, enhancing security through sandboxing and system call restrictions without manual developer intervention.
Give Me a SQL Injection, I Shall PWN IIS and SQL Server
Explore SQL injection vulnerabilities in IIS and SQL Server, uncovering unexpected attack vectors and their implications for Microsoft's ecosystem security.
Cross-Site Escape - Pwning macOS Safari Sandbox the Unusual Way
Explore a novel attack on macOS Safari sandbox using Cross-Site Scripting, achieving native code execution outside the sandbox without re-exploiting WebKit twice.
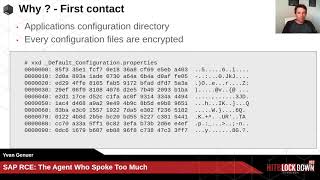
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.
How to Hack Medical Imaging Applications via DICOM
Explore critical security vulnerabilities in DICOM servers, protocols, and libraries used in medical imaging systems. Learn to identify and fix bugs in the DICOM ecosystem.
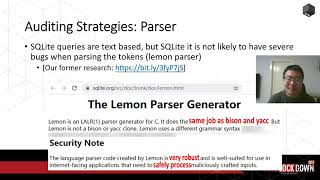
Exploring and Exploiting the SQLite
Explore SQLite vulnerabilities, auditing strategies, and fuzzing techniques. Learn about Magellan 2.0, shadow tables, and bypassing defense mechanisms for remote code execution in Chrome and SQLite binaries.
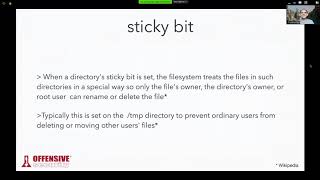
Exploiting Directory Permissions on macOS
Explore macOS directory permission vulnerabilities, from arbitrary overwrites to privilege escalation. Learn techniques to control file contents and understand the intricacies of macOS security.
The Insecurity of Cloudless Smart Door Systems
Explore vulnerabilities in cloudless smart door systems for large buildings, focusing on IP-gateway security risks and potential exploits in intercom-IP integration.
NTLM Relay Is Dead, Long Live NTLM Relay
Explore NTLM relay attacks, their evolution, and modern exploitation techniques. Learn about vulnerabilities in Windows protocols and browsers, with insights on defense strategies.
Over the Edge - Pwning the Windows Kernel
Exploración detallada del subsistema gráfico de Windows, vulnerabilidades del kernel y técnicas de escape del sandbox de Edge, con demostraciones de exploits para elevar privilegios desde el proceso de contenido de Edge a SYSTEM.
Hacking a Hospital for Fun and Profit
Revealing security vulnerabilities in hospital networks through penetration testing, exposing risks in medical devices, software, and systems for improved healthcare cybersecurity.
A Deep Dive Into Malicious Documents
Comprehensive analysis of malicious Office documents, covering macro analysis, obfuscation techniques, shellcode execution, and OS X targeting. Equips attendees to handle various maldoc threats.
Stealing PLC Intellectual Property - A Red Teaming Story
Exploring a real-world Red Team operation to steal industrial recipes from PLCs, detailing preparation, physical intrusion, and ICS device hacking techniques in manufacturing environments.
Exploiting Windows Automatic Wireless Association
Exploiting Windows automatic wireless association with "Lure10" technique. Demonstrates man-in-the-middle attack using Wifiphisher tool. Discusses WiFi security, countermeasures, and protection strategies across operating systems.
We Hacked The Planet - Now What?
Explore the evolution of cybersecurity, from hacking to bug bounties, and its impact on policy, workforce, and vulnerability management. Gain insights into future challenges and solutions.
Car Hacking - Practical Guide to Automotive Security
Practical guide to automotive security, focusing on CAN bus hacking. Learn to reverse-engineer packets, identify arbitration IDs, perform replay attacks, and explore hardware tools for vehicle network security.
Security Should Be Smarter Not Harder
Explore cybersecurity strategies, bug bounty programs, and hacker motivation with Katie Moussouris. Learn about industry myths, perverse incentives, and practical solutions for smarter security practices.
Hacking Jenkins
Exploring Jenkins vulnerabilities, including dynamic routing misuse and Groovy sandbox escape. Learn to build custom gadgets and exploit Jenkins through unconventional methods.
Sneaking Past Device Guard
Exploración de técnicas avanzadas para eludir Device Guard en Windows 10, incluyendo métodos que requieren privilegios de administrador y otros que utilizan aplicaciones nativas del sistema operativo.

SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.