Knock Knock, Who's There? Identifying Assets in the Cloud - Ben Sadehipour - Ekoparty Security Conference - 2020
Descubre técnicas para identificar activos en la nube y cazar vulnerabilidades en programas de recompensas, con ejemplos prácticos y herramientas útiles.
Social Engineering - Lateral Phishing Attack - Jorge Martin Vila - Ekoparty Security Conference - 2020
Explora técnicas de ingeniería social y phishing lateral, analizando casos reales y estrategias defensivas para mejorar la seguridad en entornos empresariales.
How to Cook Cisco: Exploit Development for Cisco IOS - George Nosenko - Ekoparty Security Conference - 2017
Exploración técnica de vulnerabilidades en Cisco IOS, incluyendo bypass de DEP, ROPing, shellcode en etapas y evasión de mecanismos de integridad. Incluye demostraciones prácticas y código fuente.
Hacking RFID Billing Schemes for Fun and Free Rides - Marcio Almeida Macedo - Ekoparty Security Conference - 2014
Explore RFID vulnerabilities in MIFARE Classic cards, focusing on public transport systems. Learn about attack methods, countermeasures, and real-world implications for security professionals.
Android Security, or This Is Not the Kind of 'Open' I Meant
Explore Android security vulnerabilities, reverse engineering techniques, and potential solutions with insights from Trustwave SpiderLabs expert Mike Park.
Pwning Intranet with HTML 5
Explore HTML5's potential for intranet exploitation using BeEF framework. Learn footprinting, network discovery, port scanning, and inter-protocol exploitation techniques.
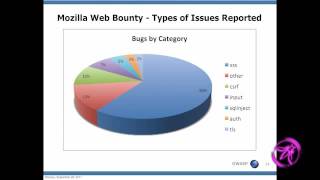
Security Evolution - Bug Bounty Programs for Web Applications
Explore the evolution of web security through bug bounty programs, focusing on Mozilla's experience, benefits, challenges, and ethical considerations.
Hacking .NET Applications - The Black Arts
Explore techniques for hacking .NET applications, including malware analysis, code review, and penetration testing. Learn to build keygens, cracks, and overcome security measures in .NET environments.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
Fixing XSS with Content Security Policy
Explore Content Security Policy (CSP) as a defense against XSS attacks, comparing CSP 1.0 and 2.0, and learn implementation strategies for enhanced web application security.
Be Mean to Your Code - Rugged Development & You
Pragmatic approaches and tools for ruggedizing your development lifecycle, from code commit to running system. Learn solutions for secure, resilient applications in fast-paced environments.
We Are the Cavalry - Why It Has to Be Us and Why Now
Exploring cybersecurity challenges in the Internet of Things era, emphasizing the need for proactive measures and collective responsibility to address emerging risks and protect human safety.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without leaving traces. Learn about the scalability and potential risks of this attack scenario.
Riding the Magical Code Injection Rainbow
Explore advanced exploitation techniques for SQL injection, XPath injection, cross-site scripting, and shell command injection using the Magical Code Injection Rainbow framework for configurable vulnerable applications.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
Working with Developers for Fun and Progress
Practical strategies for building strong relationships with developers to create an impactful AppSec program, featuring competition-based training, tooling implementation partnerships, and codebase contributions.
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and sharing real-world implementation flaws in bot prevention systems.
FIESTA - An HTTPS Side-Channel Party
Explore HTTPS side-channel vulnerabilities and a new tool, FIESTA, for testing and exploiting these issues. Learn about a novel side-channel affecting major tech companies and its implications for online security.
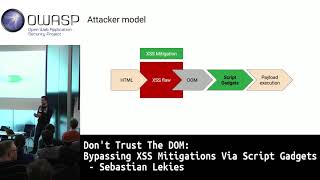
Don't Trust the DOM - Bypassing XSS Mitigations via Script Gadgets
Explores novel XSS attack technique using script gadgets to bypass mitigations, demonstrating vulnerabilities in modern JavaScript libraries and advocating for preventive security measures.
Security Vulnerabilities Decomposition - Another Way to Look at Vulnerabilities
Explore security vulnerabilities decomposition, focusing on SQL injection, secure data handling, and design patterns for payment gateways and single sign-on. Learn practical security controls for secure development.
XSS is Dead - We Just Don't Get It
Exploración crítica de la persistencia del XSS, analizando su historia, fracasos en su mitigación y factores que contribuyen a su continuidad. Se cuestiona su relevancia actual y se proponen reflexiones sobre el futuro de la seguridad web.