A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.

Raining CVEs on WordPress Plugins with Semgrep
Leveraging Semgrep to identify vulnerabilities in WordPress plugins, reducing false positives, and automating XSS validation. Includes demos on custom rule creation and the XSSBomb tool.
Stack Buffer Overflow Exploits - Wie ein "harmloses" Dokument einen Rechner infizieren kann
Erklärung und Demonstration von Stack Buffer Overflow-Exploits für Nicht-Fachleute. Zeigt anschaulich, wie scheinbar harmlose Dokumente Rechner infizieren können, mit Live-Demo.
Venenerkennung hacken
Enthüllung der Schwachstellen von Venenerkennungssystemen: Methoden zur Überwindung dieser als sicher geltenden biometrischen Technologie werden demonstriert und diskutiert.

Finally - Venenerkennung hacken
Entdecken Sie die Schwachstellen der Venenerkennung: Neueste Forschungsergebnisse und Hacking-Methoden für dieses als sicher geltende biometrische Verfahren.
In Soviet Russia Smart Card Hacks You
Explore vulnerabilities in smart card drivers and middleware through fuzzing and auditing, revealing security flaws that challenge assumptions about smart card trustworthiness.
What the Flag is CTF?
Explore the world of Capture The Flag (CTF) competitions: their history, types of challenges, and how to get started. Learn about this exciting way to improve your cybersecurity skills and join a global community.
What the Fax?
Exploración de vulnerabilidades en máquinas de fax, demostrando cómo comprometer redes a través de líneas telefónicas y exponiendo riesgos de seguridad en tecnología obsoleta pero ampliamente utilizada.
Compromising Online Accounts by Cracking Voicemail Systems
Explore techniques for compromising voicemail systems, leveraging old and new methods. Learn the far-reaching impacts and preventive measures for securing online accounts.
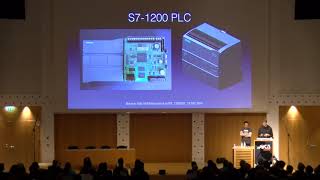
A Deep Dive Into Unconstrained Code Execution on Siemens S7 PLCs
Explore unconstrained code execution on Siemens S7 PLCs, revealing bootloader vulnerabilities and security implications. Learn about the special access feature and its potential for exploitation or forensic use.
Messenger Hacking - Remotely Compromising an iPhone through iMessage
Detailed exploration of a remote iPhone exploit via iMessage, covering vulnerability analysis, exploitation techniques, and mitigation strategies for mobile OS and messenger security.
SDR - Was ist eigentlich sonst noch im Äther
Einblick in Software Defined Radio und dessen Anwendung bei Zutrittssystemen. Analyse von UHF-Transpondern, Sicherheitsaspekte und ethische Überlegungen zur Aufklärung über potenzielle Schwachstellen in Funksystemen.
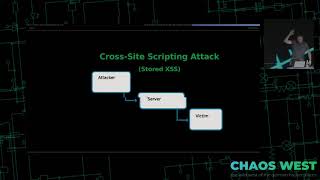
Nothing New About XSS in Impress.js
Demonstrating XSS vulnerabilities in impress.js presentations, showcasing innovative features like a 3D cockpit view and dynamic slide content manipulation for enhanced interactivity and visual appeal.
Next-Gen IoT Botnets - Bad Implementations of Good Cloud Platforms
Explore security vulnerabilities in IoT cloud platforms, including authentication bypasses and remote code execution. Learn about the risks of poor implementations and their widespread impact on connected devices.
Hacking Your Cybersecurity Career
Learn techniques to break into cybersecurity, including visualizing goals, social engineering, active learning, and skill sharpening. Discover traits of successful professionals and navigate the career triad for optimal job prospects.
BADPDF - Stealing Windows Credentials via PDF Files
Discover how PDF files can be weaponized to automatically leak Windows NTLM hashes, potentially compromising user credentials without interaction.
Tales of Red Teaming - Continuous Intrusion Continuous Deception
Explore advanced red teaming techniques for attacking large corporate networks, including compromising deployment systems, backdooring software, breaking out of containers, and exploiting misconfigurations in multi-tenant systems.
Ethical Hacking - DIY Mobile Security Workstation for Cheap
Learn to build a cost-effective mobile security workstation using affordable parts and open-source software. Discover how to create a powerful system capable of running Kali Linux or Parrot OS for ethical hacking and network testing.
Journey to Command Injection - Hacking the Lenovo ix4-300d
Demonstration of chaining vulnerabilities to remotely exploit a Lenovo NAS device, showcasing command injection, XSS, and CSRF techniques for full system compromise.
Abusing WCF Endpoint for RCE and Privilege Escalation
Explore WCF vulnerabilities in .NET programs, focusing on privilege escalation and remote code execution. Learn to identify and exploit these bugs through a real-world case study.
Hacking the Unhackable - Pwning the Bitfi Crypto Wallet
Explore the security flaws in the Bitfi crypto wallet, learn from its mistakes, and understand best practices for secure device development and responsible disclosure.