Modern Web Application Defense with OWASP Tools
Learn to defend web applications using OWASP tools. Explore XSS, CSRF, and other vulnerabilities through live demos. Gain practical skills to prevent attacks and secure your applications effectively.
Improving Penetration Testing Efficiency with OWASP Code Pulse and Attack Surface Detector
Explore OWASP tools for efficient web app penetration testing: Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery, enhancing security assessment capabilities.
Serverless Infections - Malware in Serverless Computing Environments
Explore security risks in serverless computing, including potential malware infections and data exfiltration. Learn about a novel RCE attack and best practices for securing serverless environments.
Novel Exploitation Techniques in WordPress - Prepared Statements and Object Injection
Explore novel WordPress exploitation techniques, focusing on a core design flaw leading to SQL injection and PHP object injection vulnerabilities. Learn prevention strategies for developers.
Android App Protection Techniques: Obfuscation, Packing, and Protection - APPSEC Cali 2018
Explore Android app protection techniques, including obfuscation, packing, and protection. Learn to analyze and counter these methods to identify potential malware and enhance app security.
Juice Shop - OWASP's Most Broken Flagship
Explore OWASP's intentionally vulnerable web application, learn about its features, and discover how it can enhance your web security skills through hands-on hacking challenges.
Endpoint Finder: A Static Analysis Tool for Web Endpoint Discovery - Lightning Talk
Discover a static analysis tool for extracting web endpoints from JavaScript files, offering improved accuracy and reduced false positives compared to regex-based methods.
New Web Platform Security Features to Protect Modern Web Applications
Explore modern web browser security features to protect against XSS, CSRF, and clickjacking. Learn about CSP3, Trusted Types, Fetch Metadata Request Headers, CORP, and COOP for enhanced application security.
NOSQL Web Application Vulnerabilities and Mitigation
Explore NOSQL database vulnerabilities, including injection methods and CSRF, and learn mitigation strategies for enhanced security in web applications.
How I Could Have Stolen Your Photos From Google
Uncover a critical security vulnerability in Google Photos and learn how it could have compromised user privacy. Gain insights into responsible disclosure and ethical hacking practices.
OWASP Security Shepherd - Mobile and Web Security Awareness and Education
Explore web and mobile app security risks through interactive lessons and challenges. Improve penetration testing skills and understand vulnerabilities using OWASP Security Shepherd's comprehensive platform.
Hacking Fantasy Sports Sites - Mobile App Security Vulnerabilities
Explore mobile app vulnerabilities through fantasy sports hacking. Learn techniques for intercepting traffic, exploiting formats like JSON and REST, and manipulating data in popular applications.
Building the Cloud Native Reference Architecture for Telco Cloud - Update on Anuket RA2
Explore the latest developments in Anuket RA2, a cloud-native reference architecture for telco cloud, including its structure, components, and how to get involved.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
OWASP Juice Shop Project
Explore web application security with OWASP's intentionally vulnerable Juice Shop, learning about common vulnerabilities and how to exploit and defend against them.
ATOR - Authentication Token Obtain and Replace Burp Plugin V3
Streamline complex authentication testing with ATOR v3 Burp Plugin. Automate token handling, OTP validation for JavaScript frameworks. Simplifies configuration and debugging for efficient security assessments.
Breaking and Fixing Web Application Security
Explore web application security challenges, attack vectors, and proactive measures. Learn to identify vulnerabilities, implement secure coding practices, and safeguard user data in the digital realm.
Progress on Bounds Checking in C and the Linux Kernel
Explore advancements in C bounds checking for Linux, focusing on flex array members, dynamic object size, and new struct member attributes to prevent buffer overflow vulnerabilities.
Fuzz Everything, Everywhere, All at Once - Advanced QEMU-Based Fuzzing
Explore advanced QEMU-based fuzzing techniques for binary-only targets, including command and SQL injection detection, and scalable Android library testing without physical devices.
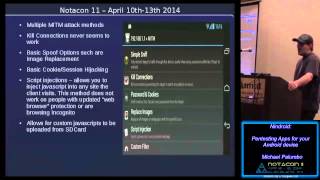
Nindroid Pentesting Apps for Your Android Device
Explore essential Android pentesting apps for mobile security assessments, enhancing your device's capabilities for ethical hacking and vulnerability detection.