Beyond Android MTE: Navigating OEM's Logic Labyrinths
Explore advanced Android security, focusing on Memory Tagging Extension (MTE) and OEM-specific implementations. Gain insights into exploiting vulnerabilities in custom logic.
Open Sesame: Stack Smashing Your Way into Opening Doors
Explore stack smashing techniques to bypass security measures in electronic door locks, uncovering vulnerabilities and potential exploits in physical access control systems.
Impacket Tools for Pentesting Secure Environments - 02-11-2023
Explore advanced pentesting techniques for secure environments using Responder, CrackMapExec, and Impacket utilities. Enhance your cybersecurity skills.
The Route to Success: Hacking a Router to Its End of Life
Explore the process of hacking a Trendnet travel router, from vulnerability hunting to exploit development. Learn methodologies and tools for both newcomers and veterans in IoT security.
How Hacking Works - Web Edition - NDC Oslo 2024
Explore web exploitation techniques and tools to enhance software security through gamified environments. Learn to think like a hacker for safer development.
Writing Powerful Penetration Testing Reports
Learn strategies for crafting effective penetration testing reports, including key components, proof-of-concept creation, and common pitfalls to avoid. Enhance your ability to deliver impactful security assessments.
Protecting Small Businesses from Cyber Attacks - Strategies and Real-World Scenarios
Explore attacker strategies, real-world scenarios, and cost-effective measures to protect small businesses from cyber threats. Learn to engage employees through gamification for enhanced security.
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
ARP Spoofing and Poisoning: Understanding Man-in-the-Middle Attacks - Demo
Explore ARP spoofing: its mechanics, targets, consequences, and prevention. Learn to safeguard your network against this malicious technique that disrupts communication and intercepts data.
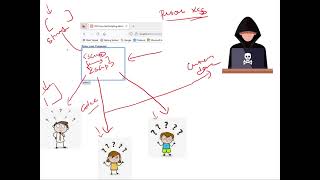
Persistent XSS (Cross-Site Scripting) Attack: What It Is and How to Prevent It
Explore persistent XSS attacks, witness a live demo, and learn effective prevention strategies to enhance web application security.

Ethical Hacking: Using Metasploit to Crack Passwords
Explore ethical password cracking using Metasploit. Learn to create dictionaries, launch attacks, and understand techniques for responsible penetration testing and system security enhancement.
Nikto Web Vulnerability Scanner - Web Penetration Testing
Learn to identify web vulnerabilities using Nikto, an open-source scanner. Explore its features and enhance your web application security skills.
Metasploit Framework Introduction - Modules in Metasploit
Explore Metasploit's core modules: Auxiliary, Exploit, Payload, Encoder, Evasion, and Post-Exploitation. Learn their functions and applications in penetration testing.
Social Engineering Attack Using Mass Mailer in Kali Linux - Demo
Discover how to execute a mass mailing attack using Kali Linux's setoolkit, exploring social engineering techniques for educational purposes.
Nation-State Threats in the Open-Source Software Supply Chain
Explore North Korean cyber threats targeting software developers through malicious npm packages, focusing on Lazarus Group campaigns and their evolving tactics to steal cryptocurrency.
Zero Trust APIs with Python
Explore Zero Trust Security for APIs using Python. Learn to identify and address vulnerabilities, implement robust data validation, and use tools for automated security testing.
Social Engineering - Hacking People
Learn to recognize and defend against social engineering attacks, enhancing your cybersecurity awareness and protecting yourself from manipulation.
When Not to Use a Web Application Firewall and Its Alternatives - Lecture
Explore when to avoid Web Application Firewalls (WAFs) and learn their limitations. Understand WAF architecture, common web threats, and alternative security approaches for effective application protection.
Why We Need Security Domains: A Comprehensive Approach to Cybersecurity
Explore essential cybersecurity domains, from compliance to hacking, and understand their importance in developing comprehensive security strategies for modern organizations.
Building an LLM Vulnerability Scanner to Secure AI Applications
Develop an LLM vulnerability scanner to audit and secure AI applications. Learn about LLM security risks and build a CLI tool for detecting vulnerabilities in AI systems.
Introduction to Risk Analysis and Management in Security - Lecture 7
Comprehensive overview of risk analysis, management, and security incident taxonomy in cybersecurity, covering eavesdropping, denial of service, and cloud computing concepts.