The Good, The Bad and The Ugly of Responsible Disclosure
Explore the complexities of responsible disclosure in cybersecurity, examining its positive aspects, challenges, and potential pitfalls through real-world examples and expert insights.
The Science Behind Social Engineering and Effective Security Culture
Explore the psychological principles behind social engineering and learn strategies for building a robust security culture within organizations.
The Path Towards Automated Heap Exploitation
Explore automated heap exploitation techniques and strategies for enhancing cybersecurity defenses in this insightful conference talk by Thaís Moreira Hamasaki.
Bug Bounty Stories - Hacking Prison
Explore ethical hacking techniques as NahamSec demonstrates breaking out of a virtual prison, showcasing real-world bug bounty strategies and cybersecurity insights.
More Than Just a Pretty Penny - Why You Need Cybersecurity in Your Culture
Discover strategies to integrate cybersecurity into workplace culture, empowering employees to identify and address potential risks, fostering a safer digital environment for your organization.
CTF Overview and Experience - Preparing for SecurityCon
Prepare for SecurityCon's CTF event with a warm-up session covering container breakouts and Kubernetes misconfigurations. Suitable for all experience levels, learn CTF engagement techniques.

The Beginner's Guide to Blind XSS - Cross-Site Scripting
Learn to identify and exploit Blind XSS vulnerabilities, a critical web security flaw. Discover tools like XSS Hunter and gain practical skills for ethical hacking and bug bounty hunting.
Cognitive Security and Social Engineering: A Systems-Based Approach
Explore cognitive security's unique approach to protecting systems, considering interconnectedness and multiple scales. Learn about the Cognitive Security Attack Cycle and strategies for disrupting attacks.
Social Engineering: Training the Human Firewall Against Phishing Attacks
Explore research on psychological factors behind phishing susceptibility and learn strategies to improve security education and measure risk in your organization.
A Hacker's Guide for Changing the World - IATC Capstone
Empowering hackers with strategies for positive global impact, including empathy, storytelling, and cyber-civics, to create meaningful change in the world.
How I Became a Hacker and What I'd Do Differently
Insights into a hacker's journey, offering valuable lessons and advice for aspiring cybersecurity professionals. Learn from real-world experiences to accelerate your path in ethical hacking.
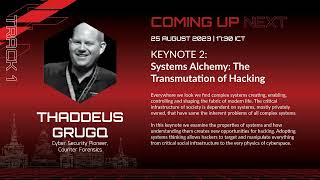
Systems Alchemy: The Transmutation of Hacking
Exploring systems thinking in hacking, this keynote reveals how understanding complex systems creates new opportunities to manipulate critical infrastructure and the fabric of cyberspace.
Ethical Hacking: Good Intentions and Questionable Outcomes
Explore ethical boundaries in security testing, from fuzzing servers to buying dark web credentials. Discuss grey areas and the need for beneficial practices that maintain moral high ground.
Inside the Mind of a Hacker 2023 - Bugcrowd Webinar
Explore hacker insights, AI's impact on cybersecurity, and industry trends with experts. Gain valuable perspectives on ethical hacking, motivations, and the evolving landscape of security research.
Remotely Exploiting the ClamAV Antivirus Engine - CVE-2023-20032 Case Study
Explore a case study on exploiting CVE-2023-20032 in ClamAV, demonstrating remote code execution and ASLR bypass techniques applicable to similar antivirus software vulnerabilities.

Disclosure, Hack and Back - Vulnerability Reporting and Cybersecurity Insights
Explore real-world vulnerability reports and hacking incidents, revealing common mistakes in both corporate security responses and cybercriminal operations. Gain insights into improving cybersecurity practices.
Timekiller: Escape From QEMU/KVM - Exploiting Asynchronous Clock Vulnerabilities
Demonstrating a novel guest-to-host escape exploit in QEMU/KVM using asynchronous clock vulnerabilities. Introduces "Timekiller" technique to turn heap overflow into arbitrary address write, achieving full VM escape.
Injecting Brains Into Blind SQL Injection - Optimizing Data Exfiltration
Innovative approach to optimize Blind SQL Injection using Machine Learning and statistics. Introduces Hakuin, a tool that significantly improves exfiltration speed for database schemas and content compared to standard methods.
Escaping From VMware Workstation Through the Disk Controller
Exploración detallada de una vulnerabilidad en los controladores de disco de VMware Workstation que permite escapar de una máquina virtual, con demostraciones de exploits para Linux y Windows.
Extracting Information from Automotive Internet Units
Techniques for extracting and analyzing firmware from automotive internet modules, focusing on Qualcomm MDM-based units. Covers extraction methods, image analysis, and file system exploration.
Exploiting the Lexmark PostScript Stack
Explore Lexmark PostScript stack exploitation, covering internals, language basics, mitigations, and achieving remote code execution through out-of-bounds read and type confusion vulnerabilities.