Protecting Yourself From Supply Chain Attacks - Trust Is Overrated
Discover practical strategies and tools for validating hardware and software integrity, minimizing supply chain risks, and implementing effective security measures across your technology stack.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.

Private Keys in Public Places - Finding and Exploiting Hidden Encryption Keys
Uncover techniques for finding hidden private keys, certificates, and encryption keys in firmware, with real-world examples from Netgear, Fortinet, and Dell's security vulnerabilities.
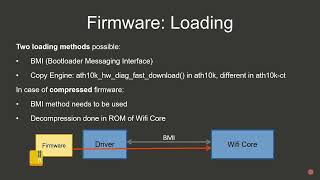
Unlocking Hidden Powers in Xtensa-based Qualcomm WiFi Chips
Dive into firmware modification techniques for Xtensa-based Qualcomm WiFi chips, exploring architecture, patching methods, and security research possibilities using the Nexmon framework.
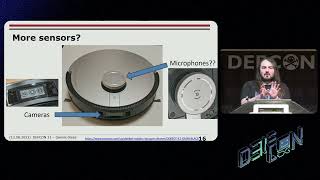
Vacuum Robot Security and Privacy: Preventing Data Collection from Smart Home Devices
Explore security vulnerabilities in smart vacuum robots and learn practical techniques to protect your privacy while maintaining control over these AI-enabled devices.
Abusing CAN Bus Specifications for DoS Attacks in Embedded Systems
Explore CAN bus protocol vulnerabilities in automotive systems, focusing on how attackers can exploit metadata fields and protocol specifications to create denial-of-service attacks in embedded systems.
Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.

Beginner's Guide to Hacking IoT Devices - Building Your First IoT Security Testing Lab
Discover practical IoT hacking techniques, from selecting beginner-friendly devices to building an affordable toolkit under $100. Learn common vulnerabilities and methods to gain device access using simple tools and tactics.
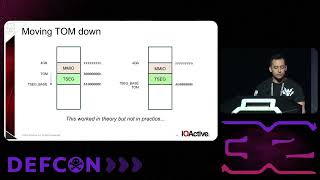
AMD Sinkclose - Universal Ring2 Privilege Escalation in System Management Mode
Delve into AMD processor security vulnerabilities, exploring System Management Mode (SMM), CPU design flaws, and the methodology behind ring-2 privilege escalation exploits.
Breaking the Beam - Exploiting VSAT Modems from Earth
Discover groundbreaking security vulnerabilities in VSAT satellite modems through reverse engineering, exploring software stack exploits and demonstrating wireless signal injection attacks for remote access.
Understanding Authentication Bypass Vulnerabilities in Industrial VPN Gateways
Dive into industrial VPN gateway vulnerabilities through detailed analysis of security flaws, session hijacking risks, and hardware security bypass techniques in remote access systems.
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
How to Make Electronic Conference Badges - From Ideation to Production
Discover the complete badge-making journey, from creative concept to mass production, including circuit design, firmware development, and practical manufacturing insights.
The Hack, the Crash and Two Smoking Barrels - Automotive Cybersecurity Challenges
Dive into automotive cybersecurity challenges through real-world stories and demonstrations, exploring vehicle architecture vulnerabilities and industry practices while witnessing live ECU hacking and security testing scenarios.
Reverse Engineering MicroPython Frozen Modules
Dive into advanced techniques for identifying and reverse engineering frozen MicroPython modules in firmware using Ghidra, focusing on bytecode analysis and module reconstruction methods.
Detecting Persistent Threats on Draytek Devices - Security Assessment and Mitigation Tools
Discover how to detect and mitigate persistent threats on Draytek devices through firmware analysis, reverse engineering, and custom security module development for enhanced network protection.
Security Vulnerabilities in Video Surveillance Systems and Supply Chain Analysis
Explore security vulnerabilities in surveillance systems, focusing on NVR devices from major vendors like Hikvision and Dahua, while examining supply chain risks and exploitation scenarios.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.
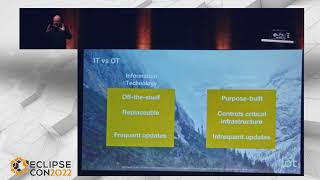
RTOS vs Bare Metal: Choosing the Right Approach for Constrained Devices
Explore the key differences between RTOS and bare metal approaches for IoT development, comparing popular frameworks like FreeRTOS, Zephyr, Arduino, and Espressif IDF.
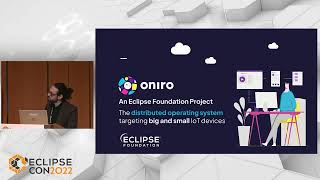
Oniro - Revolutionizing IoT Markets Through Open Source
Discover how Oniro's open-source ecosystem enables seamless IoT device integration, revolutionizing smart appliance connectivity and creating new possibilities for vendor-neutral, royalty-free development.