Netscreen of Death
Explore firmware vulnerabilities, live debugging, and real-world attacks on network security devices. Learn about untrusted code, scripting, and common criteria audits in this technical deep dive.
Bluetooth - Does It Spark Joy?
Explore Bluetooth firmware reverse engineering, security insights, and bug-finding techniques in this deep dive into wireless technology vulnerabilities.
Old New Things - An Examination of the Philips TriMedia Architecture
Explore the Philips TriMedia architecture, examining its history, features, and potential vulnerabilities through firmware analysis and hardware exploration.
Are You Sure - You Are Alone? Pwning IoT-CCTV Devices!
Explore IoT-CCTV device vulnerabilities, learn exploitation techniques, and understand the potential impact on security and privacy in this eye-opening presentation.
Unifying RF Fuzzing Techniques under a Common API - Introducing unfAPI
Explore unified RF fuzzing techniques with a common API, enhancing wireless security testing across various protocols and standards.
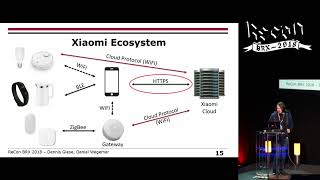
Reversing IoT - Xiaomi Ecosystem
Explore Xiaomi IoT ecosystem security, firmware extraction, and cloud communication. Learn to modify devices, implement new functions, and gain independence from proprietary cloud services.
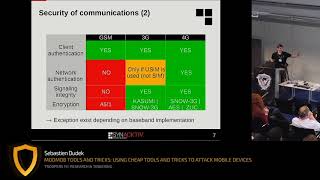
Modmob Tools - Home Made Tools to Test Mobile Devices and Monitor Networks
Explore homemade tools for testing mobile devices and monitoring networks, covering interception techniques, firmware analysis, and hardware auditing for enhanced security understanding.
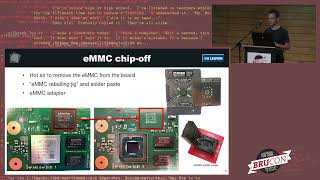
A Black-Box Security Evaluation of the SpaceX Starlink User Terminal
Exploración de seguridad del terminal Starlink: vulnerabilidades, ataques de inyección de fallas y acceso root. Análisis de la red Starlink y sus implicaciones para futuras investigaciones.
ECOS Offensive Security Research Logbook
Explore eCos RTOS security, from firmware analysis to exploitation and persistence. Learn techniques for cable modem research, including memory corruption, shellcode development, and implant creation.
Stealing a Mobile Using Wormholes
Explore mobile network vulnerabilities, SIM card access techniques, and baseband firmware analysis. Learn about "wormholes" in smartphones and their potential for identity theft and unauthorized authentication.
The Mooltipass Open Source Hardware Authentication Ecosystem - Mathieu Stephan - Ekoparty 2021: Hardware Hacking Space
Explore the Mooltipass open-source hardware authentication ecosystem, its components, and innovative features for secure data management and web authentication.
ADS-B and AIS - Open Data Is in the Air - Skymaker, JJX
Explore building a real-time marine & airborne vehicle tracking network using Linux, software-defined radio, and scripts. Learn about ADS-B and AIS technologies for advanced DIY projects.
Defending, Detecting, and Responding to Hardware and Firmware Attacks - Teddy Reed - USENIX Enigma Conference - 2016
Explore firmware security, attack surfaces, and defense strategies. Learn to detect vulnerabilities, monitor integrity, and implement deep systems defense for enterprise protection against hardware and firmware attacks.
Case Studies in Embedded VR - Silvio Cesare - Ekoparty Security Conference - 2022
Explore cutting-edge techniques in embedded VR security, focusing on router vulnerabilities, reverse engineering, and exploit development through real-world case studies.
Modern Secure Boot Attacks - Alex Matrosov - Ekoparty Security Conference - 2019
Explore modern Secure Boot attacks, focusing on bypassing Intel Boot Guard in enterprise systems. Learn about hardware Root of Trust, Embedded Controllers, and UEFI Firmware vulnerabilities.
Exploitation of a Hardened MSP430-Based Device - Braden Thomas - Ekoparty Security Conference - 2014
Reverse-engineering and exploiting a hardened MSP430 device: techniques for firmware extraction, analysis, and data retrieval from RAM, with focus on overcoming JTAG security measures.
OWASP IoTGoat Project Overview and Roadmap
Explore IoTGoat, an OWASP project for IoT security testing. Learn about hardware compatibility, vulnerabilities, and hands-on techniques like firmware extraction and password cracking.
Using the TPM NVRAM to Protect Secure Boot Keys in POWER9 OpenPOWER Systems
Explore TPM NVRAM's role in safeguarding secure boot keys for POWER9 OpenPOWER systems, covering design and implementation aspects in firmware and Linux kernel layers.
Living on Master - Using Yocto Project, Jenkins and LAVA for a Rolling Release
Explore continuous integration for Yocto Project using Jenkins and LAVA, focusing on real-time Linux kernel testing and addressing challenges in maintaining up-to-date embedded systems.
Devicetree
Explore Devicetree tooling updates, overlay progress, and future developments. Engage with a maintainer to address questions and issues in this interactive session on Linux kernel device management.
ACRN - A Big Little Hypervisor for IoT Development
Introducing ACRN: an open-source hypervisor for IoT devices, designed for resource isolation, low latency, and quick boot times. Explore its architecture, virtualization features, and benefits for embedded systems development.