Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Reversing an M32C Firmware - Lessons Learned from Playing with an Uncommon Architecture
Explore techniques for reversing firmware on unfamiliar architectures, focusing on M32C. Learn about interrupt handlers, special registers, and flash handling in embedded systems.
Building a Damned Good Watch
Cloning a calculator watch with added radio capabilities for Morse code transmission, frequency detection, and remote control signal replication. Includes practical insights and open-source code.
Getting Physical with USB Type-C - Windows 10 RAM Forensics and UEFI Attacks
Explore embedded microcontrollers in modern devices, focusing on the Surface Aggregator Module. Learn about security, firmware updates, and potential hardware implants in this deep dive into low-level system architecture.
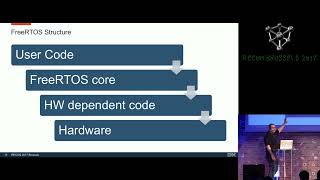
Embedded Devices Reverse Engineering
Explore reverse engineering techniques for embedded devices using FreeRTOS. Learn about memory organization, task handling, and security features. Gain insights into automating the process with IDA scripts for efficient firmware analysis.
This Dump is a Puzzle - Reconstructing J2ME Firmware from an Unknown Fragmented File System
Explore techniques for reconstructing embedded Java firmwares from fragmented file systems, developing puzzle-solving algorithms to piece together unknown J2ME fragments.
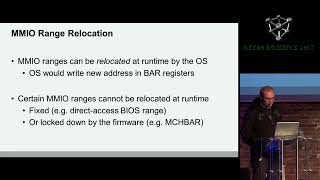
Baring the System - New Vulnerabilities in SMM of Coreboot and UEFI Based Systems
Unveiling new vulnerabilities in SMM of Coreboot and UEFI systems, exploring impacts, and discussing mitigation techniques. Includes release of CHIPSEC module for automatic detection.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
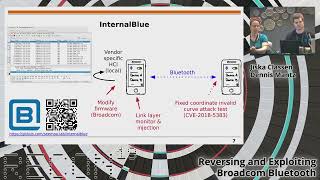
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
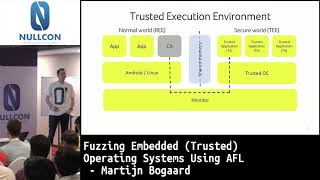
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
Fuzzware - Automating & Scaling Fuzzing For Firmware
Automated firmware testing using Fuzzware: emulate and fuzz embedded systems without hardware. Discover vulnerabilities in network stacks and scale security analysis for diverse devices.
Secure Code Development
Learn secure coding practices for embedded systems in content protection and mobile payments, focusing on real-world asset protection techniques and best practices for software security.
Hacking Automatically - Applying Program Analysis to IoT
Discover how program analysis can uncover vulnerabilities in IoT devices. Learn about firmware analysis challenges, memory corruption patterns, and see 20 real-world examples of security flaws identified through automated techniques.
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
DIY ARM Debugger for Wi-Fi Chips
Explore DIY ARM debugging for Wi-Fi chips using Nexmon framework. Learn to set breakpoints, handle debugging events, and perform single-step debugging on Cortex-R4 microcontrollers in FullMAC Wi-Fi firmwares.
Static Analysis-Based Recovery of Service Function Calls in UEFI Firmware
Discover a new tool for automated recovery of service calls and EFI type info in UEFI firmware, simplifying vulnerability hunting and making firmware code resemble original source.
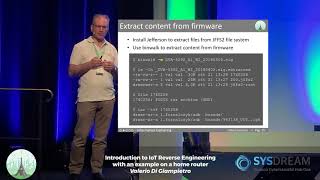
Introduction to IoT Reverse Engineering
Introduction to firmware reverse engineering for IoT devices, focusing on information gathering, emulation environment setup, and analysis techniques. Includes a practical example using a home router.
Assessing IoT with EXPLIoT Framework - Hardware Hacking Space
Explore EXPLIoT, an open-source framework for IoT security testing. Learn how it addresses challenges in IoT assessments, automates tasks, and supports various protocols and technologies.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Exploración de vulnerabilidades en fases tempranas de arranque, evolución de mitigaciones de firmware y nuevos ataques en módulos de evaluación de plataformas Intel desde una perspectiva ofensiva.
Not Yet Another Fuzzer
Explore NYAF, a multi-platform fuzzer using emulation and Generation Search algorithm for improved analysis of IOT devices, embedded systems, and firmware. Learn about its advantages in scalability and efficiency.