Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.

Beginner's Guide to Hacking IoT Devices - Building Your First IoT Security Testing Lab
Discover practical IoT hacking techniques, from selecting beginner-friendly devices to building an affordable toolkit under $100. Learn common vulnerabilities and methods to gain device access using simple tools and tactics.
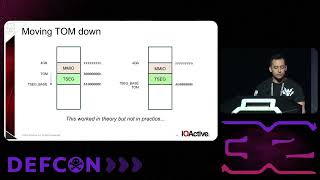
AMD Sinkclose - Universal Ring2 Privilege Escalation in System Management Mode
Delve into AMD processor security vulnerabilities, exploring System Management Mode (SMM), CPU design flaws, and the methodology behind ring-2 privilege escalation exploits.
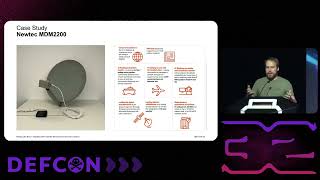
Breaking the Beam - Exploiting VSAT Modems from Earth
Discover groundbreaking security vulnerabilities in VSAT satellite modems through reverse engineering, exploring software stack exploits and demonstrating wireless signal injection attacks for remote access.
Creating Custom Electronic Conference Badges - A Guide to OpenTaxus Design
Learn to design and customize electronic conference badges using OpenTaxus - from hardware modifications in KiCAD to software changes in CircuitPython, plus cost management and production logistics.

Inside the FBI's Secret Encrypted Phone Company Anom - The Dark Wire Investigation
Uncover the fascinating story behind Anom, the FBI-run encrypted phone network that infiltrated criminal organizations, exploring technical details, operational challenges, and surveillance implications.
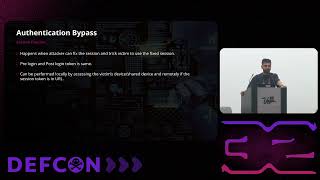
Understanding Authentication Bypass Vulnerabilities in Industrial VPN Gateways
Dive into industrial VPN gateway vulnerabilities through detailed analysis of security flaws, session hijacking risks, and hardware security bypass techniques in remote access systems.
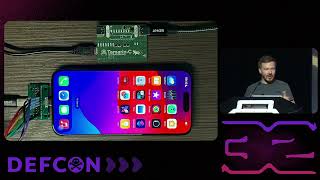
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
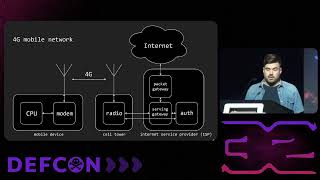
Leveraging Private APNs for Mobile Network Traffic Analysis and Security
Discover how to monitor and control mobile device network traffic using private APNs, enabling affordable security testing and traffic analysis for IoT and mobile devices on 4G/5G networks.
How to Make Electronic Conference Badges - From Ideation to Production
Discover the complete badge-making journey, from creative concept to mass production, including circuit design, firmware development, and practical manufacturing insights.
The Hack, the Crash and Two Smoking Barrels - Automotive Cybersecurity Challenges
Dive into automotive cybersecurity challenges through real-world stories and demonstrations, exploring vehicle architecture vulnerabilities and industry practices while witnessing live ECU hacking and security testing scenarios.
Reverse Engineering MicroPython Frozen Modules
Dive into advanced techniques for identifying and reverse engineering frozen MicroPython modules in firmware using Ghidra, focusing on bytecode analysis and module reconstruction methods.
Detecting Persistent Threats on Draytek Devices - Security Assessment and Mitigation Tools
Discover how to detect and mitigate persistent threats on Draytek devices through firmware analysis, reverse engineering, and custom security module development for enhanced network protection.
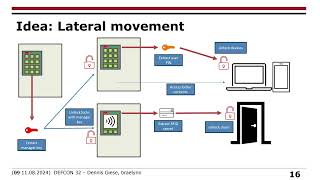
Open Sesame - Vulnerabilities in Electronic Smart Lockers and Cabinets
Explore physical and side-channel vulnerabilities in electronic smart locks, focusing on PIN and RFID security risks in organizational locker systems and shared spaces.
Security Vulnerabilities in Video Surveillance Systems and Supply Chain Analysis
Explore security vulnerabilities in surveillance systems, focusing on NVR devices from major vendors like Hikvision and Dahua, while examining supply chain risks and exploitation scenarios.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.
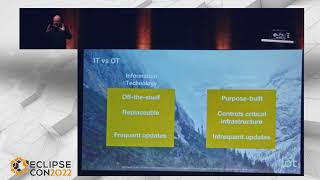
RTOS vs Bare Metal: Choosing the Right Approach for Constrained Devices
Explore the key differences between RTOS and bare metal approaches for IoT development, comparing popular frameworks like FreeRTOS, Zephyr, Arduino, and Espressif IDF.
Oniro - Revolutionizing IoT Markets Through Open Source
Discover how Oniro's open-source ecosystem enables seamless IoT device integration, revolutionizing smart appliance connectivity and creating new possibilities for vendor-neutral, royalty-free development.
Updating Embedded Devices with hawkBit Using Eclipse Hara
Discover how to build efficient DDI API clients for JVM-capable devices using Eclipse Hara's Kotlin library, enabling seamless device updates through hawkBit's DDI protocol.
Eclipse Zenoh - Unifying Communication, Storage and Computation from Cloud to Microcontroller
Discover how Zenoh protocol unifies data management and computation across diverse systems, from cloud infrastructure to microcontrollers, with minimal 5-byte overhead and high performance capabilities.