Investigating Hackers - Stories from Norway's National Cybercrime Center
Insights from police cybercrime investigators on forensic challenges and custom code solutions for extracting crucial data when standard tools fall short.
Recover Quarantined Malware
Explore techniques to safely recover and analyze quarantined malware, enhancing cybersecurity skills and understanding of malicious software behavior.

Who Hacked Who? PsExec Forensic Artifacts
Explore forensic artifacts left by PsExec, a powerful remote administration tool, to uncover evidence of potential hacking activities and enhance your cybersecurity investigation skills.

LinusTechTips Twitter Account Hack - Securing Your Online Presence
Cybersecurity expert analyzes LinusTechTips Twitter hack, offering insights on account security and protection strategies for individuals and businesses against similar threats.

Cyber Threat Hunting and DFIR - Understanding Malware Attack Steps
Explore cyber threat hunting and DFIR techniques, including malware attack paths, detection methods, and essential skills for strengthening organizational cybersecurity defenses.
Breaking Barriers and Boundaries in IT Security - TROOPERS24
Explore cutting-edge IT security insights with experts Alexander Heinrich and Jiska Classen at TROOPERS24 conference, focusing on breaking barriers and pushing boundaries in cybersecurity.
Tales from Incident Response - Unmasking the Threat Actor's Inner Sanctum
Unmasking threat actors' inner workings through incident response tales. Gain insights into cybersecurity challenges and strategies from a principal advisor's real-world experiences at a major hacking conference.
Geolocation and Its Implications
Explore geolocation's impact on cybersecurity with expert Simona David at DefCamp Cluj-Napoca. Gain insights into location-based vulnerabilities and their implications for digital security.
Automating Incident Response: Scalable and Fast, Within Minutes
Discover how to automate incident response using open-source tools, combining digital forensics with DevOps for faster, more efficient security incident handling at scale.
Breaching the Depths of the Abyss: Exposing Rootkits - Track 2, Session 4
Dive deep into rootkits: explore their inner workings, detection techniques, and countermeasures. Learn to identify and neutralize these stealthy threats using advanced tools like Living Off The Land Drivers.
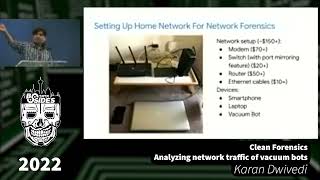
Clean Forensics: Analyzing Network Traffic of Vacuum Bots - Lecture
Explore network forensics of vacuum bots, uncovering security and privacy concerns. Learn step-by-step analysis of bot communication, authentication protocols, and potential vulnerabilities in smart home devices.
Introduction to Risk Analysis and Management in Security - Lecture 7
Comprehensive overview of risk analysis, management, and security incident taxonomy in cybersecurity, covering eavesdropping, denial of service, and cloud computing concepts.
Introduction to Risk Analysis in Security and Network Forensics - Chapter 7
Explore risk analysis, management methodologies, and security incident taxonomy. Learn about various cyber threats and attack types, as well as cloud computing concepts and services.
The Fog of War - How Do You Know What to Believe
Experts discuss the challenges of propaganda and disinformation in modern warfare, focusing on the Russia-Ukraine conflict and exploring tactics to discern truth amidst the fog of war.
The Beautiful Mind of a Timeline - Data Exploration and Analysis in Digital Forensics
Explore data science techniques for anomaly detection and noise reduction in digital forensics using Timesketch, with insights from Google security experts.
Photoshop Fantasies - Putting Altered and Synthetic Imagery on the Internet into Context
Explore the impact of altered and synthetic imagery on the internet, understanding its context and implications for digital media consumption and creation.

The Future of Fingerprint Analysis - Historical Tools to Digital Comparison Software
Explore the evolution of fingerprint analysis, from historical tools to modern digital techniques. Learn about specialized software and comparison methods for effective criminal investigations.

Emerging Trends and Challenges in Questioned Document Examination
Explore advancements and challenges in questioned document analysis, including new methods, their implications for forensic experts, and the balance between innovation and practicality in the field.

Modern Developments and Current Trends in Questioned Documents Examination
Explore modern trends in questioned document examination, including digital analysis, advanced microscopy, and AI applications for enhanced forensic investigation and document authentication.
Crime Investigation Platform of the Future
Explore the future of crime investigation with advanced technology, ethical considerations, and collaborative approaches for more efficient and accurate law enforcement processes.
Forensic Analysis of Container Checkpoints
Explore forensic container checkpointing in Kubernetes, learning tools and methods to analyze checkpoints and extract crucial information for uncovering potential malicious activity.