System for Deepfake Detection - DeepAudioDetector - Ekoparty 2021
Explora técnicas avanzadas de detección de deepfakes de audio utilizando inteligencia artificial, con énfasis en metodologías, experimentos y herramientas de libre uso para enfrentar amenazas cibernéticas emergentes.
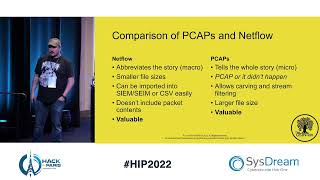
NetflOSINT- Taking an Often-Overlooked Data Source and Operationalizing It - Joe Gray - Hack in Paris
Explore NetflOSINT: Leveraging overlooked Netflow data for efficient network forensics. Learn extraction techniques, analysis methods, and tools to enhance threat hunting and intelligence gathering.
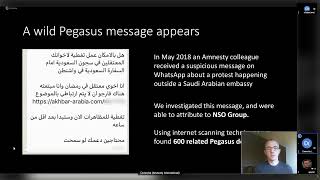
Catching NSO Group's Pegasus Spyware
Explore Amnesty International's innovative forensic techniques for detecting NSO Group's Pegasus spyware, including the open-source Mobile Verification Toolkit (MVT) for identifying sophisticated mobile threats.
Internet of Compromised Things: Methodology & Tools - Damien Cauquil - Hack in Paris - 2017
Explore methodologies and tools for investigating connected devices in criminal cases, addressing challenges and introducing new resources for digital forensics.
Into the Dark - Globalized Crime
Explore global illicit financial activities and strategies to combat them through partnerships, digital forensics, and legal measures. Experts discuss international cooperation and public awareness.
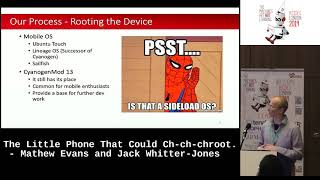
The Little Phone That Could Ch-ch-chroot
Explore cost-effective Red Team tactics using a covert disposable phone for reconnaissance, including device rooting, functionality, and anti-forensics techniques.
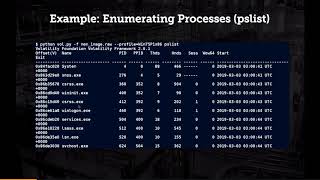
Investigating Malware Using Memory Forensics - A Practical Approach
Practical approach to memory forensics for malware detection and investigation, covering techniques, demonstrations, and analysis of various malware types and rootkits.
Hiding Process Memory via Anti-Forensic Techniques
Explore novel anti-forensic techniques for hiding malicious process memory, evading detection by memory analysis tools while maintaining accessibility for malware functionality.
Extract Data from Damaged Android Mobile Device - Version 7.X.X
Comprehensive workshop on extracting data from damaged Android devices, covering soldering, retrieval of device information, and extraction of various data types for forensic analysis.
Advanced Smartphone Forensics
Explore advanced smartphone forensics techniques for iOS, Windows Phone, and BlackBerry, focusing on cloud backups, data encryption, and device tracking protocols.
Getting Saucy with APFS - The State of Apple's New File System
Explore Apple's APFS file system, covering acquisition techniques, tools, and key features like clones and snapshots. Gain insights into forensic analysis and system management.
Hunting for Memory Resident Malware
Explore techniques for detecting memory-resident malware, including API analysis, post-breach detection, and CLR hooking. Learn why memory hunting is crucial in cybersecurity.
Hack for Show, Report for Dough - Brian King
Learn effective techniques for crafting compelling penetration testing reports that resonate with both technical and non-technical audiences, enhancing communication and impact.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
Skynet Will Use PsExec When SysInternals Go Bad
Explore how attackers leverage Sysinternals tools for reconnaissance, execution, persistence, and anti-forensics in cybersecurity incidents. Learn detection techniques for enhanced defense.
Windows Operating System Archaeology - Casey Smith and Matt Nelson
Explore Windows OS archaeology, focusing on Component Object Model, persistence techniques, and evasion methods for enhanced system understanding and security awareness.
A Sherlock Holmes Mystery - AI-Powered Behavioral Forensics
Explore AI-powered behavioral forensics for cybercrime investigation, profiling hackers through their digital traces and connecting seemingly unrelated attacks using advanced analysis techniques.
Deep Fakes Are Getting Terrifyingly Real - How Can We Spot Them?
Explore deepfake technology, its creation process, and detection strategies. Learn to identify AI-generated content and understand the importance of explainability in combating this emerging threat.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.
What I Know About Your Company OSINT and Hacking LinkedIn Business Processes
Discover advanced OSINT techniques for LinkedIn, including reconnaissance, scripting, and exploiting vulnerabilities. Learn to gather valuable business intelligence ethically and securely.
Stealthier Attacks and Smarter Defending With TLS Fingerprinting
Explore TLS fingerprinting for enhanced attack stealth and improved defense strategies. Learn techniques for anomaly detection, anti-forensics, and fingerprint-based routing in network security.