CSI Forensics - Unraveling Kubernetes Crime Scenes
Explore advanced DFIR techniques for container environments, focusing on Kubernetes. Learn to checkpoint compromised apps, conduct memory forensics, and understand the latest DFIR capabilities for effective incident response.
Deep Dive in the Dark Web OSINT Style
Explore OSINT techniques for investigating the Dark Web, including market analysis, social network mapping, and tools for uncovering hidden content and connections.
From Dead Data to Digestion - Extracting Windows Fibers for Your Digital Forensics Diet
Explore Windows Fibers' undocumented internals, reverse APIs, and create detection telemetry from process memory. Learn about a new open-source tool for threat hunting and EDR development.
Practical Osint
Explore practical Open Source Intelligence techniques for gathering and analyzing publicly available information, enhancing your cybersecurity and investigative skills.
The Truth, You Thought We Wouldn’t Know? - Wolf Flight
Uncover hidden truths and explore the depths of information security in this intriguing talk that challenges conventional wisdom and reveals surprising insights.
USB Write Blocking with USBProxy
Explore USB write blocking techniques using USBProxy, enhancing digital forensics and security practices for USB device interactions.
De-Serial Killers
Explore the intricacies of serialization vulnerabilities in software and learn effective techniques for identifying and mitigating these security risks.
Tomb Raider - Automating Data Recovery and Digital Forensics
Explore automated data recovery and digital forensics techniques, enhancing efficiency in retrieving crucial information from digital sources for investigations and analysis.
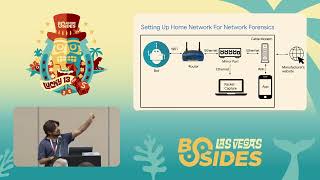
Clean Forensics - Analyzing Network Traffic of Vacuum Bots
Explore network traffic analysis of vacuum bots, uncovering potential security vulnerabilities and data privacy concerns in smart home devices.
Cold Case Cyber Investigations - Catfishing Cooper and Other Ops
Explore cold case cyber investigations, including the intriguing "Catfishing Cooper" operation, with insights from expert Jim Christy's keynote address on digital forensics and cybercrime solving.
See You Later, Allocator! - Updating Volatility's Analysis of Modern Linux Memory Allocators
Explore modern Linux memory allocators and their impact on Volatility's analysis techniques. Learn about recent developments and improvements in memory forensics for Linux systems.
A Tale of Two Malware Families - Overcoming Anti-Forensics and Foiling Botnets in the Cloud
Explore techniques to overcome anti-forensics and disrupt cloud-based botnets, focusing on two malware families. Gain insights into advanced cybersecurity strategies and threat mitigation.
Revisiting the Analog Hole - Using OCR and Other Techniques to Exfiltrate Data
Explore innovative data exfiltration techniques using OCR and analog methods, enhancing your understanding of cybersecurity vulnerabilities and potential countermeasures.
Forensicating Endpoint Artifacts in the World of Cloud Storage Services
Explore key forensic artifacts in cloud storage services like OneDrive and Dropbox, focusing on data exfiltration detection and acquisition techniques for endpoint investigations.
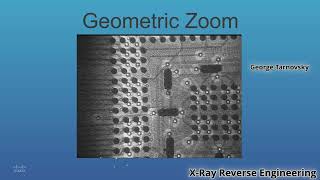
X Ray Reverse Engineering
Explore advanced X-ray reverse engineering techniques with expert George Tarnovsky, uncovering hidden hardware secrets and enhancing your security analysis skills.
GPG Memory Forensics
Techniques for retrieving passphrases and encryption keys from memory dumps of GPG processes, including Volatility3 plugins for key material extraction and potential defensive applications against ransomware.
Andromeda - GUI Based Dynamic Instrumentation Toolkit Powered by Frida
Explore Andromeda, a GUI-based toolkit for dynamic app analysis. Learn about class enumeration, method hooking, and runtime memory analysis features that enhance mobile security research and penetration testing.
Every Breath You Take - A CTI Review of Stalkerware
Explore stalkerware as an emerging enterprise threat, its poor detection, and potential for data breaches. Learn reverse engineering of Android APKs and OSINT techniques for stalkerware hunting.
Forense Digital a Sistemas Windows
Exploración detallada de técnicas forenses digitales en sistemas Windows, incluyendo recuperación de datos, rastreo de actividades y análisis de artefactos del sistema operativo.
La importancia del triage en la seguridad informática
Exploración del triage en seguridad informática: proceso vital para evaluar sistemas y tomar decisiones efectivas ante incidentes digitales. Enfoque en la normalización y mejores prácticas.
Fake You! Stopping the Spread of Fake News
Aprende estrategias para identificar y combatir la desinformación en línea con un experto en investigación digital y análisis forense.