
Secure CI/CD Using JSON Web Token (JWT)
Explore how GitLab leverages JWT for secure access to secret management solutions, enhancing DevSecOps practices and addressing challenges in retrieving sensitive data across cloud providers.
Know Your Dependencies - A Guide to Automating Dependency Assurance
Explore automated dependency assurance mechanisms for enhanced visibility into software components, addressing vulnerabilities and license obligations while maintaining development velocity.
SLSA with Cosign and Kyverno - Securing Software Delivery in Cloud Native Environments
Explore SLSA, Cosign, and Kyverno for enhancing software delivery security in cloud-native environments. Learn practical techniques to safeguard your development pipeline.
Shifting Security Left - Simplifying Security for Kubernetes and OpenShift Environments
Learn to simplify security in Kubernetes and OpenShift, focusing on authentication, secrets management, and bridging the gap between security and DevOps for more efficient cloud-native environments.
Application Security for Better Business Value - Expert Insights
Experts discuss how application security practices in cloud-native environments can reduce risks, enhance compliance, and drive innovation, leading to improved business value.
Security as Code - A DevSecOps Approach
Explore DevSecOps and Security as Code with CodeQL. Learn to implement security checks, detect vulnerabilities, and foster collaboration between development and security teams for a robust security culture.
Software Supply Chain Security with TAG Security
Explore software supply chain security with insights on guidance, resources, and recent developments. Learn about the whitepaper, compromise catalog, and reference architecture for secure supply chains.
Securing Diverse Supply Chains Across Interconnected Systems
Explore how SpaceX integrates SBOM and vulnerability discovery tools to enhance security across diverse software systems, reducing response time and improving prioritization for developers.
Security Threat Modeling Live from Scratch Session
Hands-on workshop demonstrating lightweight threat modeling for CNCF projects, led by Andrew Martin. Learn practical techniques to identify and mitigate security risks in cloud-native environments.
Security That Enables - Breaking Down Security Silos in the DevOps Ecosystem
Explore strategies to integrate security seamlessly into DevOps, addressing challenges in CI/CD workflows and learning from real-world breaches to enable confident, secure deployments.
How to Secure Your Supply Chain at Scale
Learn how Yahoo secures its software supply chain using open-source tools like Grafeas, Sigstore, and Kyverno. Discover strategies for source code scanning, vulnerability management, and protecting Kubernetes deployments at scale.
How do Mature DevOps Teams Manage Software Security?
Explore strategies for managing software security in mature DevOps environments, focusing on best practices and innovative approaches for integrating security into the development lifecycle.
Fun with Continuous Compliance
Explore continuous compliance strategies, including OSCAL for automated assessments and OSS tools like Falco and Voucher for scalable implementation, to streamline and modernize your DevSecOps compliance approach.
Secure Kubernetes Supply Chain: Lessons and Tools for Project Releases
Explore Kubernetes' enhanced security features for software supply chain, including SBOMs, provenance attestations, and digital signatures. Learn to implement these tools in your projects.
Secure Your Software Supply Chain Using Observability
Explore techniques for enhancing software supply chain security through observability, focusing on key benefits and practical implementation strategies.
First Steps to Full Lifecycle Security with Open Source Tools
Hands-on workshop demonstrating installation, configuration, and customization of open-source security tools for DevOps, focusing on Trivy for container and infrastructure security and Starboard for continuous security assurance.
Cloud Native - Protecting Software Supply Chains Using Kyverno
Explore Kyverno's role in safeguarding software supply chains, enhancing security practices, and ensuring compliance in cloud-native environments.
Using CNCF Best Practices to Enhance Software Supply Chain Security
Enhance software supply chain security using CNCF best practices. Learn from 3M's journey to improve code security, respond to vulnerabilities, and implement standards-based SBOM.
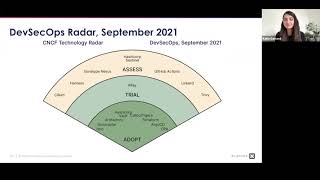
CNCF End User Technology Radar for DevSecOps - September 2021
Explore DevSecOps trends and recommendations from CNCF's End User Community. Gain insights on security solutions, micro-segmentation, and balancing security with developer experience in cloud-native environments.
Secure Containers and Workloads with Certificates in CI/CD Pipelines
Learn to enhance security in CI/CD pipelines by implementing certificate-based protection for containers and workloads, ensuring robust safeguards for cloud-native applications.
Digital Forensics with Container Checkpointing
Explore container checkpointing for digital forensics in cloud environments. Learn to capture and analyze forensic snapshots of running containers, enhancing security in ephemeral Kubernetes setups.