MLSecOps and Shift-Left Security in Machine Learning Model Lifecycle
Learn to integrate security into machine learning model lifecycles using MLSecOps. Explore shift-left security practices, address vulnerabilities early, and implement effective risk management in ML projects.
Design-Level Supply Chain Attacks in the Real World
Explore design-level supply chain attacks, including environmental constraints, compatibility issues, and malicious influence. Learn to identify and mitigate these often-overlooked vulnerabilities in cybersecurity.

Introduction to Inner-Loop Security - Shifting Left, but Better
Explore inner-loop security as the next evolution of "shift left," enabling developers to build secure-by-design products through improved methodologies and tools.
The DevSecOps Builder's Guide to the CI/CD Pipeline
Comprehensive guide to integrating security into DevOps practices, focusing on CI/CD pipeline implementation for enhanced software delivery and protection.
The Gift of Feedback - Enhancing Application Security
Discover how to implement next-generation security by leveraging feedback, pushing security left, and making it consumable. Learn strategies to engage developers and address the challenges of securing complex software workloads.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Changed Responsibilities in Modern Development Practices
Explore how modern development practices like CI/CD and DevOps impact application security. Learn strategies for integrating security early in the development lifecycle and empowering developers with essential security skills.
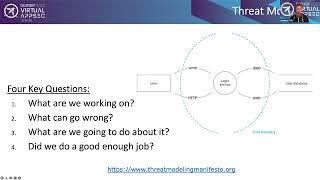
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
Shift-Left to Address OS Vulnerabilities and Compliance for Cloud Native Applications
Inject security early in software development to address vulnerabilities before production, focusing on OS vulnerabilities and compliance for cloud-native apps.
Understanding the Sec in DevSecOps: Beyond Just Shifting Left
Explore attack vectors, preventive measures, and compliance strategies in DevSecOps. Learn innovative approaches to enhance software security beyond shifting left.
The Ownership Battle Between Engineering and InfoSec
Explore the ownership dynamics between Engineering and InfoSec teams in DevSecOps, focusing on effective result consumption and action implementation.
Building Your First DevSecOps Pipeline
Demystify DevSecOps and build a functional pipeline with cutting-edge security testing, including SCA, SAST, and DAST tooling. Supercharge software security and achieve true "Shift Left" success.
Using Static Analysis to Catch Configuration Vulnerabilities
Learn to secure containers and IaC using static analysis. Discover how to identify misconfigurations, prevent vulnerabilities, and implement early detection in your development workflow for improved application security.
Cloud Native Application Security with Open Source
Explore cloud native app security risks, identification methods, and open-source tools for risk mitigation in developer-friendly environments. Learn to integrate security into workflows.
Securing Kubernetes Multi-Tenancy - Navigating Challenges Through DevSecOps
Explore security challenges in multi-tenant Kubernetes environments and learn strategies for enhancing control and visibility through DevSecOps practices, including namespace isolation, access controls, and incident response.
Making Security Simpler
Experts discuss simplifying security through built-in features, automation, and improved architectures, aiming to reduce resource needs and enhance protection for various organizations.
Machine Learning Security Operations at One of the World's Largest Brewing Companies
Explore MLSecOps in brewing industry, focusing on Heineken's approach to automating security in machine learning processes, data democratization, and secure ML workbenches.
How to Shift-Left and Find Critical Authorization Vulnerabilities Throughout Your CI/CD Pipeline
Discover effective strategies for detecting and preventing authorization vulnerabilities in DevSecOps pipelines, focusing on early identification and remediation across multiple application roles and APIs.