Securing Your Open Source Supply Chain
Explore software supply chain security threats and learn from SUSE's journey to secure open source codebases. Gain insights on certifications, processes, and tools for enhancing supply chain protection.
Shifting Application Security Left: Practical Steps to Get There
Explore practical steps to integrate automated security testing into software delivery pipelines, enabling efficient and secure development practices for modern engineering teams.
A Different Kind of S3 - First Line Security of the Supply Chain
Explore three core areas for securing the software supply chain: Software Bill of Materials (SBOM), Signing, and Slimming. Learn practical methods to enhance first-line security controls and minimize attack surfaces.
Dependencies: Do's and Don'ts - Managing Application Dependencies Securely
Learn best practices for managing dependencies in software development, balancing security risks with benefits to team velocity and business value. Discover preventive measures to minimize vulnerabilities.
Securing Open Source Software - End-to-End, at Massive Scale, Together
Explore strategies for securing open source software at scale, focusing on collaborative approaches and end-to-end solutions for robust protection in the digital ecosystem.
A Different Kind of S3 - First Line Security of the Supply Chain
Explore innovative approaches to supply chain security, focusing on first-line defense strategies and cutting-edge solutions for robust protection against emerging threats.
5 Open Source Security Tools All Developers Should Know About
Discover five essential open-source security tools for developers, enhancing code safety and vulnerability detection in your projects.
Curating and Securing Open Source for GovCloud
Explore automated workflows for curating and securing open-source libraries in air-gapped environments, enhancing developer experience while maintaining strong controls over third-party packages.
Securing Your Software Supply Chain
Explore the current state and future of JavaScript ecosystem security, learn about emerging tools to combat threats, and discover practical strategies to protect your software supply chain.
Ketchup, Mustard, and Relish of Software Supply Chain Security - Panel Discussion
Explore open source standards and tools for enhancing software supply chain security with industry experts. Learn about S2C2F, SLSA, and FRSCA, their benefits, and how to implement them effectively.
Securing the Software Supply Chain: From Threats to Best Practices
Comprehensive overview of software supply chain security, covering history, threats, initiatives, challenges, and best practices. Experts discuss key issues and solutions for organizations.
Supply Chain Security: From Infrastructure to Application, Code to Cloud
Explore best practices for securing the entire software supply chain, from infrastructure to application, covering code, cloud, dependencies, and deployment.
Security as Code: A DevSecOps Approach
Explore DevSecOps and Security as Code principles, focusing on SQL injection prevention and vulnerability analysis using Code2LV and data flow techniques.
Securing Your Open Source Supply Chain
Explore strategies for securing the open source supply chain, focusing on best practices and tools to mitigate risks in software development and deployment.
Road to SLSA3 - Non-falsifiable Provenance in Tekton with SPIFFE/SPIRE
Explore non-falsifiable provenance in Tekton using SPIFFE/SPIRE, enhancing software supply chain security and achieving SLSA3 compliance.
HashiCorp's Multicloud Zero Trust Platform
Explore HashiCorp's innovative platform for implementing zero trust security across multicloud environments, enhancing data protection and access control.
Fight Back Against Cyber Risk in the Software Supply Chain - Secure DevSecOps Pipeline for Regulated Environments
Secure DevSecOps pipelines for regulated environments: best practices, open-source tools, and real-world application in banking using BIAN framework and technologies like Tekton, Terraform, and SonarQube.
DevSecOps Best Practices in Cloud Native Computing - CMCC Case Study
探索中国移动通信公司的DevSecOps最佳实践,了解如何将安全无缝集成到云原生开发和运维流程中,提高效率和安全性。
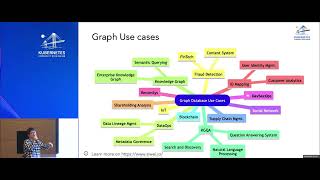
Graph Driven DevSecOps in Practice
Explore graph-driven DevSecOps implementation strategies, enhancing security integration in cloud-native development pipelines for improved efficiency and risk mitigation.
Critical DevSecOps Considerations for Multi-Cloud Kubernetes
Explore DevSecOps for multi-cloud Kubernetes: containerization, infrastructure, observability, and system-wide security best practices. Gain insights from cloud-native experts on optimizing and securing Kubernetes environments.
Path to Production: Sustainable Compliance in Strict Environments
Discover strategies for achieving sustainable compliance in highly regulated environments, focusing on DoD practices using Big Bang, Iron Bank, and Kyverno for faster, secure-by-default Kubernetes deployments.