Deep Dive into Falco - Empowering DevSecOps with Real-time Container Security
Explore Falco's Kubernetes-native runtime security features, detect threats in real-time, and enhance container security posture through behavior-based rules and customized alerts.
GitHub-Azure Authentication and SLSA in DevOps
Explore GitHub Actions authentication for Azure and SLSA principles in DevSecOps. Learn passwordless methods, security levels, and contribute to open-source supply chain security projects.
Strategies for Patching Critical CVEs in Open Source Software - Best Practices and Tools
Master strategies for handling critical CVEs in open source packages, from patching container images with Copacetic to building projects from scratch, while learning best practices for software supply chain security.
Watching the Watchers - The Hidden Risks of Container Scanning Tools
Explore critical security risks and mitigation strategies for container vulnerability scanning tools, focusing on system protection, secure configurations, and defense-in-depth approaches.
Scanning Infrastructure as Code for Security Vulnerabilities with Terraform
Master infrastructure security scanning with Checkov OSS, focusing on Terraform vulnerabilities and exploring policy-as-code solutions like Bridgecrew and Hashicorp Sentinel for enhanced cloud security.
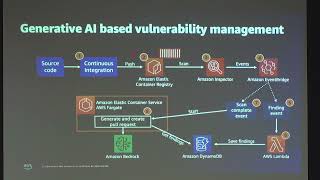
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
How to Shift-Left and Find Critical Authorization Vulnerabilities Throughout Your CI/CD Pipeline
Discover effective strategies for detecting and preventing authorization vulnerabilities in DevSecOps pipelines, focusing on early identification and remediation across multiple application roles and APIs.
Secure by Design CI/CD: Practical Insights for Pipeline Security
Discover practical strategies for securing CI/CD pipelines through real-world insights from Adobe and Autodesk, featuring reference architectures, security controls, and implementation of CNOE stacks for cloud-native excellence.
Rapidly Scaling Actionable Insights at the Point of Interaction
Discover how to leverage open source projects from Intel and IBM to build commercial solutions that deliver AI at the Edge, enabling rapid scaling of actionable insights at interaction points.
Securing AI Systems and Protecting the Software Supply Chain
Explore key AI security challenges in software development, focusing on OWASP Top 10 for LLMs, supply chain vulnerabilities, and practical mitigation strategies for CI/CD pipelines.
5 Steps to Operationalize and Mature Your Cloud Security Program
Discover proven strategies to strengthen cloud security operations, from democratizing security to consolidating tools and managing risks across DevOps, SOC, and AI teams.
Secure Your Systems Using Policy-as-Code
Discover how policy-as-code bridges the gap between development and security teams, improving developer experience while maintaining robust system security. Learn implementation best practices and overcome common challenges.
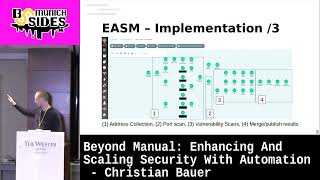
Beyond Manual: Enhancing and Scaling Security with Automation
Discover how to scale security operations through automation, focusing on practical strategies and tools to enhance your organization's security posture efficiently.
A Security Champion's Journey - Making Things A Bit More Secure Than Yesterday Every Day
Discover practical strategies for incrementally improving security in your organization through the lens of a security champion's daily experiences and lessons learned.
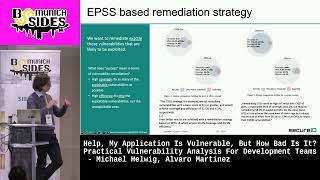
Practical Vulnerability Analysis for Development Teams
Discover effective vulnerability analysis techniques and best practices for development teams, focusing on identifying and mitigating security risks in software development.
Secure Development in Open Source - The Road to SLSA Level 3 Compliance for Eclipse Temurin
Discover how Eclipse Temurin achieves SLSA Level 3 compliance through secure development practices, cloud-based Jenkins implementations, and open-source distribution methods across multiple platforms.
Cloud Native's Next Decade: Stable, Secure, and Ready for Disruption - The Future of Cloud Security
Explore the future landscape of cloud native security, examining emerging challenges like AI system protection while understanding why current stability might precede a new wave of innovation.
Secure Release Processes with in-Toto Policy Verification
Discover how to enforce secure software release processes using in-toto's policy verification system, covering attestations, SDLC compliance, and build provenance for enhanced security measures.
Practical Supply Chain Security: Implementing SLSA Compliance from Build to Runtime
Discover practical strategies for implementing SLSA compliance, from using GitHub Actions and Cosign for artifact signing to enforcing runtime policies with Kyverno and securing keys with HSMs.
Securing with Love: A Philly Style Approach to Cloud Safety
Discover how security and development teams can collaborate effectively on cloud applications, focusing on practical steps like threat modeling, risk assessment, and maintaining robust security practices.
Application Security in the Age of AI - Understanding Modern SSDLC and AI-Enhanced Security
Explore modern application security practices enhanced by AI, covering SSDLC implementation, threat modeling, secure coding, and runtime security for comprehensive software protection.