
AWS AI Services Transforming DevSecOps - Amazon Q Insights
Explore how AWS AI services like CodeGuru, Amazon Q, and GuardDuty revolutionize DevSecOps, enhancing code quality, extracting insights, and bolstering security in AWS environments.
Attacking and Defending Kubernetes Clusters with KubeHound Attack Graph Model
Explore Kubernetes cluster security using KubeHound attack graph model. Learn offensive and defensive strategies to enhance your IT infrastructure protection.
Introducing the Databricks AI Security Framework (DASF) to Manage AI Security Risks
Explore robust AI security guidelines for secure ML and AI application deployment. Learn about the Databricks AI Security Framework and gain tools to test Databricks deployments for AI security.
Shift Down Security - How Platform Teams Can Help Break the Logjam
Explore how platform engineering and cloud native practices can automate security using policy as code, enabling developers and security teams to focus on their core competencies.
Below the Radar: Identifying Hidden Threats Within the Development Ecosystem
Explore critical threats in cloud-native environments, focusing on hidden exposed secrets in code. Learn about vulnerabilities in source code management, Kubernetes secrets, and Shadow IT, with mitigation strategies and tools.
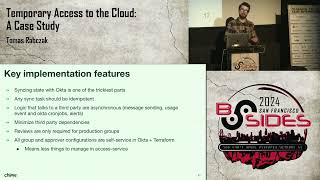
Temporary Access to the Cloud - A Case Study
Explore Chime's innovative temporary access solution for Okta, balancing product development with cultural shifts in security practices. Learn from this real-world case study.
Threat Modeling for Developers
Expert panel discussion on threat modeling techniques, best practices, and resources for developers to enhance application security and design safer systems.
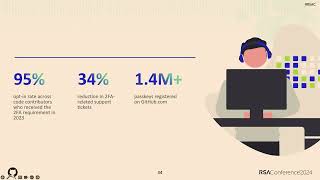
AI and the Software Supply Chain - Evolving Security Strategies
Explore how AI and other methods enhance software supply chain security, addressing advanced attacks and evolving developer toolkits for improved protection.
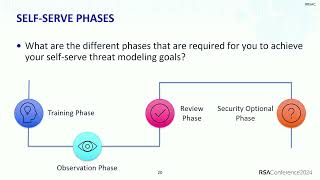
Redefining Threat Modeling - Scaling Security Without Bottlenecks
Innovative approach to scaling threat modeling by empowering development teams, reducing bottlenecks, and integrating security seamlessly into software development processes.
OSS Supply Chain Threats and Why You Need a Holistic Security Strategy
Analyze 13 real-world threats to open source components and learn how to mitigate risks using the OpenSSF's Secure Supply Chain Consumption Framework for a holistic security strategy.
A Step Closer to Secure Development: Using in-Toto and OPA Gatekeeper to Verify Artifact Integrity
Explore securing software supply chains using in-toto, Witness, Archivista, and OPA Gatekeeper. Learn to verify artifact integrity from development to Kubernetes deployment.
Securing Your Supply Chain with an Open Source Ecosystem
Explore open-source tools and best practices for securing software supply chains across creation, build, deployment, and runtime stages. Learn to leverage automation and DevSecOps to reduce vulnerabilities.
Developing Secure Software with GitHub - Automated Security Checks and Tools
Learn to leverage GitHub for automated security checks, including static application security testing and software composition analysis, to enhance your application's security posture with minimal effort.
So Long Secure Coding - Hello Secure Development
Explore secure development beyond code, covering design, architecture, threat modeling, ecosystems, testing, and deployment for comprehensive system protection.
Small Language Models for Application Security - Beyond ChatGPT
Explore how small, open-source language models like LLaMa and Alpaca can revolutionize application security workflows, enabling earlier and more efficient security integration in software development.
DevSecOps Tutorial - Building a Pipeline with GitHub Actions and Docker Scout
Learn to implement DevSecOps practices using GitHub Actions and Docker Scout. Covers SAST scanning, container image scanning, and integrating security into the development pipeline.
AI Hallucinations and Manipulation - How to Use AI Coding Tools Securely - DevSecCon
Explore AI coding tools' security implications, challenging their ability to produce secure software and learning strategies for safe implementation in development workflows.
Visibility and Protection in Infrastructure as Code and Web Applications - DevOps Security with FortiGate CNF, FortiWeb and FortiDevSec
Master application security practices through FortiGate CNF, FortiWeb, and FortiDevSec integration with DevOps, covering IaC protection, source code security, and attack surface minimization in the development lifecycle.
TTPs of Attacks on OSS in Python - Trusty Package Security
Explore tactics and techniques of supply-chain attacks on Python open-source software, including starjacking, installation, delivery, and exfiltration. Learn defensive strategies against these threats.
5 Biggest Platform Manager Mistakes - Building and Managing Internal Developer Platforms
Discover common pitfalls in Platform Management and learn strategies to build effective Internal Developer Platforms beyond technical aspects. Gain insights on business analysis, stakeholder engagement, and holistic approaches.
GitOps and GitHub Events in DevSecOps Release Orchestration Pipeline
Implement DevOps processes to ensure controlled software releases comply with standards. Learn how to define control levels, establish best practices, and disseminate culture across the organization.