A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
Lost in Translation - Communicating Outside of Security
Bridging the communication gap between security professionals and developers for successful DevSecOps adoption, with insights on common language and mutual understanding.
DevSecOps Without DevOps Is Just Security
Explore effective DevSecOps practices, emphasizing collaboration between security and DevOps teams. Learn prerequisites, case studies, and strategies for leveraging existing resources to enhance security integration.
SCORE Bot - Shift Left, at Scale!
Automated security code review tool for early detection of organization-specific vulnerabilities, integrated with GitHub PR process. Provides real-time feedback and actionable guidance for developers.
DevSecOps with OWASP DevSlop
Learn DevSecOps through hands-on examples with OWASP DevSlop. Explore secure component management, secret handling, testing techniques, and open-source tools to enhance your pipeline security.
Temporal - AppSec Timeline - Wins, Failures, Promises, and Predictions
Explore AppSec's 20-year journey: achievements, setbacks, and future prospects. Analyze trends, evaluate DevSecOps impact, and gain insights into the evolving landscape of application security.
OWASP Standard Classification - Rough Consensus - An OWASP Story
Explore OWASP's journey in establishing software security standards through rough consensus, highlighting challenges, achievements, and future directions in the field.
Topics of Interest - Top 10 Challenges for DevSecOps
Explore the top 10 challenges in implementing DevSecOps, focusing on integrating security into DevOps processes for precise, usable data and reduced business risk.
Cloud Security - A Guide For Developing A Comprehensive Multi-Cloud Security Strategy
Explore top trends, risks, and practical guidance for developing a comprehensive multi-cloud security strategy to protect IaaS, PaaS, and SaaS services.
As Strong as the Weakest Link - Securing the Software Supply Chain
Explore software supply chain security, recent high-profile attacks, and defense strategies. Learn about dependencies, vulnerabilities, and best practices for protecting your production systems.
How to Start with DevSecOps
Explore DevSecOps fundamentals, including security testing methods, runtime application security, and the Executive Order on Cyber Security in this informative Docker community talk.
Hacking into Your Containers, and How to Stop It
Explore container security vulnerabilities and learn proactive DevSecOps practices to protect your deployments. Live hack demonstration and practical steps for hardening clusters against attacks.
Hacked! Run Time Security for Containers
Explore container security challenges, runtime monitoring, policy enforcement, and forensics using system call signals. Learn to detect threats and implement robust security measures for containerized environments.
Making Security Simpler
Experts discuss simplifying security through built-in features, automation, and improved architectures, aiming to reduce resource needs and enhance protection for various organizations.

Three Things the Security Industry Isn't Talking About - but Should Be
Explore innovative approaches to cybersecurity beyond threat detection, focusing on reducing attack surfaces and empowering defenders with proactive strategies and application-aware solutions.
Protecting the Cloud with the Power of Cloud
Explore DevSecOps principles and self-healing cloud architectures. Learn to identify and auto-remediate security misconfigurations in real-time, enabling scalable and secure multi-cloud environments.
Integrating Our DevSecOps Product Pipeline with Software Security Standards
Explore strategies for integrating security standards into DevOps pipelines, leveraging automation, and aligning innovation with compliance for efficient product development.
In Search of Security Shangri-La
Exploring the evolution of cybersecurity practices, challenges in integrating security into tech processes, and strategies for achieving a more collaborative and effective security approach in modern organizations.
Beyond Firefighter vs. Safety Matches - Growing the DevSecOps Pipeline
Explore strategies for balancing specialization and generalization in DevSecOps talent development, addressing challenges in modern systems development, operations, and security.
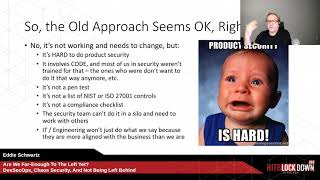
DevSecOps, Chaos Security, and Not Being Left Behind
Exploring DevSecOps and Chaos Security Engineering to integrate business, development, and security teams for effective product security and staying ahead of adversaries.
Security Learns to Sprint - DevSecOps
Explore strategies for integrating security into DevOps, focusing on the "Three Ways" and providing actionable steps for immediate implementation in your organization.