OWASP AppSec Europe 2014 - Builder and Breaker Track Sessions
Explore cutting-edge web security topics including DevOps, JavaScript vulnerabilities, XSS detection, Windows Store app testing, developer training effectiveness, and automated authorization checks.
AppSec at DevOps Speed and Portfolio Scale
Explore a revolutionary approach to application security using passive sensors for real-time vulnerability detection, enhanced architecture, and proactive collaboration across entire IT portfolios.
Stop Chasing Vulnerabilities - Introducing Continuous Application Security
Explore continuous application security strategies using open-source tools for real-time monitoring and analytics, shifting focus from individual vulnerabilities to comprehensive portfolio-wide assurance.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
AppSec is Eating Security - The Future of Information Security
Explore the future of application security with insights on containerization, hardware security, and user-centric approaches. Learn about emerging trends and strategies for building safer digital ecosystems.
Application Security at DevOps Speed and Portfolio Scale
Explore a revolutionary approach to application security using passive sensors for real-time visibility across an organization's portfolio, enabling proactive collaboration and value generation.
Anuket Launch Event - Standardizing Network Function Infrastructure
Explore Anuket, a new LF Networking project merging OPNFV and CNTT, delivering standardized infrastructure specifications for virtualized and containerized network functions to accelerate telecom digital transformation.
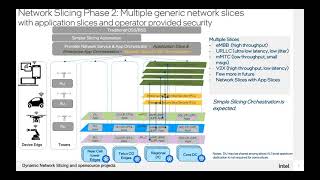
5G Dynamic Network Slicing via Open Source Projects
Explore 5G dynamic network slicing, its business opportunities, and deployment models. Learn about orchestration, automation, and open-source projects contributing to this innovative technology.
Auto Generate SBOMs for Open Source Projects in Any Language and Platform
Learn to automatically generate Software Bill of Materials (SBOMs) for open source projects, enhancing security and compliance across languages and platforms.
Software Supply Chain Integrity with Sigstore
Learn about Sigstore, a tool for securing software supply chains, with demos on Cosign for signing and verifying artifacts, and insights on its practical applications.
Generating a SPDX SBOM for Your Code in CI Using ORT
Learn to generate SPDX Software Bill of Materials (SBOM) for your code in continuous integration using the OSS Review Toolkit (ORT), enhancing software transparency and security.
Attesting Practically: Exploring the Glue Behind Secure Runtime Environments
Explore practical applications of attestations in software supply chain security, focusing on Cosign, in-toto, and VEX to create secure, auditable runtime environments and effectively manage security threats.
Gitsign - Keyless Git Commit Signing
Explore Gitsign, a Sigstore project enabling keyless Git commit signing. Learn its functionality, integration with Sigstore, and application in development, CI/CD, and GitOps workflows.
Board Farms for Everyone - Making Hardware Debugging Easier and Sharing Boards Across the Globe
Discover how to create a board farm for remote hardware debugging, simplifying development and enabling global collaboration. Learn practical tips for setup, integration, and efficient device management.
Securing CI/CD Pipelines Through Security Gates
Explore CI/CD pipeline security gates, frameworks, and best practices. Learn to embed security seamlessly in DevOps workflows and eliminate issues before production. Includes live demo.
Leveraging Next Generation Cellular Networks for Drone Telemetry and Payload Communication
Explore how 5G cellular networks can enhance drone telemetry and payload communication, addressing limitations in data rates, latency, and beyond visual line of sight operations for UAVs.
Zero-Configuration Runtime Software Component Detection
Discover how to detect vulnerable software components in running systems using eBPF, focusing on Java applications and container images without initial configuration.
Automated Testing and Board Farming for Embedded Linux
Explore practical aspects of running board farms for embedded Linux testing. Discuss control software, architectures, hardware tools, and collaboration opportunities in automated testing.
Using OpenEmbedded Inside Containers - How and Why
Explore generating container payloads with OpenEmbedded for embedded Linux devices, comparing benefits and challenges to traditional Docker approaches in image size, reproducibility, and license management.
Use Pi-Hole with Unbound DNS for Enhanced Privacy
Enhance online privacy by setting up Pi-hole with Unbound DNS to filter ads and prevent data tracking. Learn to install and configure these tools for improved web browsing security.
Shifting Application Security Left: Practical Steps to Get There
Explore practical steps to integrate automated security testing into software delivery pipelines, enabling efficient and secure development practices for modern engineering teams.