Grey Science: Bridging Academic and Underground Cybersecurity Research
Exploring synergies between academic and non-academic cybersecurity research to foster collaboration and innovation in addressing critical security and privacy challenges.
Designing for Interpersonal Security - A New Threat Framework
Explores interpersonal threat modeling for consumer technology, addressing security concerns from cohabitants and shared devices. Challenges traditional assumptions to better protect individuals and at-risk populations.
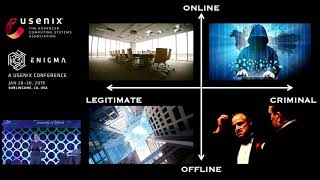
The Offline Dimension of Online Crime
Exploring the offline dimension of cybercrime, challenging the notion of anonymity and revealing local elements in criminal networks through extensive global fieldwork and interviews.
Why Even Experienced and Highly Intelligent Developers Introduce API Vulnerabilities
Explores why experienced developers introduce vulnerabilities through API misuse, examining cognitive factors and personality traits affecting code security detection abilities.
Modern Mind Control - Public Opinion Manipulation in Our Online World
Explores techniques for manipulating public opinion online, including fake news and social media campaigns. Examines historical precedents, current methods, and ways to identify and trace these influence operations.
Protecting Firefox Data with Content Signatures
Explore Firefox's content signature protocol, designed to protect data integrity against transport intermediaries and server compromises, ensuring secure updates for millions of users.
Backdooring of Real Time Automotive OS Devices
Explore vulnerabilities in automotive embedded devices, focusing on bare-metal software and real-time constraints. Learn about potential security risks and backdooring techniques in critical automotive systems.
Skeletons in the App Sandbox - 5+ Ways to Escape
Explore vulnerabilities in Apple's App Sandbox, uncovering methods to bypass security measures and escape containment, with insights on improving iOS and macOS protection.

Protecting Privacy with Math - Census Bureau Collaboration
Explore mathematical techniques for protecting privacy in data analysis, focusing on differential privacy and its applications in census data collection and statistical safeguards.
Exploiting Windows COM - WinRT Services
Discover techniques for exploiting Windows COM/WinRT services, uncovering vulnerabilities in cross-process communication and UWP applications for potential LPE, RCE, and sandbox escape attacks.
Internal Affairs - Hacking File System Access from the Web
Explore vulnerabilities in the File System Access API, revealing how malicious websites can exploit it for arbitrary code execution and bypass security measures.
Diving Into Spooler - Discovering LPE and RCE Vulnerabilities in Windows Printer
Uncover critical vulnerabilities in Windows Printer Spooler, exploring potential LPE and RCE exploits. Learn from past attacks and discover hidden security risks in this essential system component.
CCNP ENCOR - Dynamic Trunking Protocol - ENCOR 350-401 Complete Course
Learn Dynamic Trunking Protocol (DTP) for CCNP ENCOR, covering negotiation, frames, and interface commands. Gain practical knowledge through quizzes and hands-on examples.
The Future of Digital Communication and Privacy
Explore digital communication's future, encryption's role in privacy, and WhatsApp's efforts to balance security with combating misinformation in this insightful talk by Will Cathcart.
Hire the Hackers
Explore the world of cybercrime as Misha Glenny profiles convicted coders, revealing surprising insights about the individuals behind malicious code and challenging conventional cybersecurity approaches.
Chasing Foxes by the Numbers - Patterns of Life and Activity in Hacker Forums
Explore patterns of cyber criminal activity in underground forums, analyzing behavior across clear, deep, and dark web platforms to understand hacker communities and their focus areas.
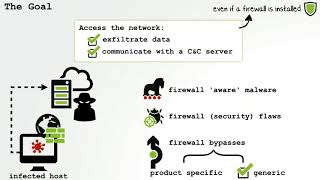
Fire & Ice - Making and Breaking macOS Firewalls
Explore macOS firewall creation and vulnerabilities, covering kernel-level socket filtering, user-mode communication, secure installation, and self-defense mechanisms. Learn about firewall bypasses and potential weaknesses.
PEIMA - Harnessing Power Laws to Detect Malicious Activities
Explore power law-based techniques for detecting and mitigating DDoS attacks, intrusions, and other malicious network activities using PEIMA methodology.
Insecurity in Building Automation - How to Create Dark Buildings with Light Speed
Explore vulnerabilities in building automation systems, their potential for exploitation, and the implications for physical security in modern infrastructure.
Offensive Malware Analysis - Dissecting OSX/FruitFly via a Custom C&C Server
Explore malware analysis techniques using a custom C&C server for OSX/FruitFly. Learn to decode, monitor, and understand malware behavior for enhanced cybersecurity skills.
Protecting Visual Assets - Digital Image Counter-Forensics
Explore counter-forensic techniques to safeguard image-based intelligence from exploitation attacks, addressing current and emerging threats in visual asset protection.