Security in the Context of Human Behaviors and Values by Elissa Redmiles
Explore security through human behavior, examining its intersection with machine learning and economics. Gain insights into valuable skills for understanding and improving digital safety.
Computer Security and the Internet of Things - Risks and Challenges
Exploring security risks in IoT devices, from cars to toys, and discussing challenges and new directions for enhancing digital and physical security in everyday technology.
From Concept to Deployment - The Life and Death of Security Features
Explore the journey of security features from concept to deployment, examining successful implementations and abandoned ideas in the tech industry, with insights from BlackBerry's research.
A Million Hit Points and Infinite Charisma - How Games Can Fix Computer Security Education
Exploring how cybersecurity games can address the skills gap by making security education more engaging, creative, and socially relevant. Discusses the potential and limitations of game-based learning in computer security.
Medical Device Security and Cybersecurity Risks - Enigma 2016
Exploring cybersecurity risks in medical devices, this talk covers regulatory issues, international standards, and the balance between innovation and patient safety in software-dependent healthcare technology.
Social Media Self-Defense - A Guide to Stopping Stalkers
Practical strategies for protecting privacy and safety on social media, including threat modeling, disinformation, and maintaining separate online identities for personal and professional use.
The Golden Age of Bulk Surveillance
Explore bulk surveillance concepts, their effectiveness, implementation, and key industry players. Learn about potential threats and the importance of secure communication in the digital age.
Stranger Things: Privacy and Security Implications of Always-On Devices
Exploring privacy and security implications of always-on AI devices in homes and workplaces, focusing on consumer education and design choices for wide adoption and enhanced security.
Social Cybersecurity - Reshaping Security Through Human Social Behavior
Exploring how social influences impact cybersecurity behaviors and designing systems that leverage social dynamics to encourage better security practices among users.
Least Privilege: Security Gain without Developer Pain
Automated approach to implement least privilege security without impacting developer productivity. Combines data gathering and policy adjustment to remove unused permissions across applications.
Combining the Power of Builders and Breakers in Cybersecurity - USENIX Enigma 2018
Exploring the evolving relationship between companies and security researchers in bug bounty programs, examining challenges, benefits, and future implications for cybersecurity.
Security Technology Adoption: Challenges Beyond Hardware Development
Exploring challenges in hardware security adoption, this talk examines market barriers and proposes solutions for integrating advanced security features into connected devices and systems.
Moving Fast and Breaking Things - Security Misconfigurations in Practice
Exploring system operators' perspectives on security misconfigurations, analyzing root causes, and providing practical recommendations to reduce their frequency and impact in organizations.
Building Identity for a Zero Trust Network
Exploring Netflix's zero trust network architecture, focusing on identity-based security, adaptive authentication, and device health to create a cloud-first, open perimeter environment.
Privacy Engineering: Not Just for Privacy Engineers
Explore Uber's collaborative approach to privacy engineering, blending data analysis with robust privacy measures to enhance services while ensuring regulatory compliance and user protection.
Countering Adversarial Cyber Campaigns - Alternative Strategies to Cyber War
Explores cyber campaigns as strategic alternatives to war, analyzing their impact on power politics and proposing new measures beyond conventional approaches to address current cyber policy challenges.
Learning from the Dark Web Dimension of Data - Valuing Stolen Data
Exploring the dark web's data economy to understand the true value of compromised information and develop better cybersecurity strategies for businesses and individuals.
If Red Teaming Is Easy - You're Doing It Wrong
Explore the challenges and complexities of effective Red Teaming in cybersecurity, going beyond simple penetration testing to improve organizational defenses through a comprehensive adversarial perspective.
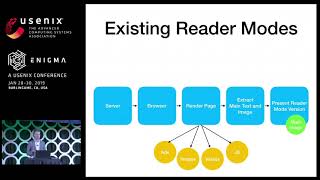
Next Steps for Browser Privacy: Pursuing Protections Beyond Extensions
Exploring privacy improvements beyond browser extensions, focusing on Brave's innovative approaches to enhance user protection and encourage broader research in web privacy.
Hardware Is the New Software - Finding Exploitable Bugs in Hardware Designs
Explore techniques for identifying and exploiting security vulnerabilities in hardware designs, focusing on RISC-V and OR1k CPU architectures using innovative tools and symbolic execution.
Stethoscope: Securely Configuring Devices without Systems Management
Discover Stethoscope, Netflix's open-source tool for secure device configuration. Learn how it guides users to improve security without administrative access, ideal for BYOD environments and third-party collaborations.